How to create a Temporary Access Pass using Logic Apps
Now that more and more organizations are moving towards passwordless, a Temporary Access Pass becomes indispensable for onboarding and recovery. Using Logic…

Now that more and more organizations are moving towards passwordless, a Temporary Access Pass becomes indispensable for onboarding and recovery. Using Logic…
As you may or may not know, most FIDO2 security keys can be set up with easy PINs like 1111 or 123456. Just like passwords, users tend to come up with…
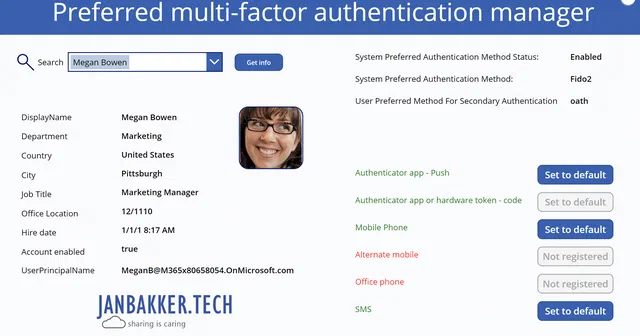
This post is all about setting the preferred multi-factor authentication method using Graph API. We already know the system-preferred multi-factor…
Company branding in Azure AD is a nice feature that allows administrators to prettify the sign-in experience for their end-users. It also comes with the…
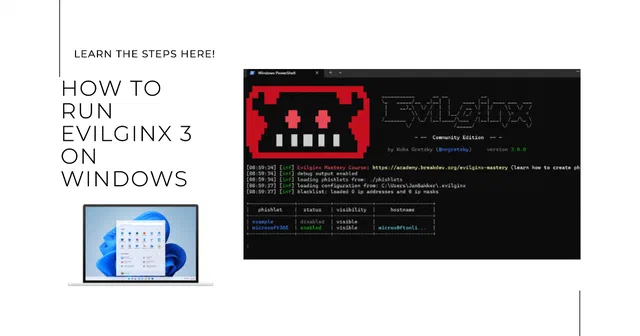
In case you missed it: Evilginx 3 was recently launched to the public. This release is a quality-of-life update and has many fixes and a few new features…
In this post, I will show you how you can integrate Azure AD's Authentication Context with Defender for Cloud Apps to require step-up authentication for…
I've done quite some Azure MFA projects over time (and counting), and as we mainly focus on the technical side, there are also practical sides to consider.…
That's the post for today. Just a bunch of sources with icons from Microsoft 365, Azure, Azure AD, and other Microsoft-related services. This can be super…
A new feature popped up in Azure AD. Well, not entirely new, I must say. Reading from the docs, Report Suspicious Activity is an enhancement of the Fraud Alert…
Microsoft released a new feature where the Outlook mobile app now has some of the Microsoft Authenticator App features onboard. Users can now enroll for Azure…
A new feature has popped up in Azure AD: System-preferred multifactor authentication (MFA). This will allow administrators to enforce the most secure method…
In this post, we look at managing Conditional Access policies and, in particular, duplicating existing policies. This can be super handy when you: