
KB - SelfServicePasswordReset write-back problem - error hr=80230818
This is a knowledgebase item. Hope it helps you out someday.
Now, since you landed on this page, I assume you’ve got the following issue:
- Azure AD SelfService Password Reset worked like a charm for quite some time.
- All of the sudden it stopped working, and you have no idea why. You have checked the permissions on the service account, and all looks good.
- You are in a hybrid setup, and use password write back. All checkmarks are green.
- Azure AD audit logs contain OnPremisesAdminActionRequired or ADAdminActionRequired as failure.
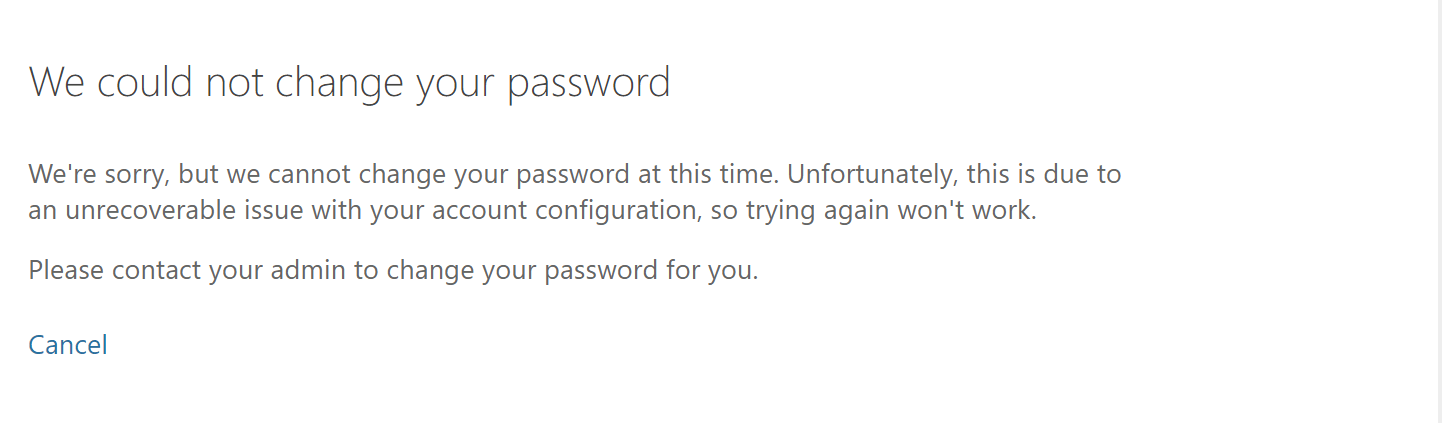
Your users are prompted with this error when trying to do a password reset using Azure AD Self Service Password Reset Portal.
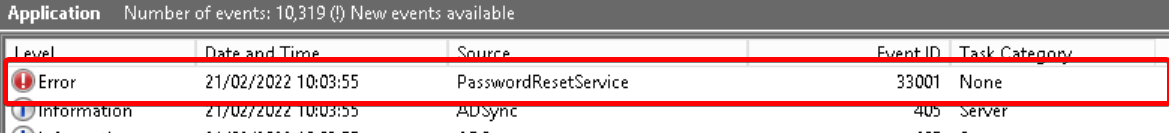
On your ADConnect server, you will find this event:
Synchronization Engine returned an error hr=80230818, message=The management agent run was terminated because a domain controller could not be contacted.Event ID: 33001
Source: PasswordResetService
TrackingId: xxxxxxxxxxxxxxxxxxxxxxxxxx, Reason: Synchronization Engine returned an error hr=80230818, message=The management agent run was terminated because a domain controller could not be contacted., Context: cloudAnchor:xxxxxxxxxxxxxxxxxxxxxxxxxx, SourceAnchorValue: xxxxxxxxxxxxxxxxxxx, UserPrincipalName: xxxxxxxxxxxxxxxxxxxxxxxx, Details: Microsoft.CredentialManagement.OnPremisesPasswordReset.Shared.PasswordResetException: Synchronization Engine returned an error hr=80230818, message=The management agent run was terminated because a domain controller could not be contacted.
   at AADPasswordReset.SynchronizationEngineManagedHandle.ThrowSyncEngineError(Int32 hr)
   at AADPasswordReset.SynchronizationEngineManagedHandle.ChangePassword(String cloudAnchor, String sourceAnchor, String oldPassword, String newPassword)
   at Microsoft.CredentialManagement.OnPremisesPasswordReset.PasswordResetCredentialManager.ChangePassword(String changePasswordXMLRequestString)
How to fix#
The fix is to use an FQDN format, instead of the NETBIOS name in your AD-Connect configuration.
Open the Synchronization Service Manager -> Connectors -> open the Active Directory Domain Services window -> Configure Directory Partitions -> and under “Domain controller connection settings” click configure you’ll see the list of DCs that ADConnect connects to and in which order. Make sure that your DC’s are formatted in a Fully Qualified Domain Name like “ DC01.domain.com”.
Stay safe!
Comments
Comments load when you scroll here.