Get started with passkeys in Microsoft 365
On this page
It’s here! A long-awaited feature in Microsoft 365 is finally there. Now, in public preview, organizations can add another phishing-resistant credential to their arsenal: device-bound passkeys.
DISCLAIMER: This feature is currently in public preview. Everything you read in this blog post is subject to change and may be outdated soon. Always check the current documentation on Microsoft Learn to keep track of changes. Images in this post might be slightly different in reality.
What is a device-bound passkey?#
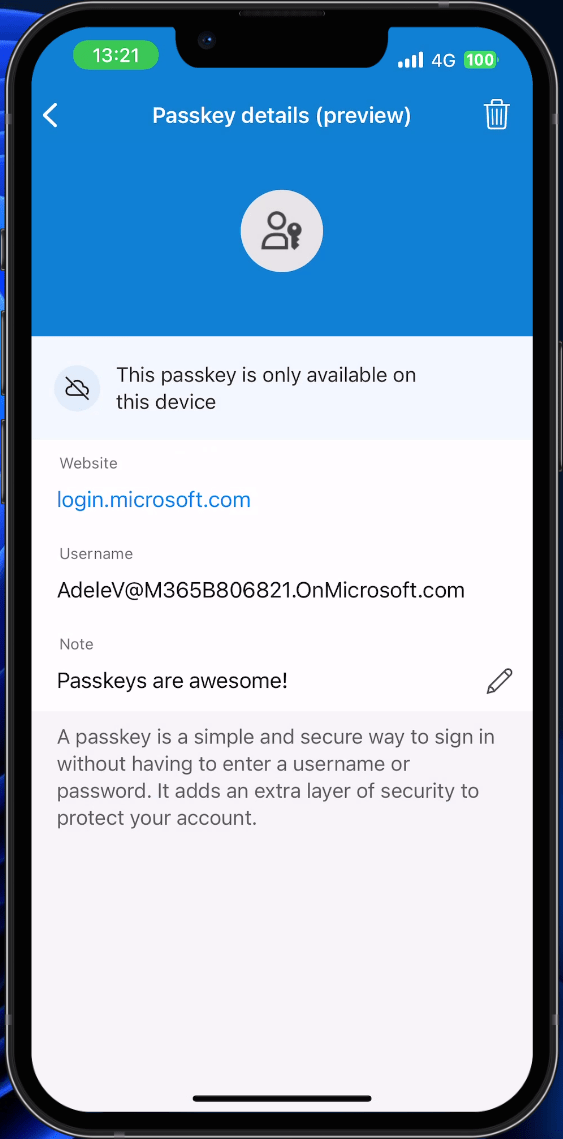
First, let’s have a clear understanding of the terminology. A device-bound passkey is a FIDO2 Discoverable Credential bound to a single authenticator. For example, FIDO2 security keys typically hold device-bound passkeys as the credential cannot leave the device. Device-bound passkeys have been previously referred to as single-device passkeys.
Translating this to Microsoft 365 means you can use a device-bound passkey in the Microsoft Authenticator app on iOS and Android to perform phishing-resistant authentication towards Microsoft 365 services and Entra ID-integrated applications. This credential will be bound to the device, the mobile phone, in this case.
Why do we want passkeys? Because MFA via push, TOTP, hardware OTP, and passwordless phone sign-in can be phished and will be phished for years and years to come. We’ve said goodbye to passwords (hopefully). Now, it’s time to take the next step.
How to prepare for passkeys?#
In a previous blog post, I explained how you, as an admin, could prepare for the landing of passkeys. This is also explained in the announcement in Microsoft 365 admin center » Message center:
For your organization to opt-in to this preview, you will need to enforce key restrictions to allow specified passkey providers in your FIDO2 policy. Here are the possible configuration states for FIDO2 key restrictions during the preview:
- No key restrictions (FIDO2 policy default): Tenant allows all security key models. Device-bound passkey providers on computers and mobile devices are not allowed.
- Key restrictions set to “Allow”: Tenant only allows the explicitly added AAGUIDs. To enable a device-bound passkey provider, add their AAGUID(s) to the key restrictions list.
- Key restrictions set to “Block”: Tenant blocks the explicitly added AAGUIDs and allows all other security key models. Device-bound passkey providers on computers and mobile devices are not allowed.
If you already use FIDO2 security keys, make sure you do an inventory of your current AAGUIDs so you can add them next to the device-bound passkeys. Many organizations use FIDO2 security keys for emergency break-glass admin accounts, so make sure you’re not breaking that procedure. Read more: Prepare for passkeys in Entra ID! - JanBakker.tech
Prerequisites#
To support passkeys in Microsoft 365, please have the following requirements in place:
- It’s recommended to migrate your legacy policies for SSPR and MFA methods to the new unified policy for managing authentication methods. This will make your life easier. Learn more.
- The users should have already been enrolled for multi-factor authentication, or you will need a Temporary Access Pass to enroll passkeys.
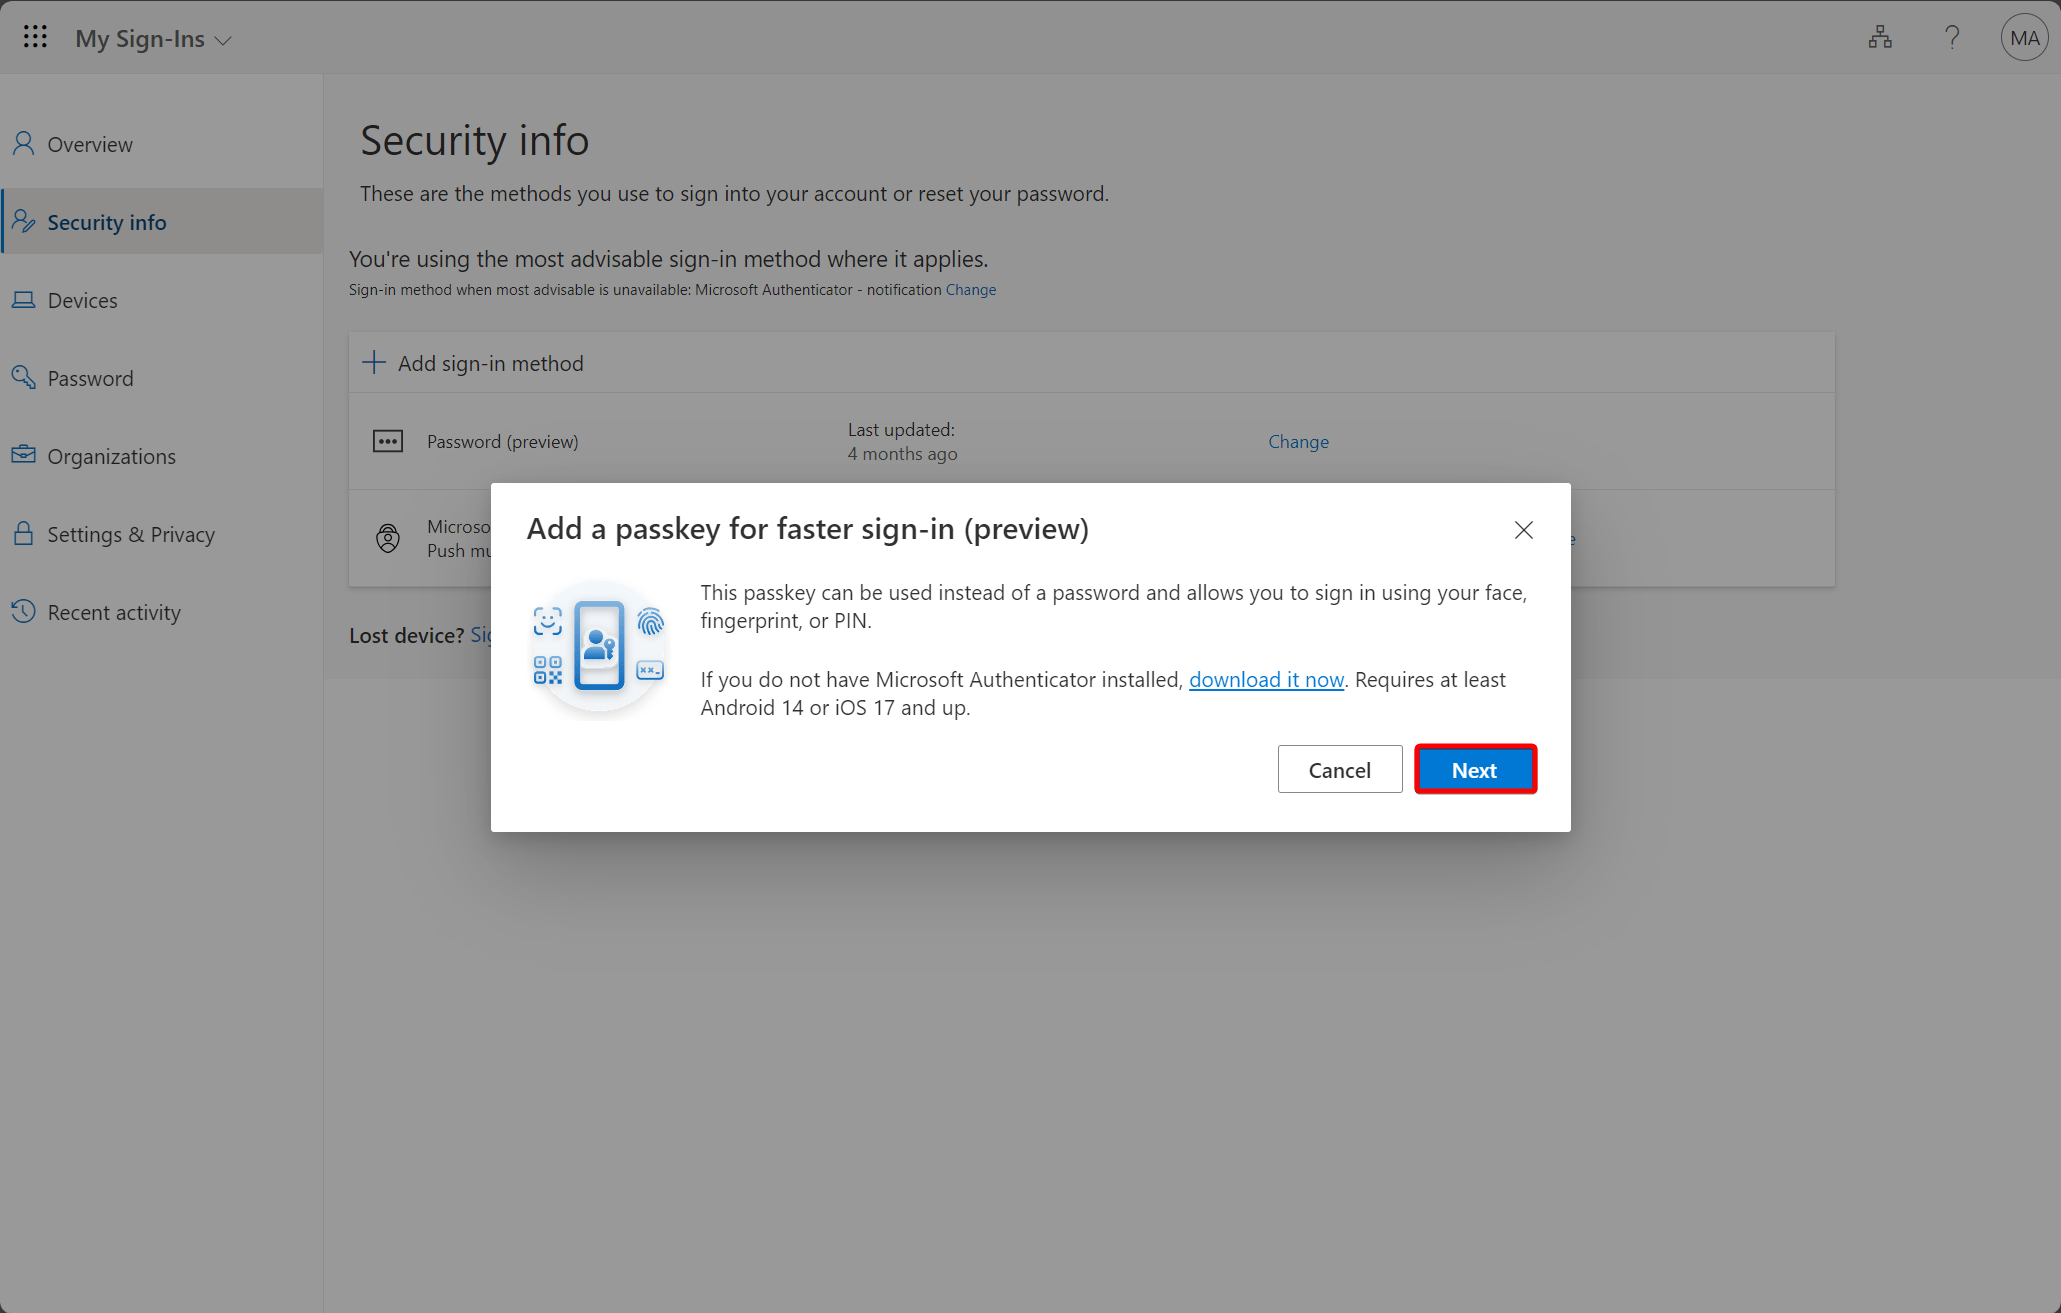
- Passkeys require Android 14 or iOS 17 and up.
- Microsoft Authenticator App on Android should be 6.2404.2444 or newer.
- Microsoft Authenticator App on iOS should be version 6.8.7 or newer.
- The “Usage data” (under Settings) should be enabled from the Microsoft Authenticator App.
- For Android, the Authenticator app should be enabled as an additional provider under Settings -> Passwords and accounts. (user will be guided during enrollment)
- For iOS, the Microsoft Authenticator app should be enabled for AutoFill under Settings -> Passwords -> Password options.(user will be guided during enrollment)
- For cross-device sign-in, both the mobile phone and the device from which you sign-in should have Bluetooth enabled.
- If you already use FIDO2 security keys, make sure you do an inventory of your current AAGUIDs so you can add them next to the device-bound passkeys, as stated earlier. Don’t lock yourself out.
One important note for Apple iPhone users: There is currently a limitation by Apple, so you can only use one password manager next to the iCloud keychain for AutoFill. Enabling the Microsoft Authenticator for AutoFill will disable any existing password manager.
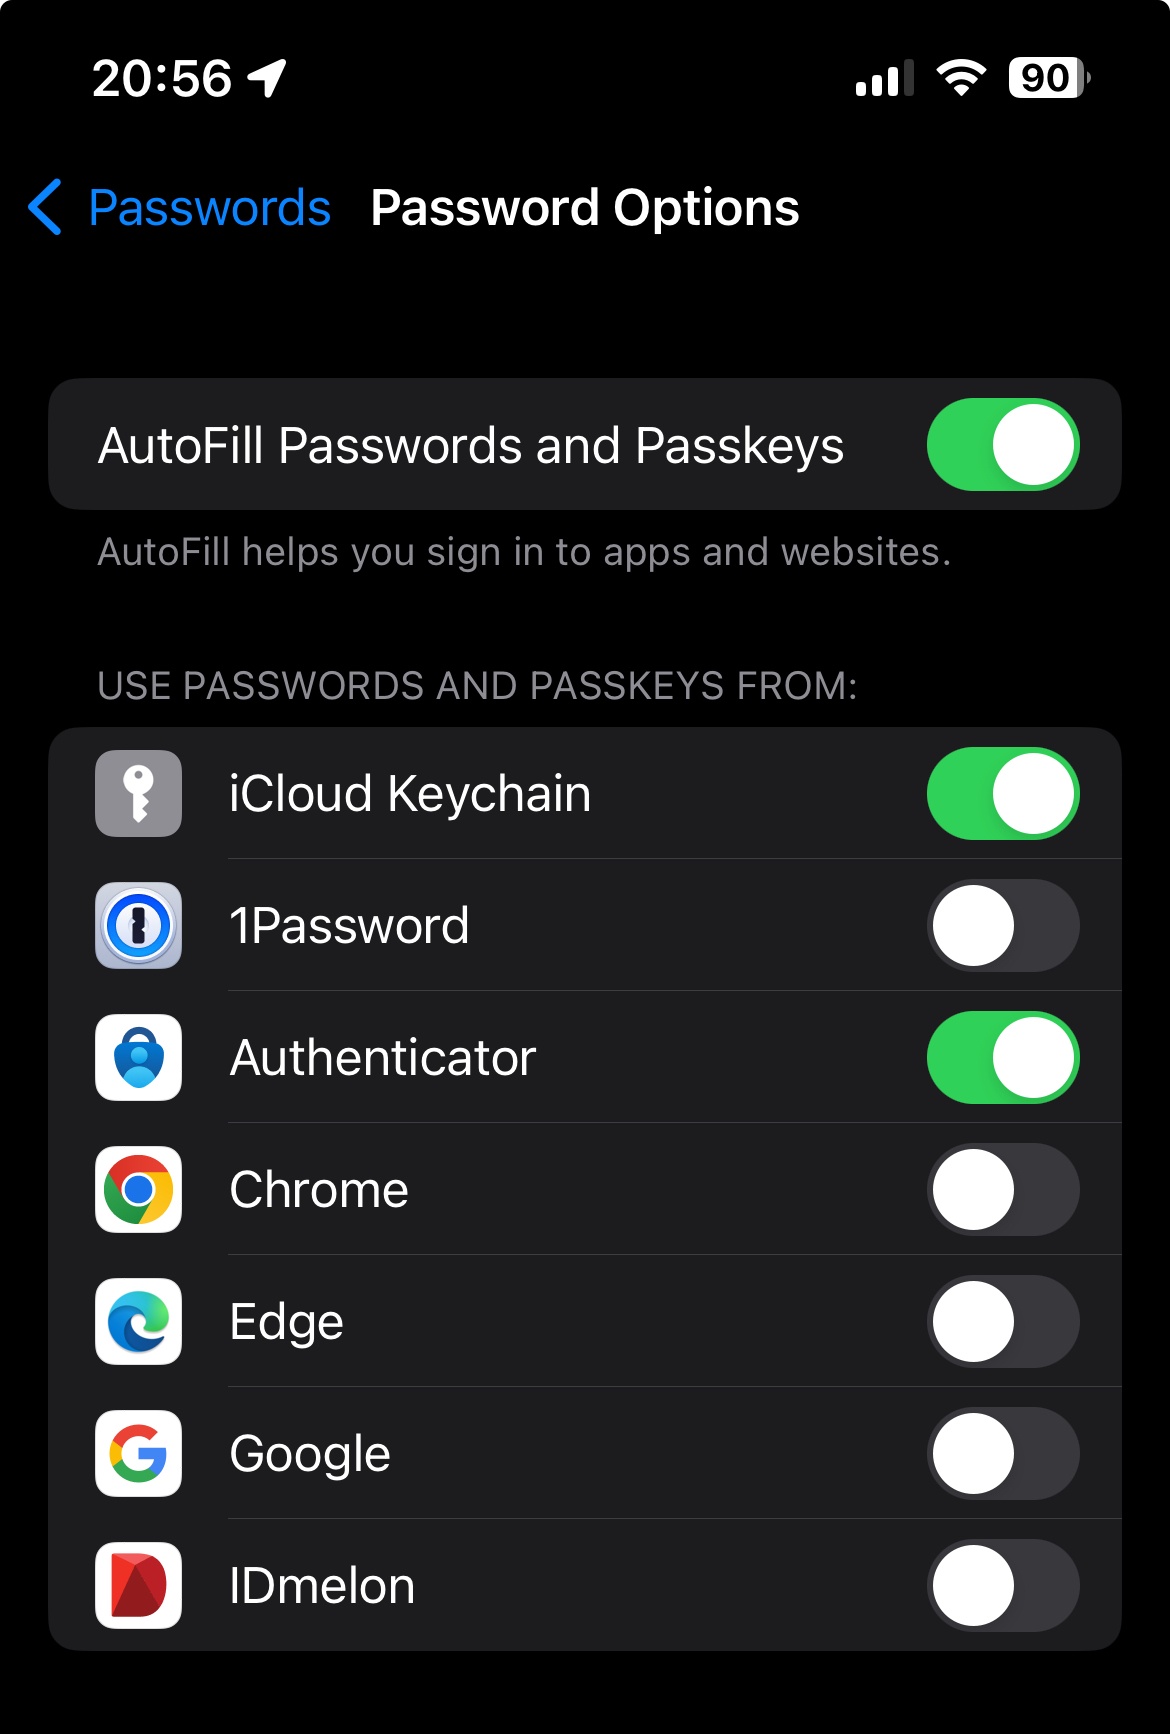
Please consider reporting this to Apple by sharing feedback.
Feedback - iPhone - Apple
You can use this sample text, created by Fabian Bader:\
Dear Tim Apple,
Please allow an unlimited number or at least three passkey providers in the next minor iOS release to comply with the Digital Markets Act, and to make your users happy.
Thank you in advance
How to enable device-bound passkeys in Microsoft 365 / Entra ID#
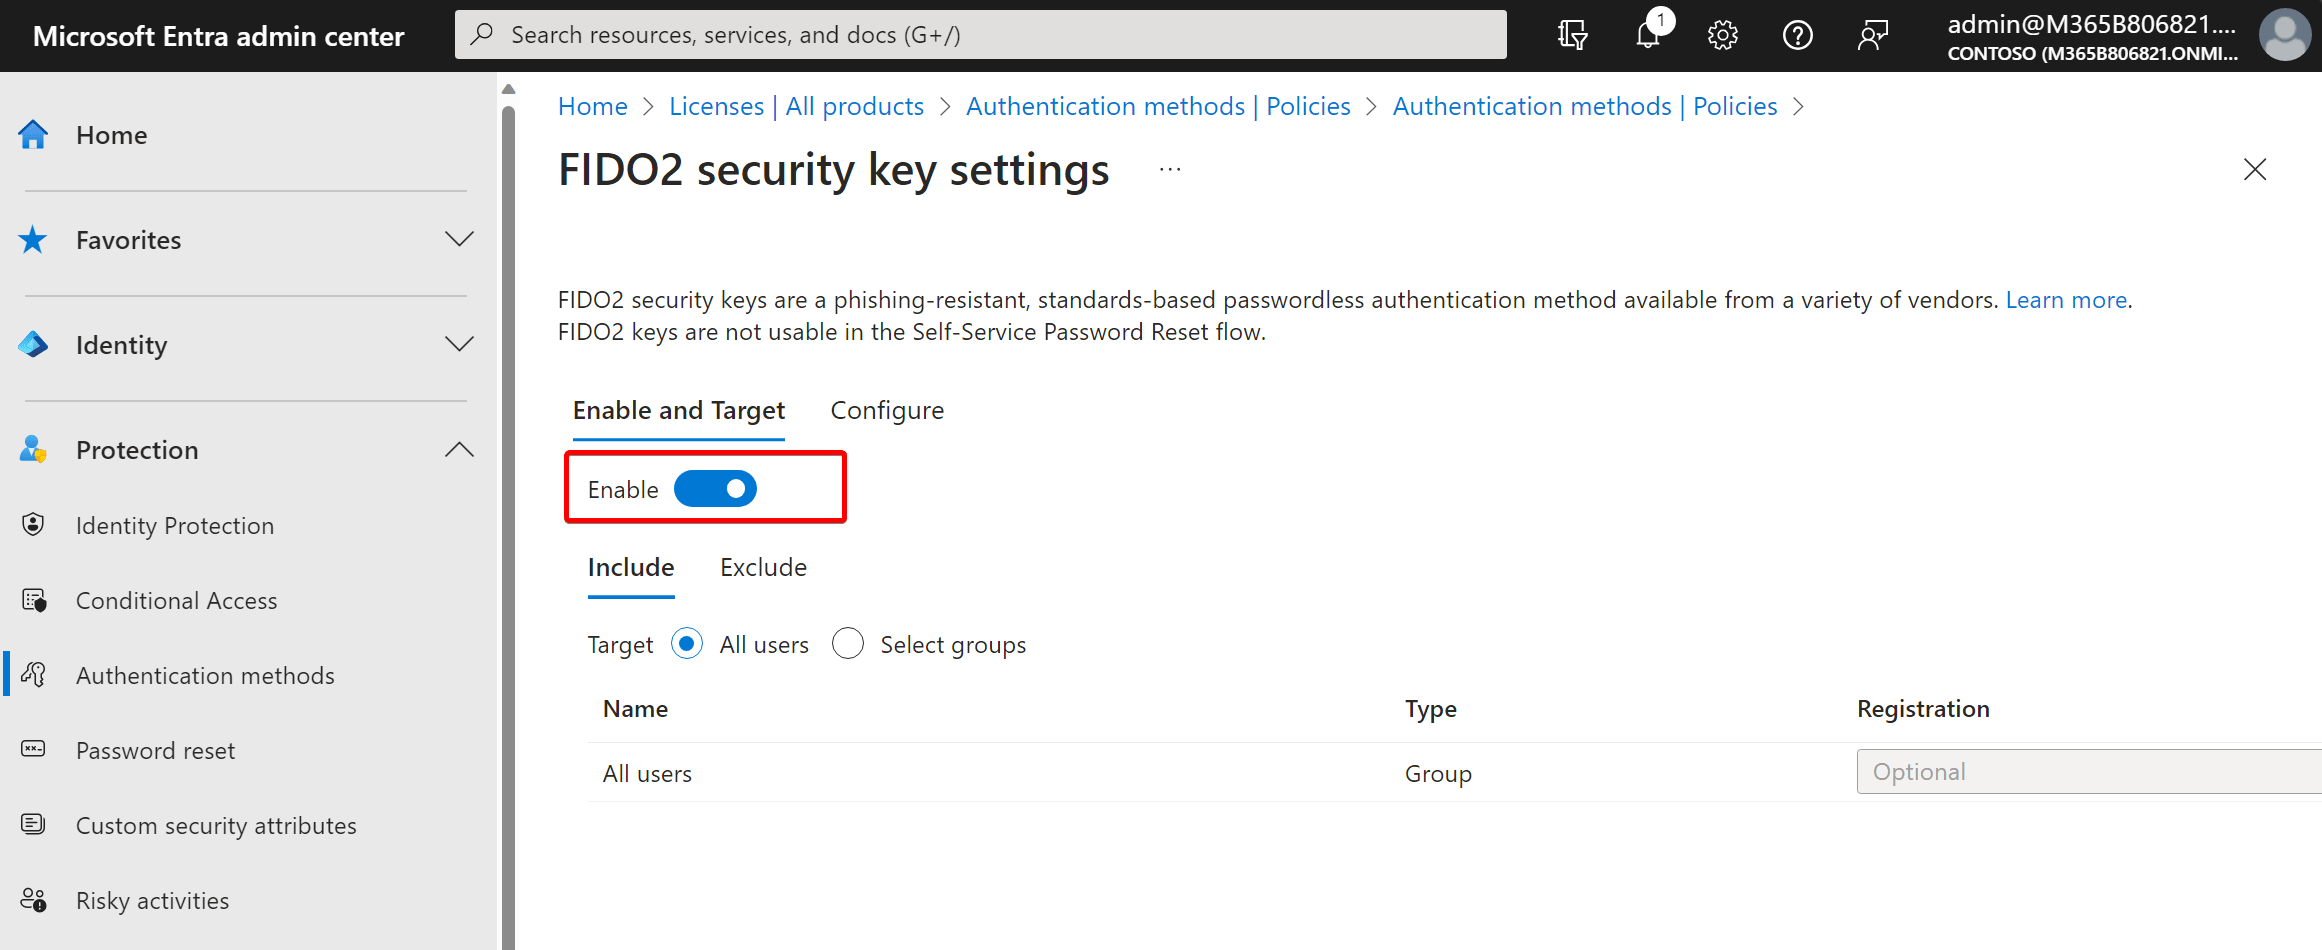
The easiest way to enable device-bound passkeys is by using the Entra admin center. Navigate to Protection -> Authentication methods, and select Policies. Find the Passkey (FIDO2) policy and enable the policy for all users or a select group of users.
Next, go to the Configure tab.
- Set “Enforce attestation” to “No”.
- Set “Enforce key restrictions” to “Yes”.
- Set “Restrict specific keys” to “Allow” and enter the AAGUIDs of the device-bound passkeys, and the existing FIDO2 security keys you support, and save the configuration.
| iOS Microsoft Authenticator | 90a3ccdf-635c-4729-a248-9b709135078f |
|---|---|
| Android Microsoft Authenticator | de1e552d-db1d-4423-a619-566b625cdc84 |
*AAGUIDs for device-bound passkeys in Microsoft Authenticator App*
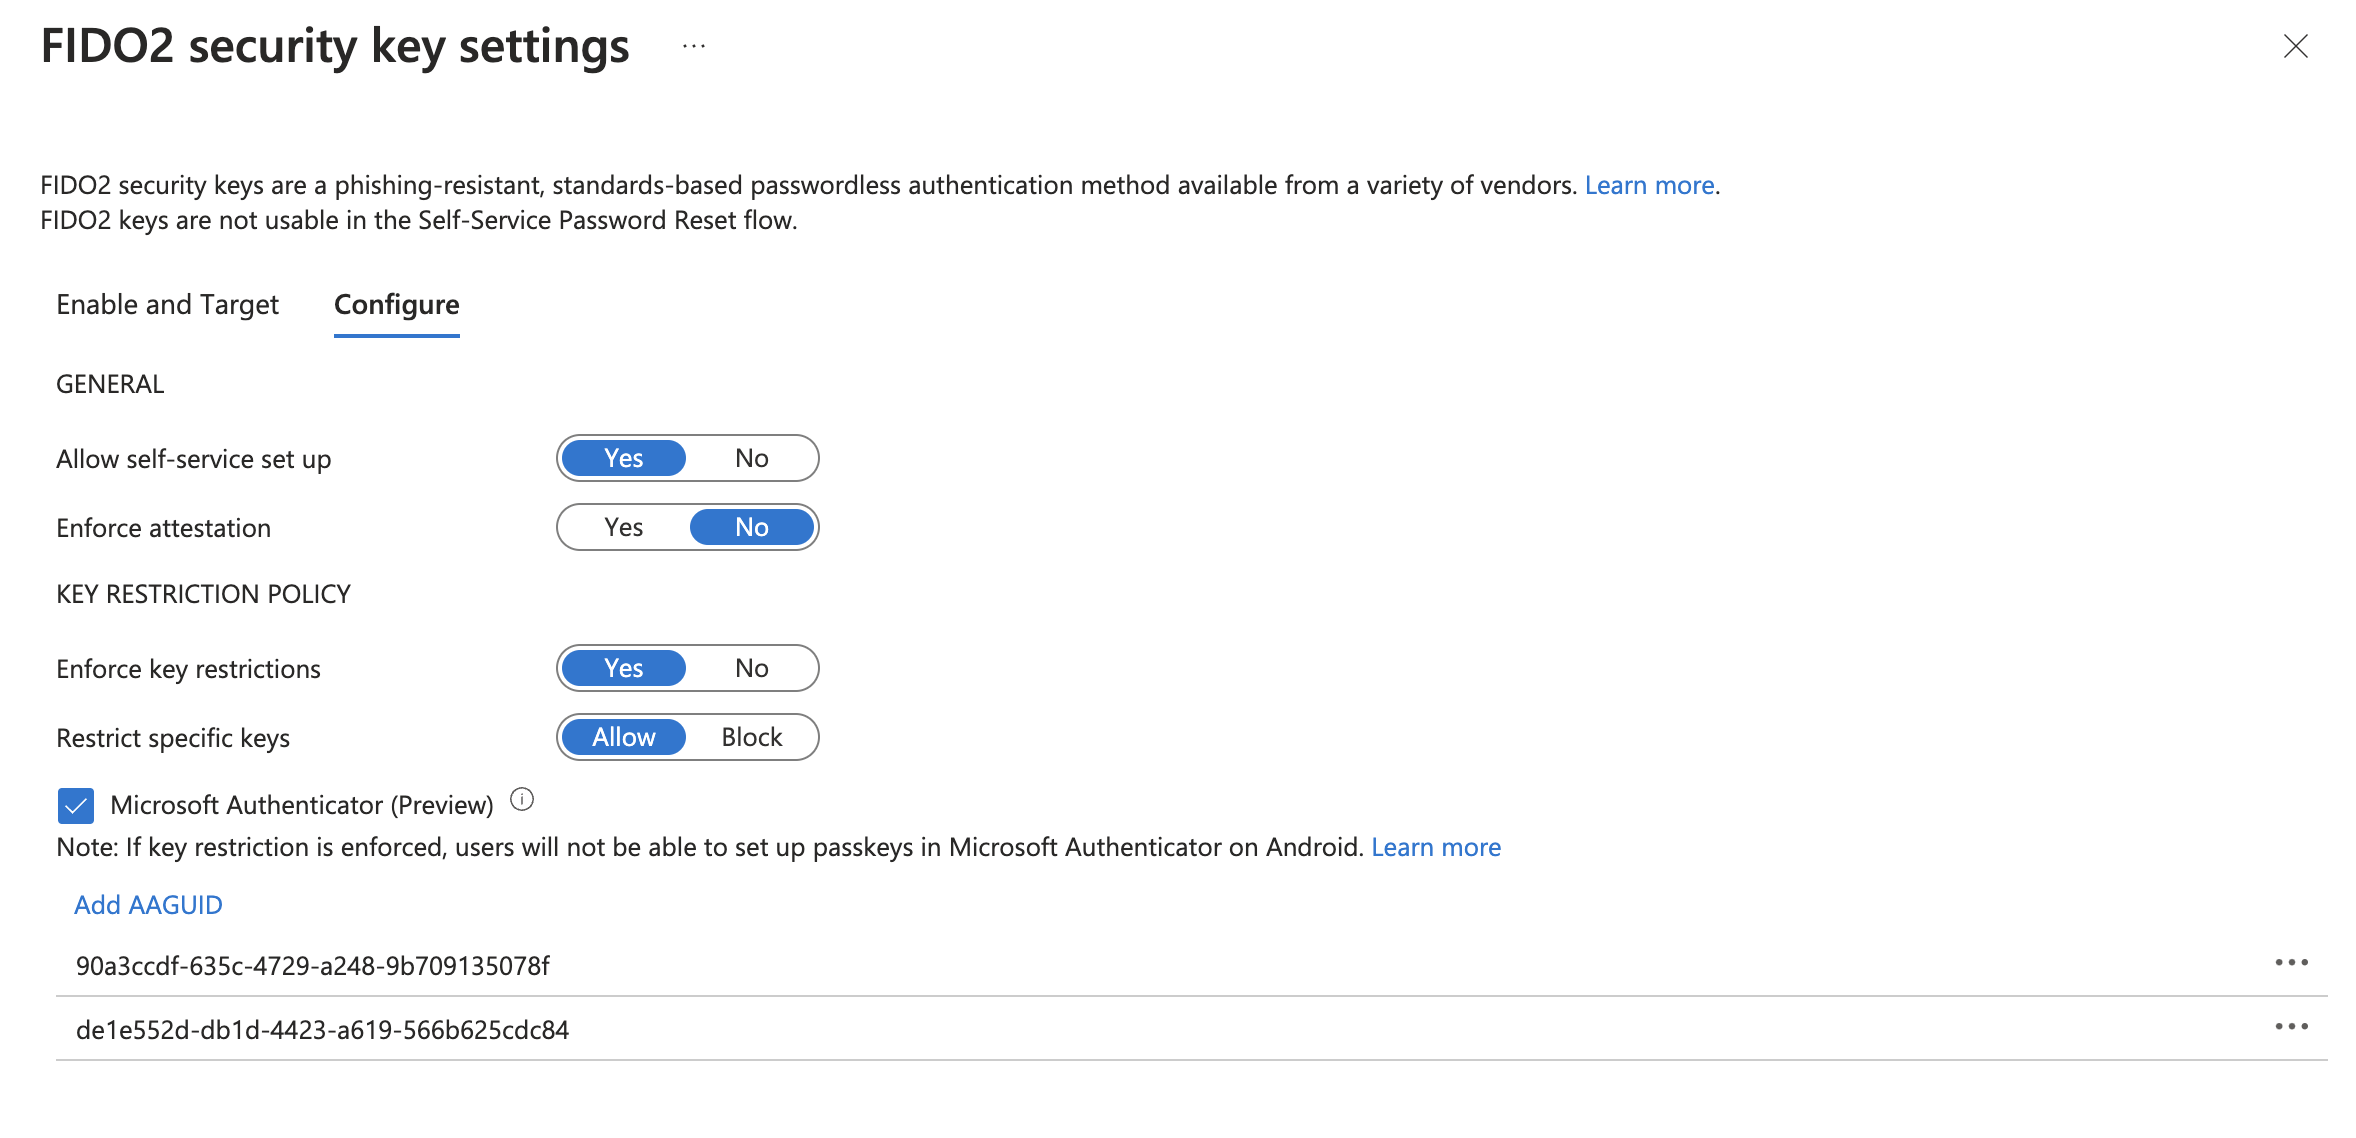
Some interfaces may also show a checkbox for the Microsoft Authenticator app. You can use that one to allow both iOS and Android. If you want to support either one, use the AAGUIDs.
Please find this community-driven list of known passkey provider AAGUIDs. (Thanks to Ru Campbell (@rucam365) / X (twitter.com)) I assume these providers will get supported in Entra over time. For now, only device-bound passkeys are supported.
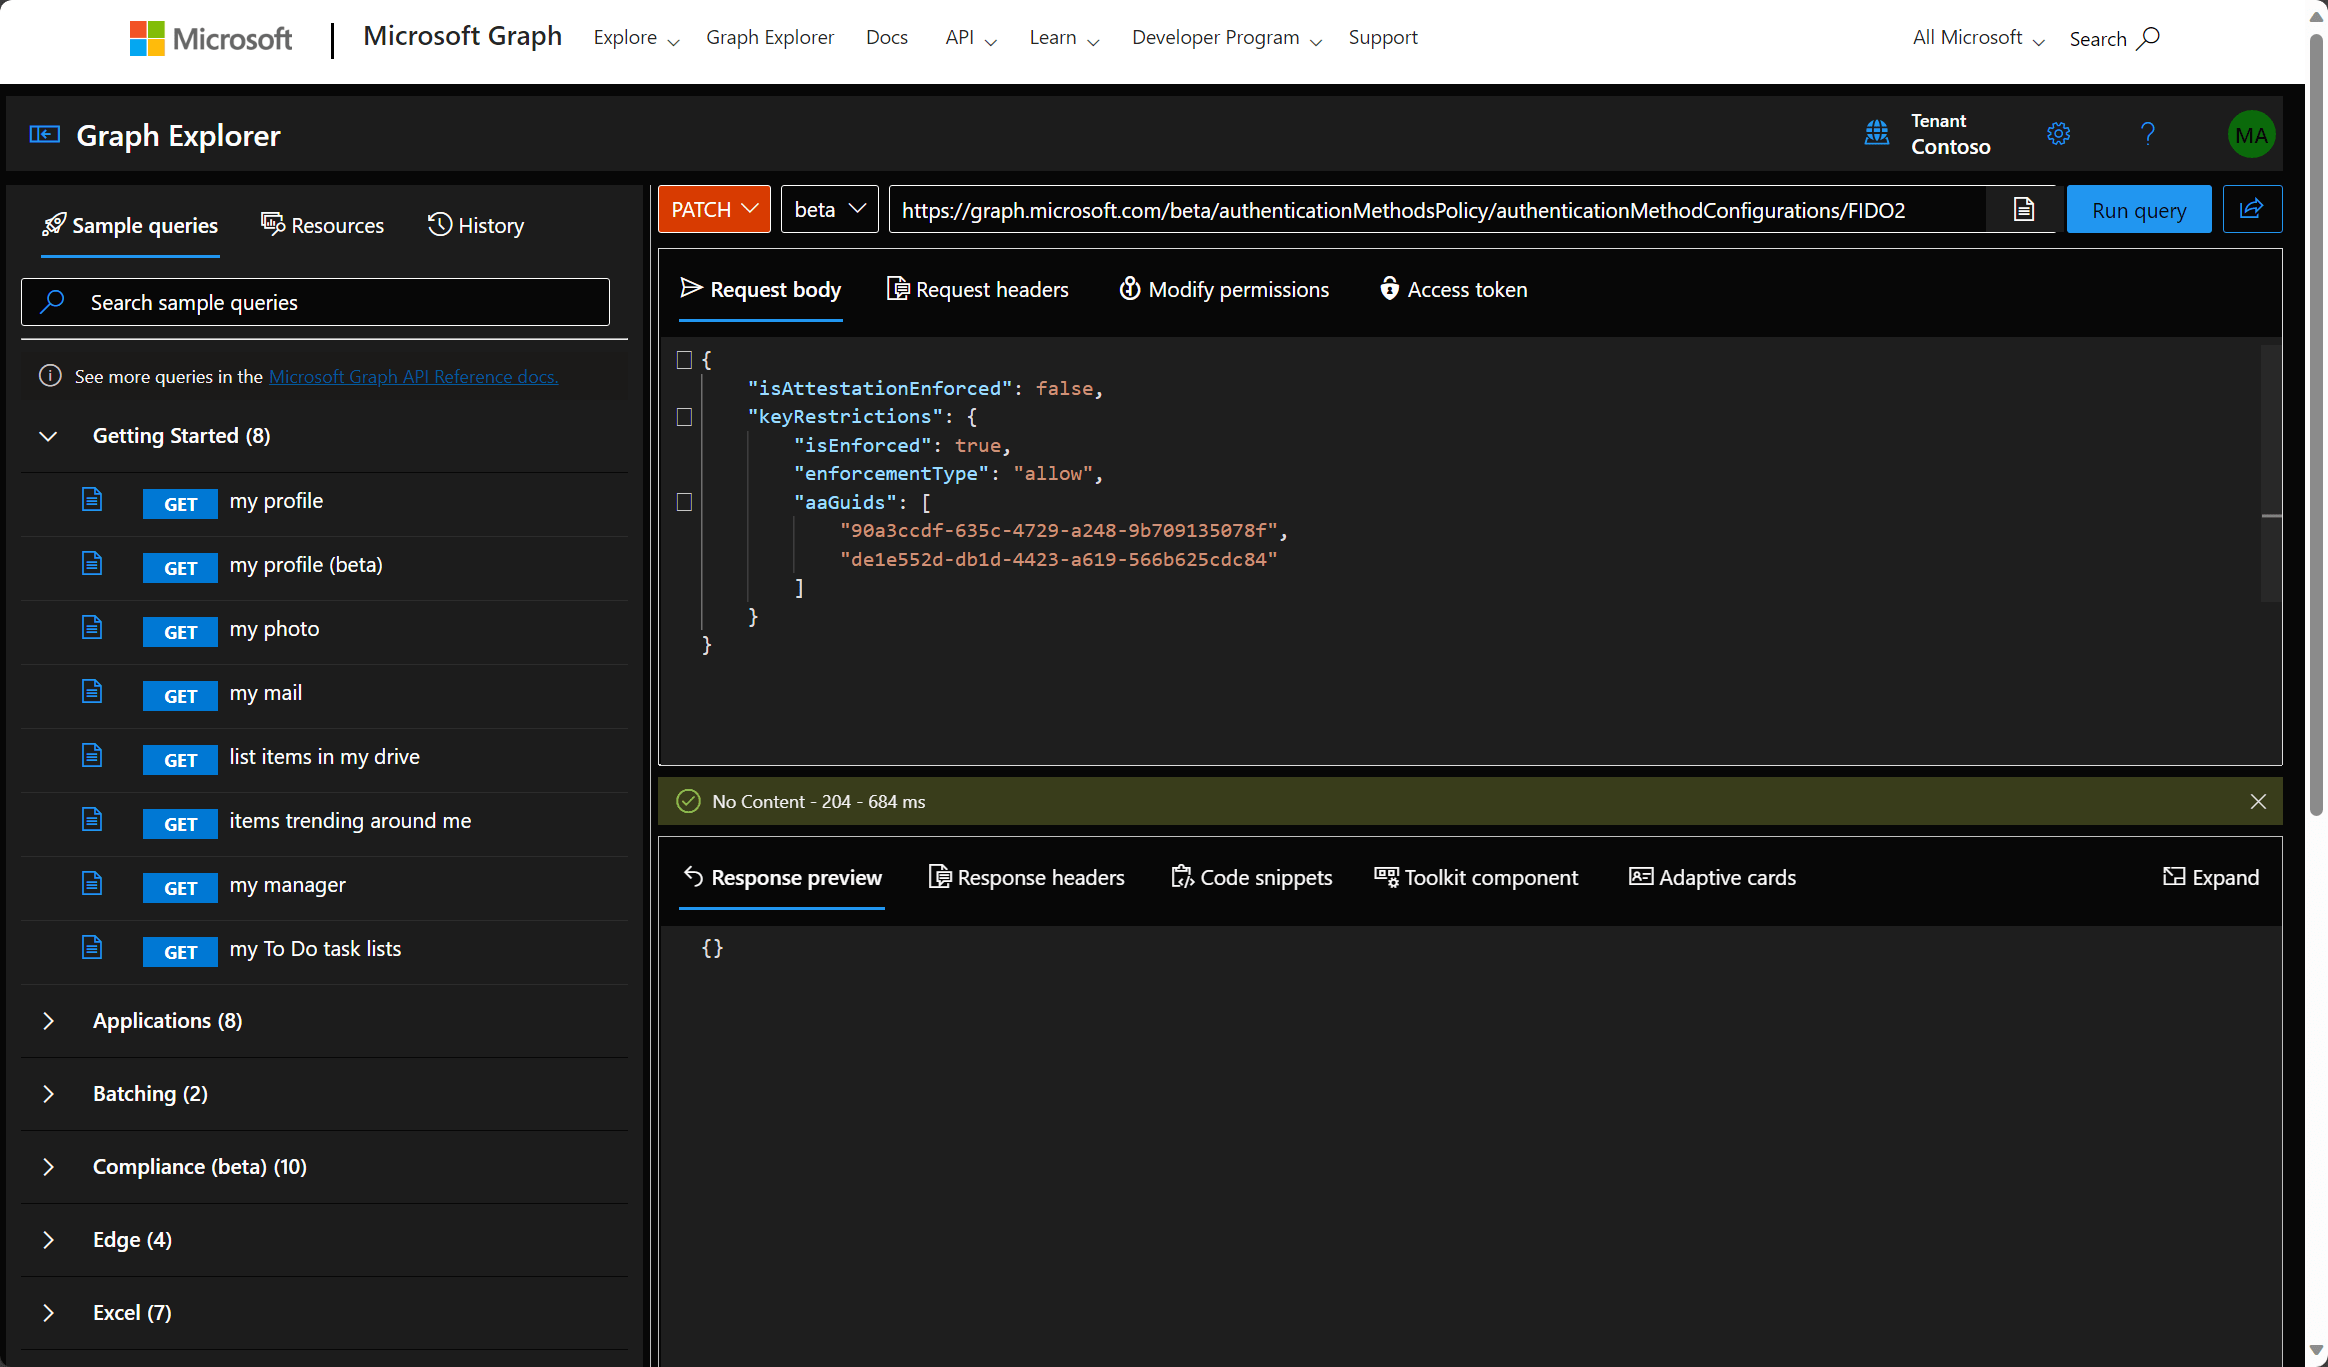
You can also use Graph API to update the policies. Please make a copy of your existing configuration first because AAGUIDs may be overwritten.
Navigate to Graph Explorer and ensure that you’ve consented to the Policy.Read.All and Policy.ReadWrite.AuthenticationMethod permissions.
Use the following URI to see the current configuration of the FIDO2 policy:
GET https://graph.microsoft.com/beta/authenticationMethodsPolicy/authenticationMethodConfigurations/FIDO2To enable Passkeys for iOS and Android on the Authenticator App, use the following request:
PATCH

https://graph.microsoft.com/beta/authenticationMethodsPolicy/authenticationMethodConfigurations/FIDO2

{
    "isAttestationEnforced": false,
    "keyRestrictions": {
        "isEnforced": true,
        "enforcementType": "allow",
        "aaGuids": [
            "90a3ccdf-635c-4729-a248-9b709135078f",
            "de1e552d-db1d-4423-a619-566b625cdc84"
        ]
    }
}
End-user experience - Passkey enrollment on iOS#
I’m the proud owner of an iPhone so I can show you that side of the party. Go find a proud Android owner to see how that rolls. I assume it would be pretty similar.
First, sign in to https://aka.ms/mysecurityinfo with some form of MFA. This can be an existing MFA method or a Temporary Acces Pass. Add a new sign-in method. Pick Passkey in Microsoft Authenticator (preview).
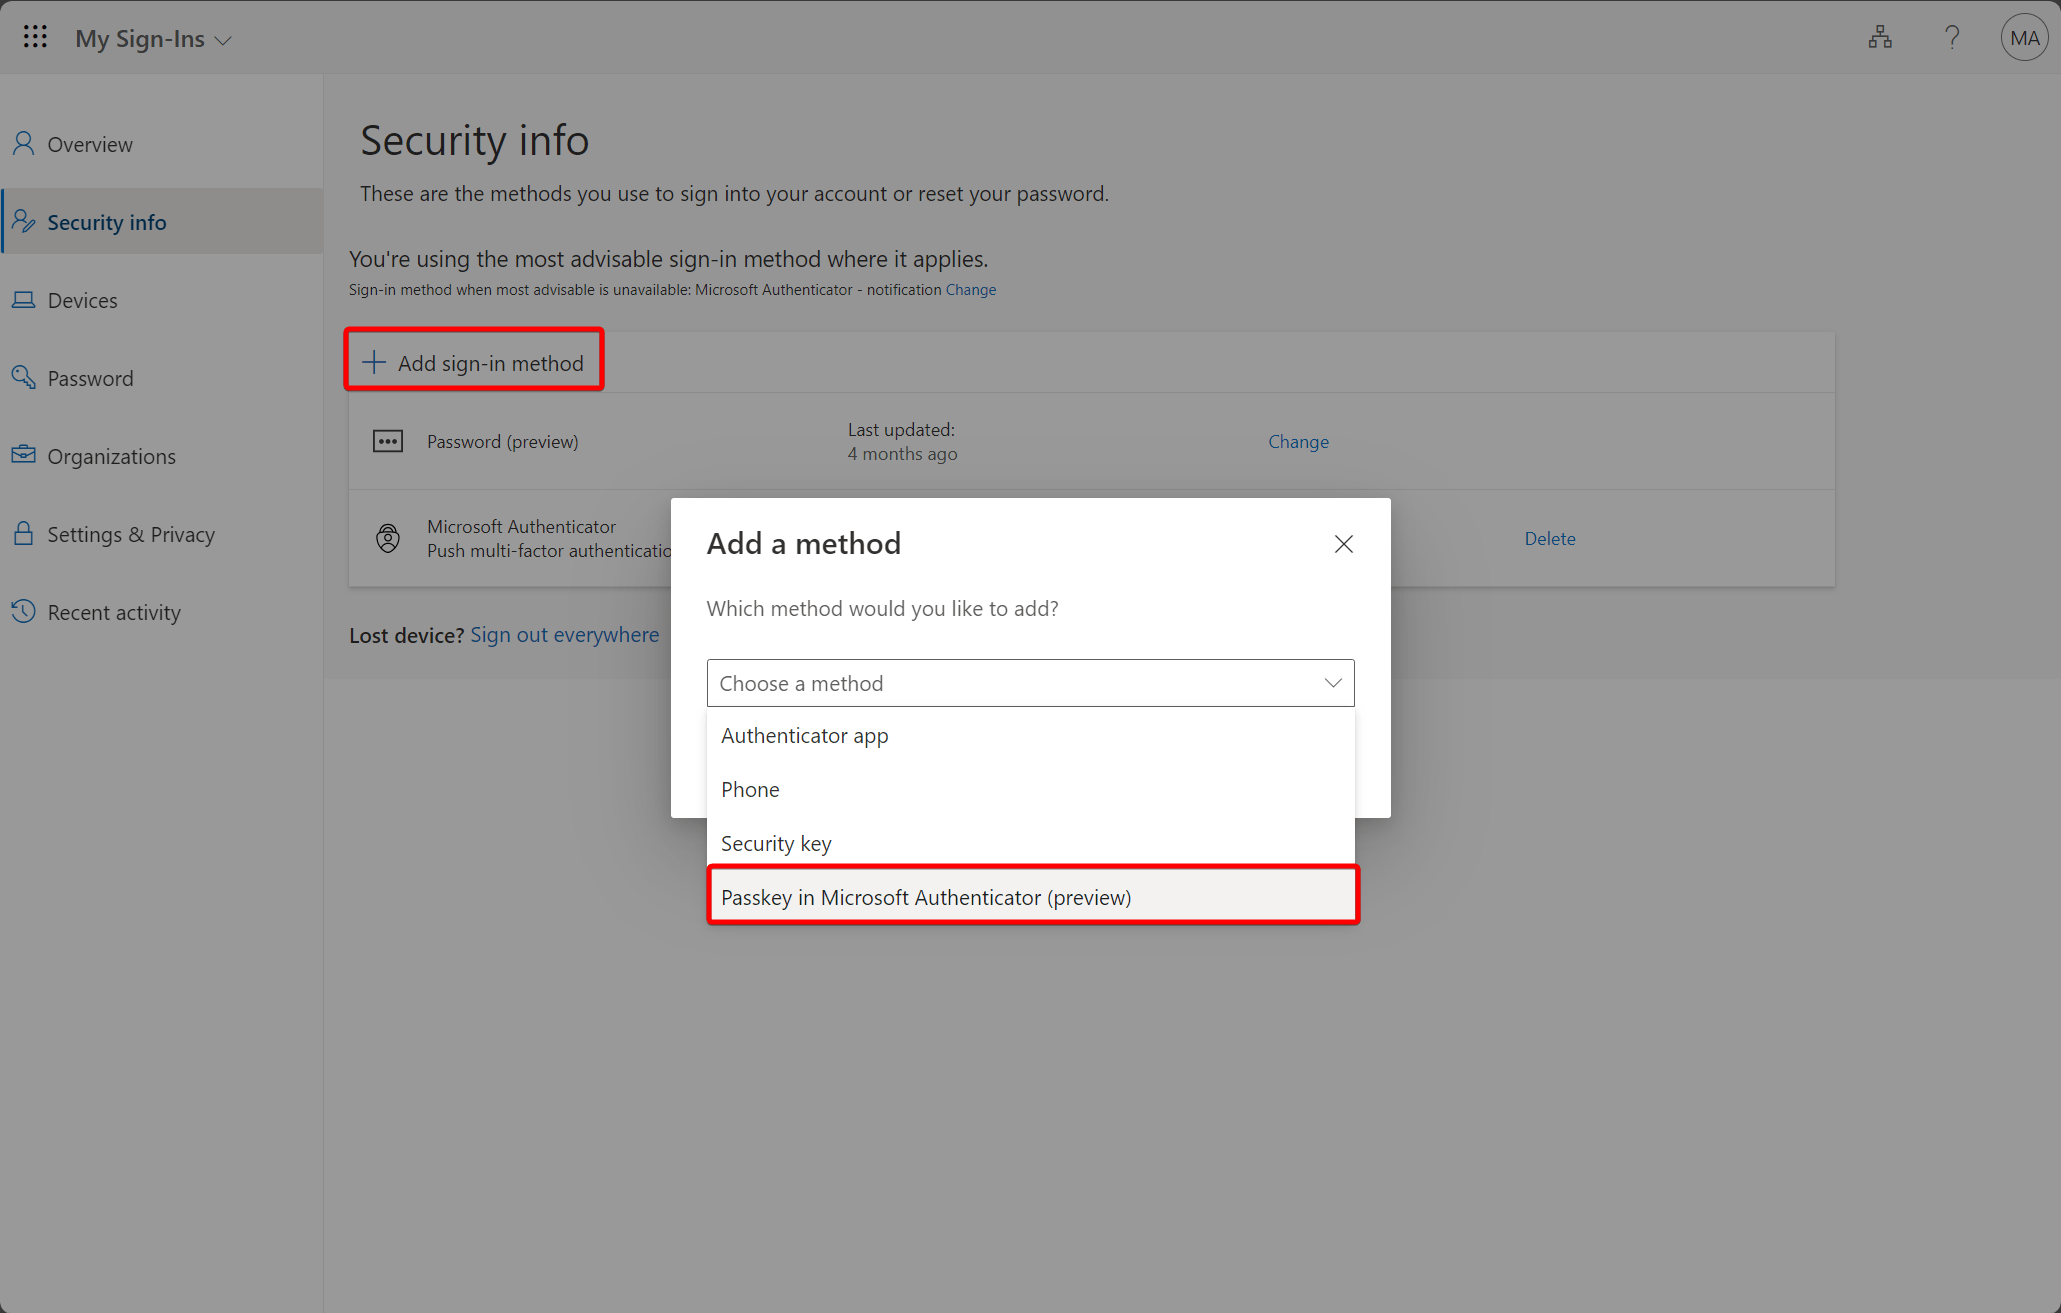
Make sure you have installed the latest version of the Microsoft Authenticator App. Then, click Next.
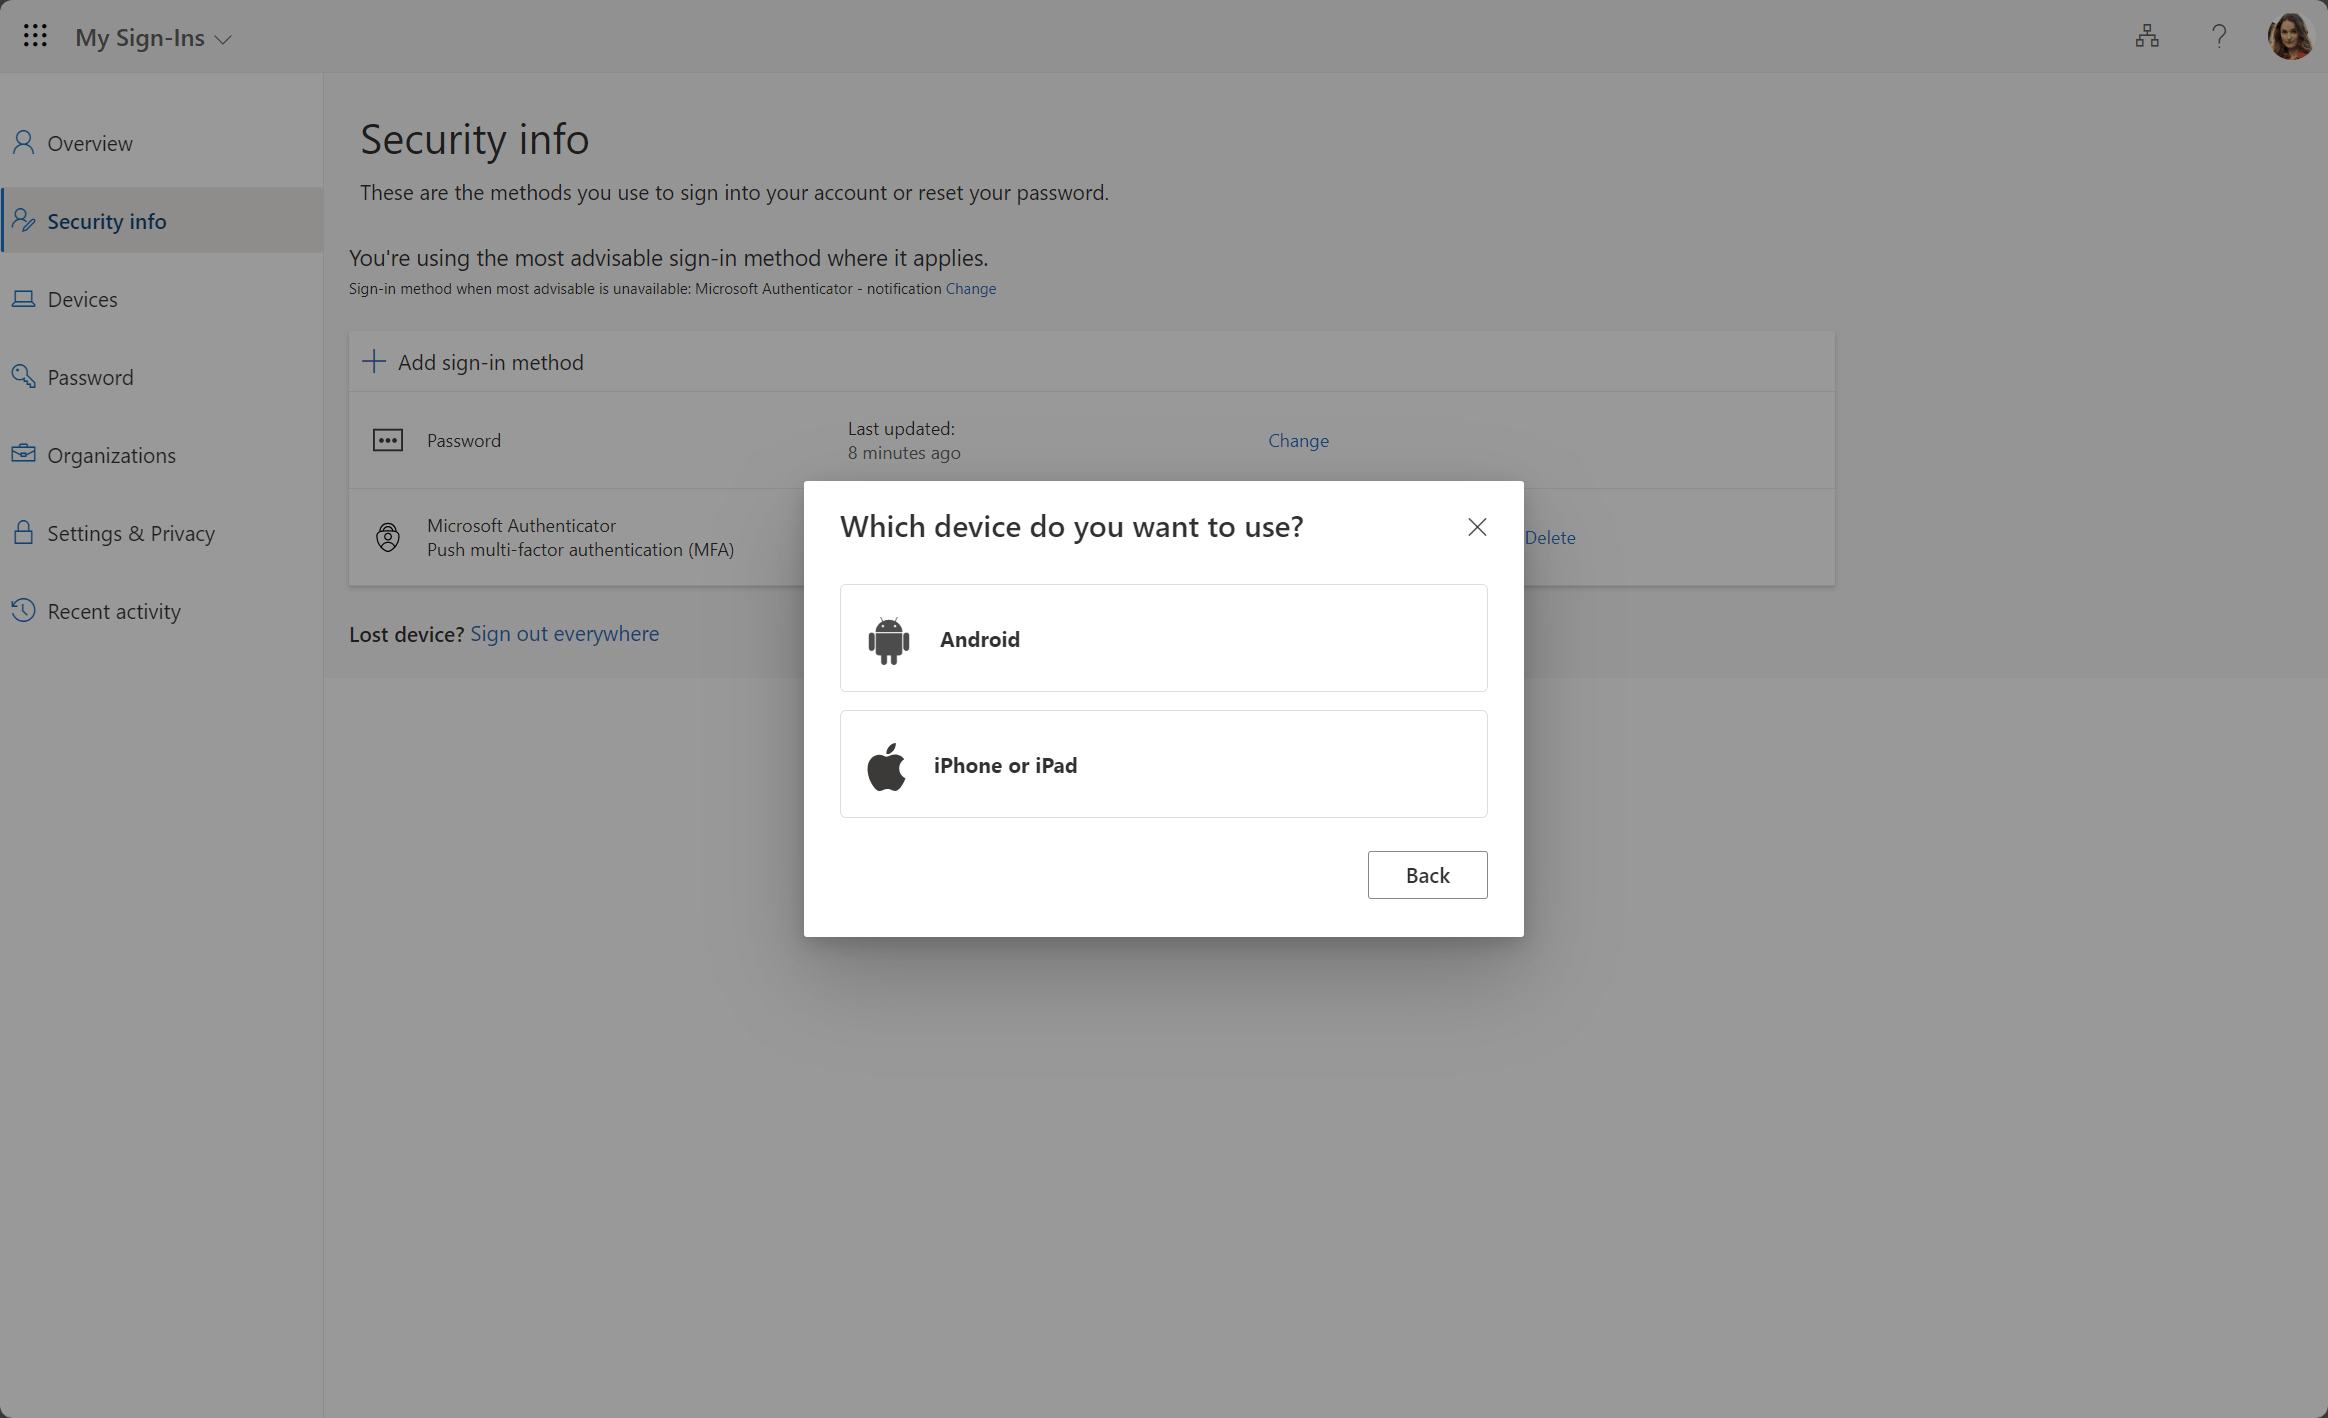
Now, pick your mobile operation system. As said, from here, it might be slightly different, but overall, this should work the same for Android users.
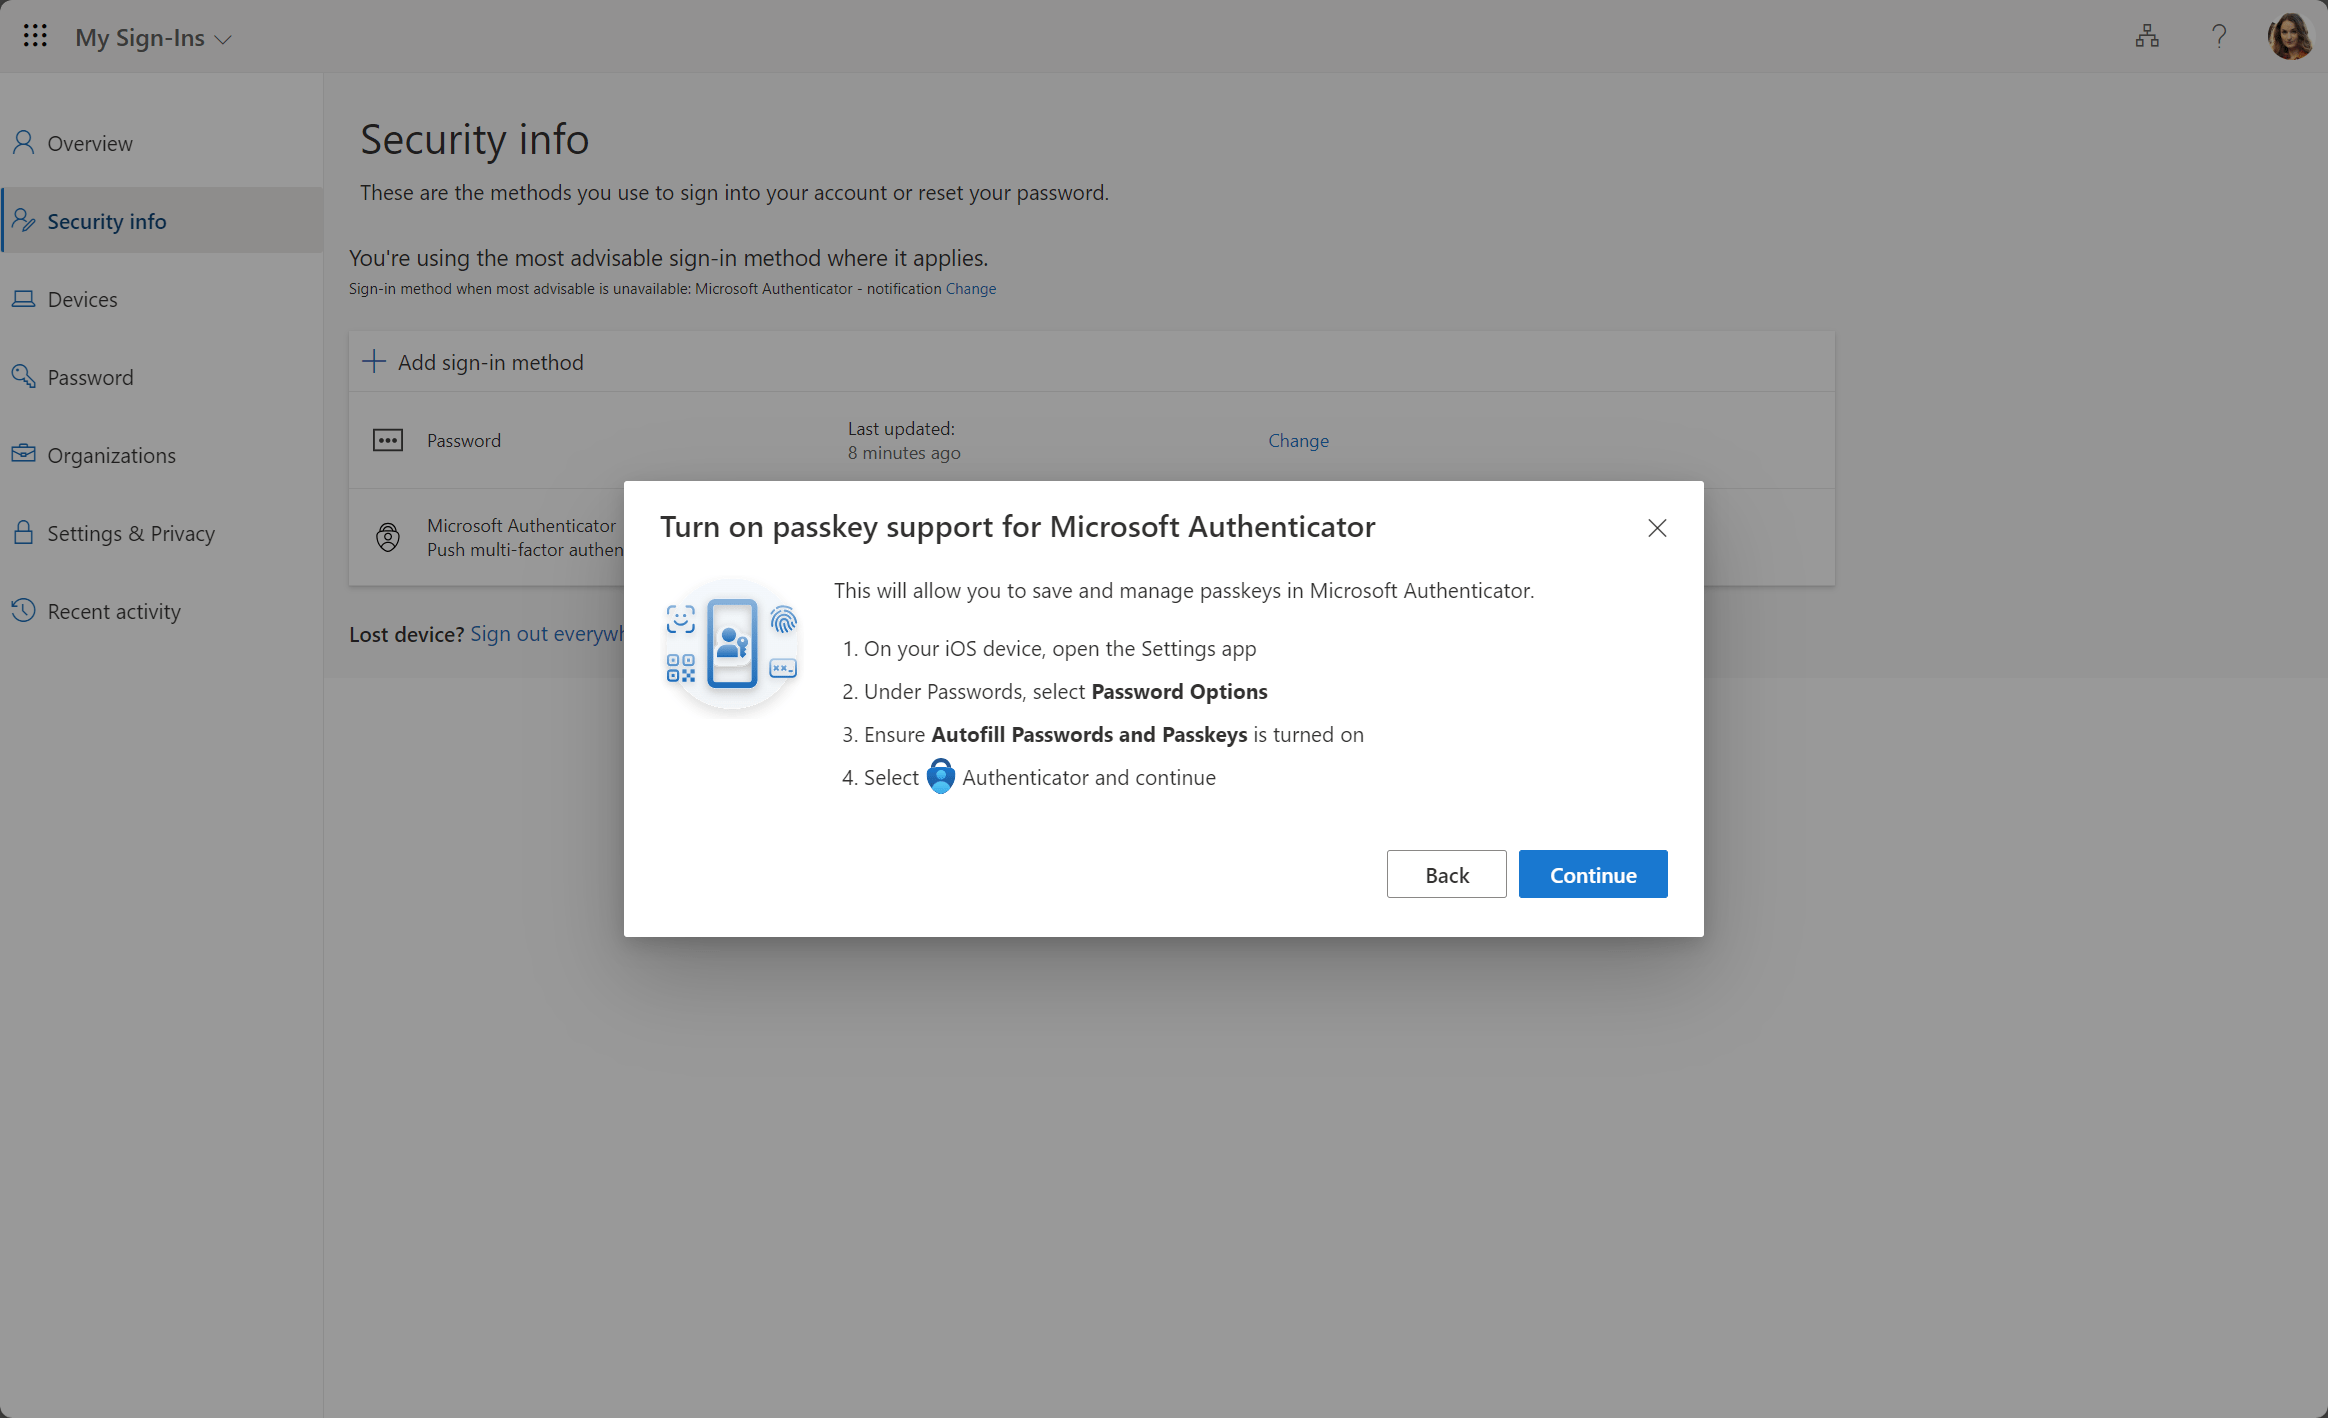
Make sure Autofill Passwords and Passkey is enabled from the iOS system password settings.
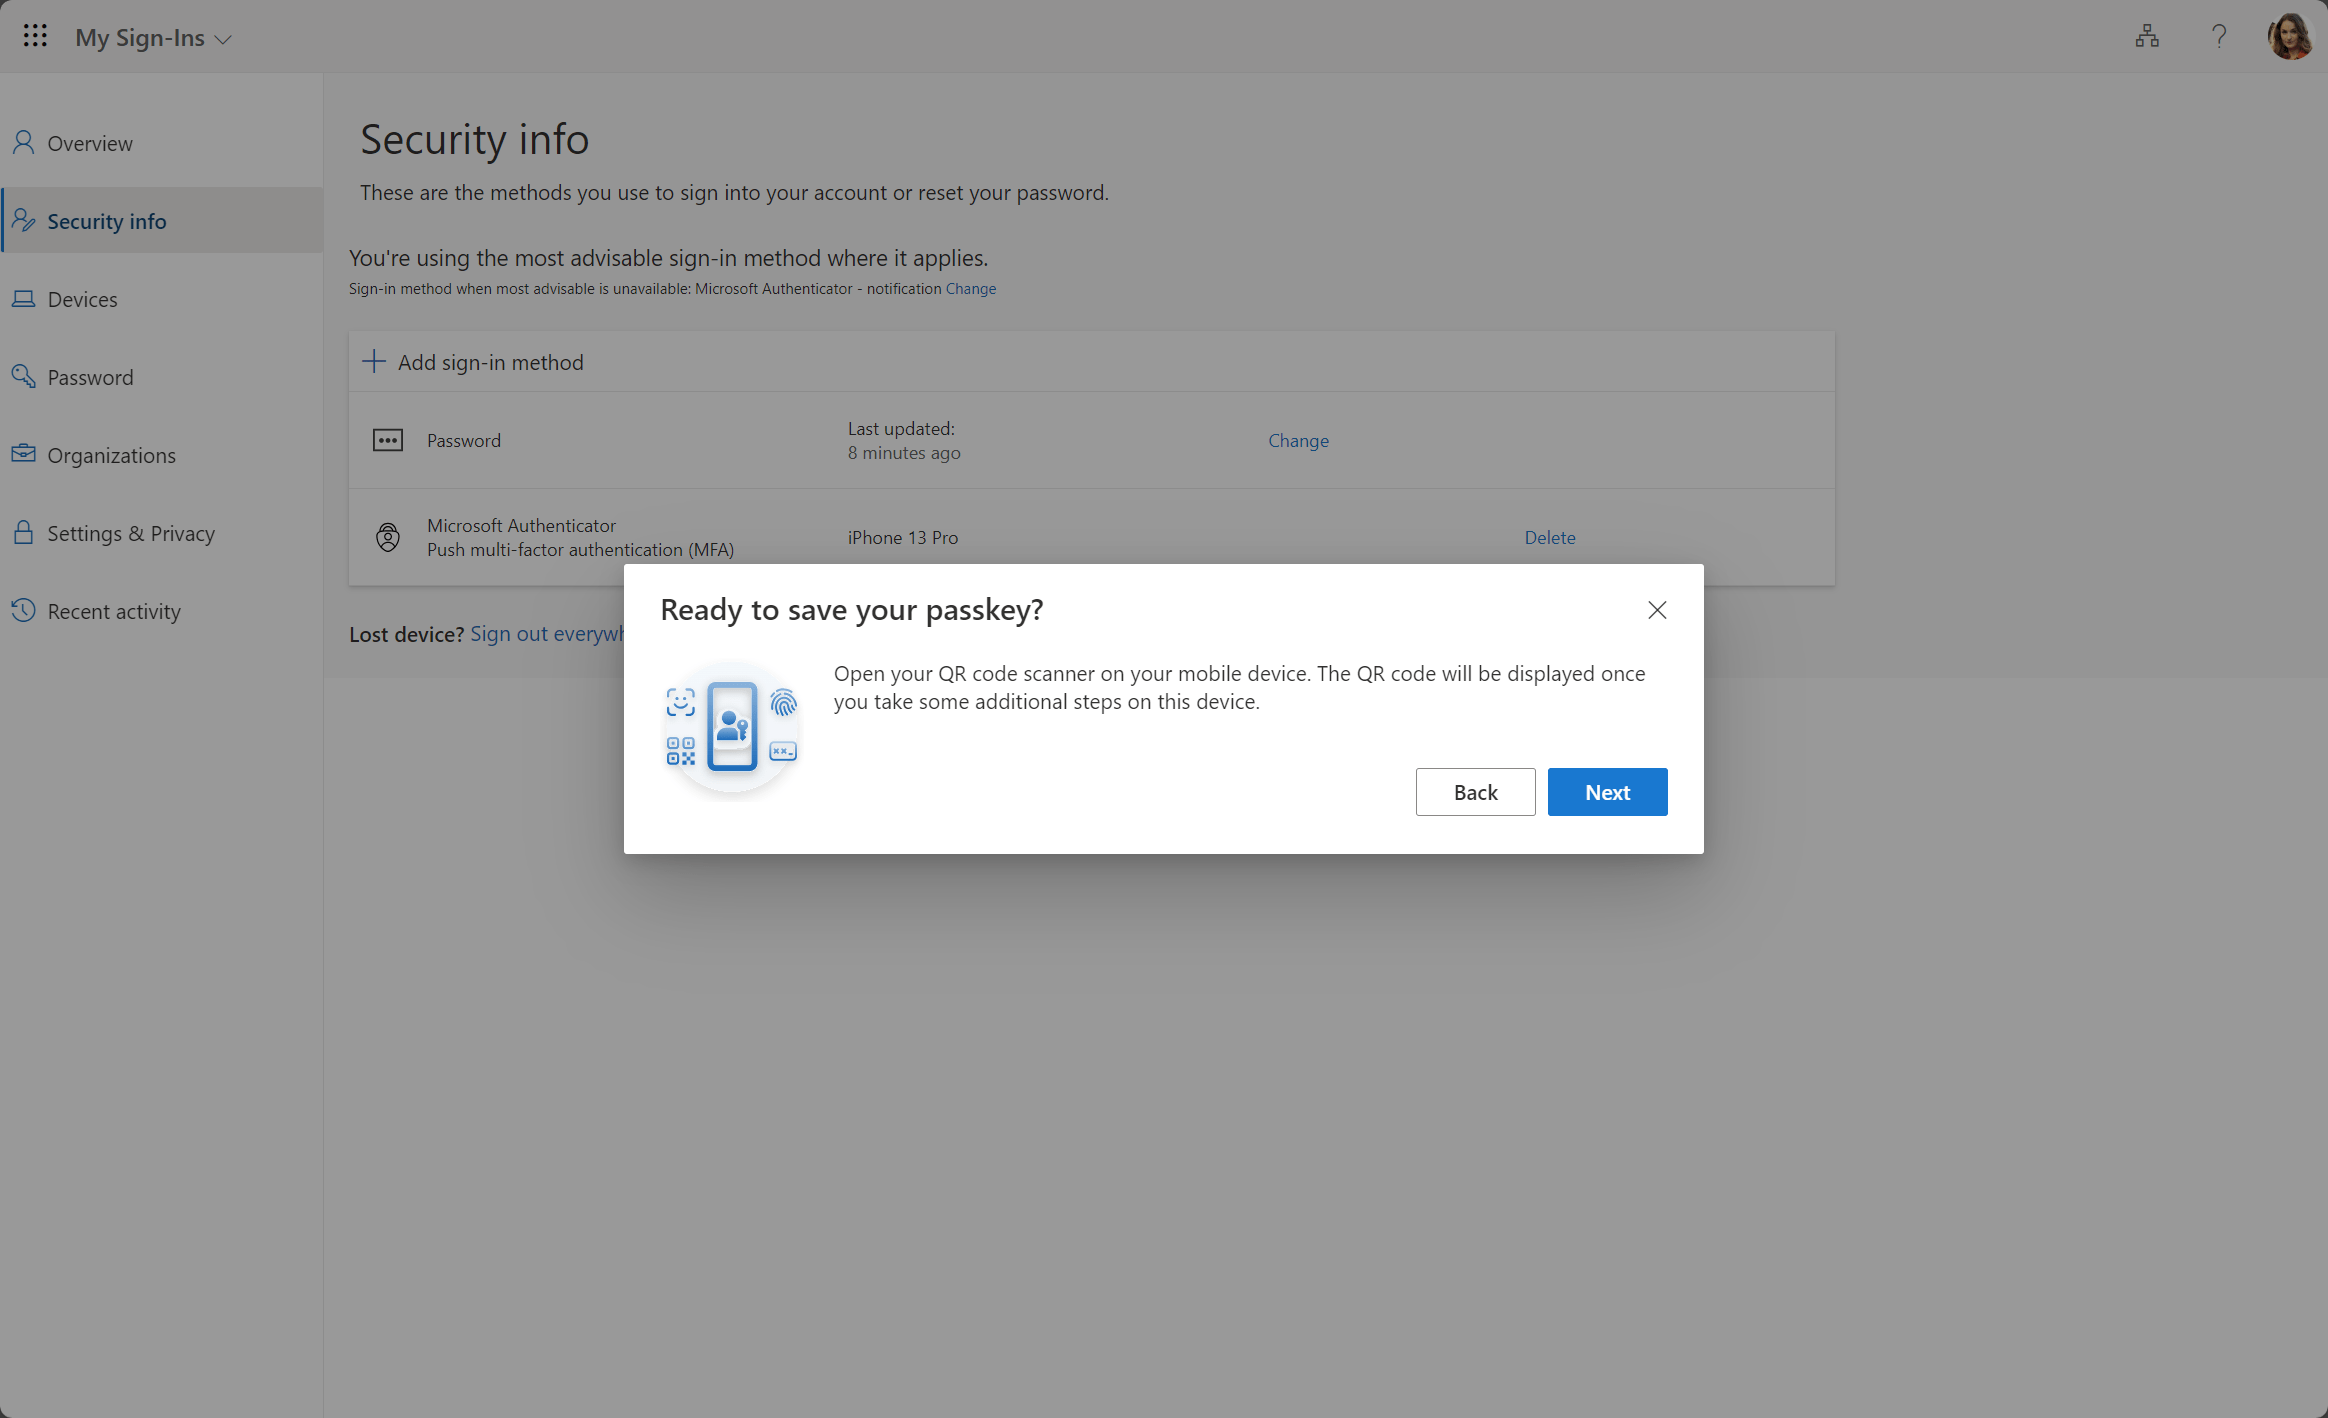
With all the prerequisites in place, we are ready to add the passkey to the Microsoft Authenticator app.
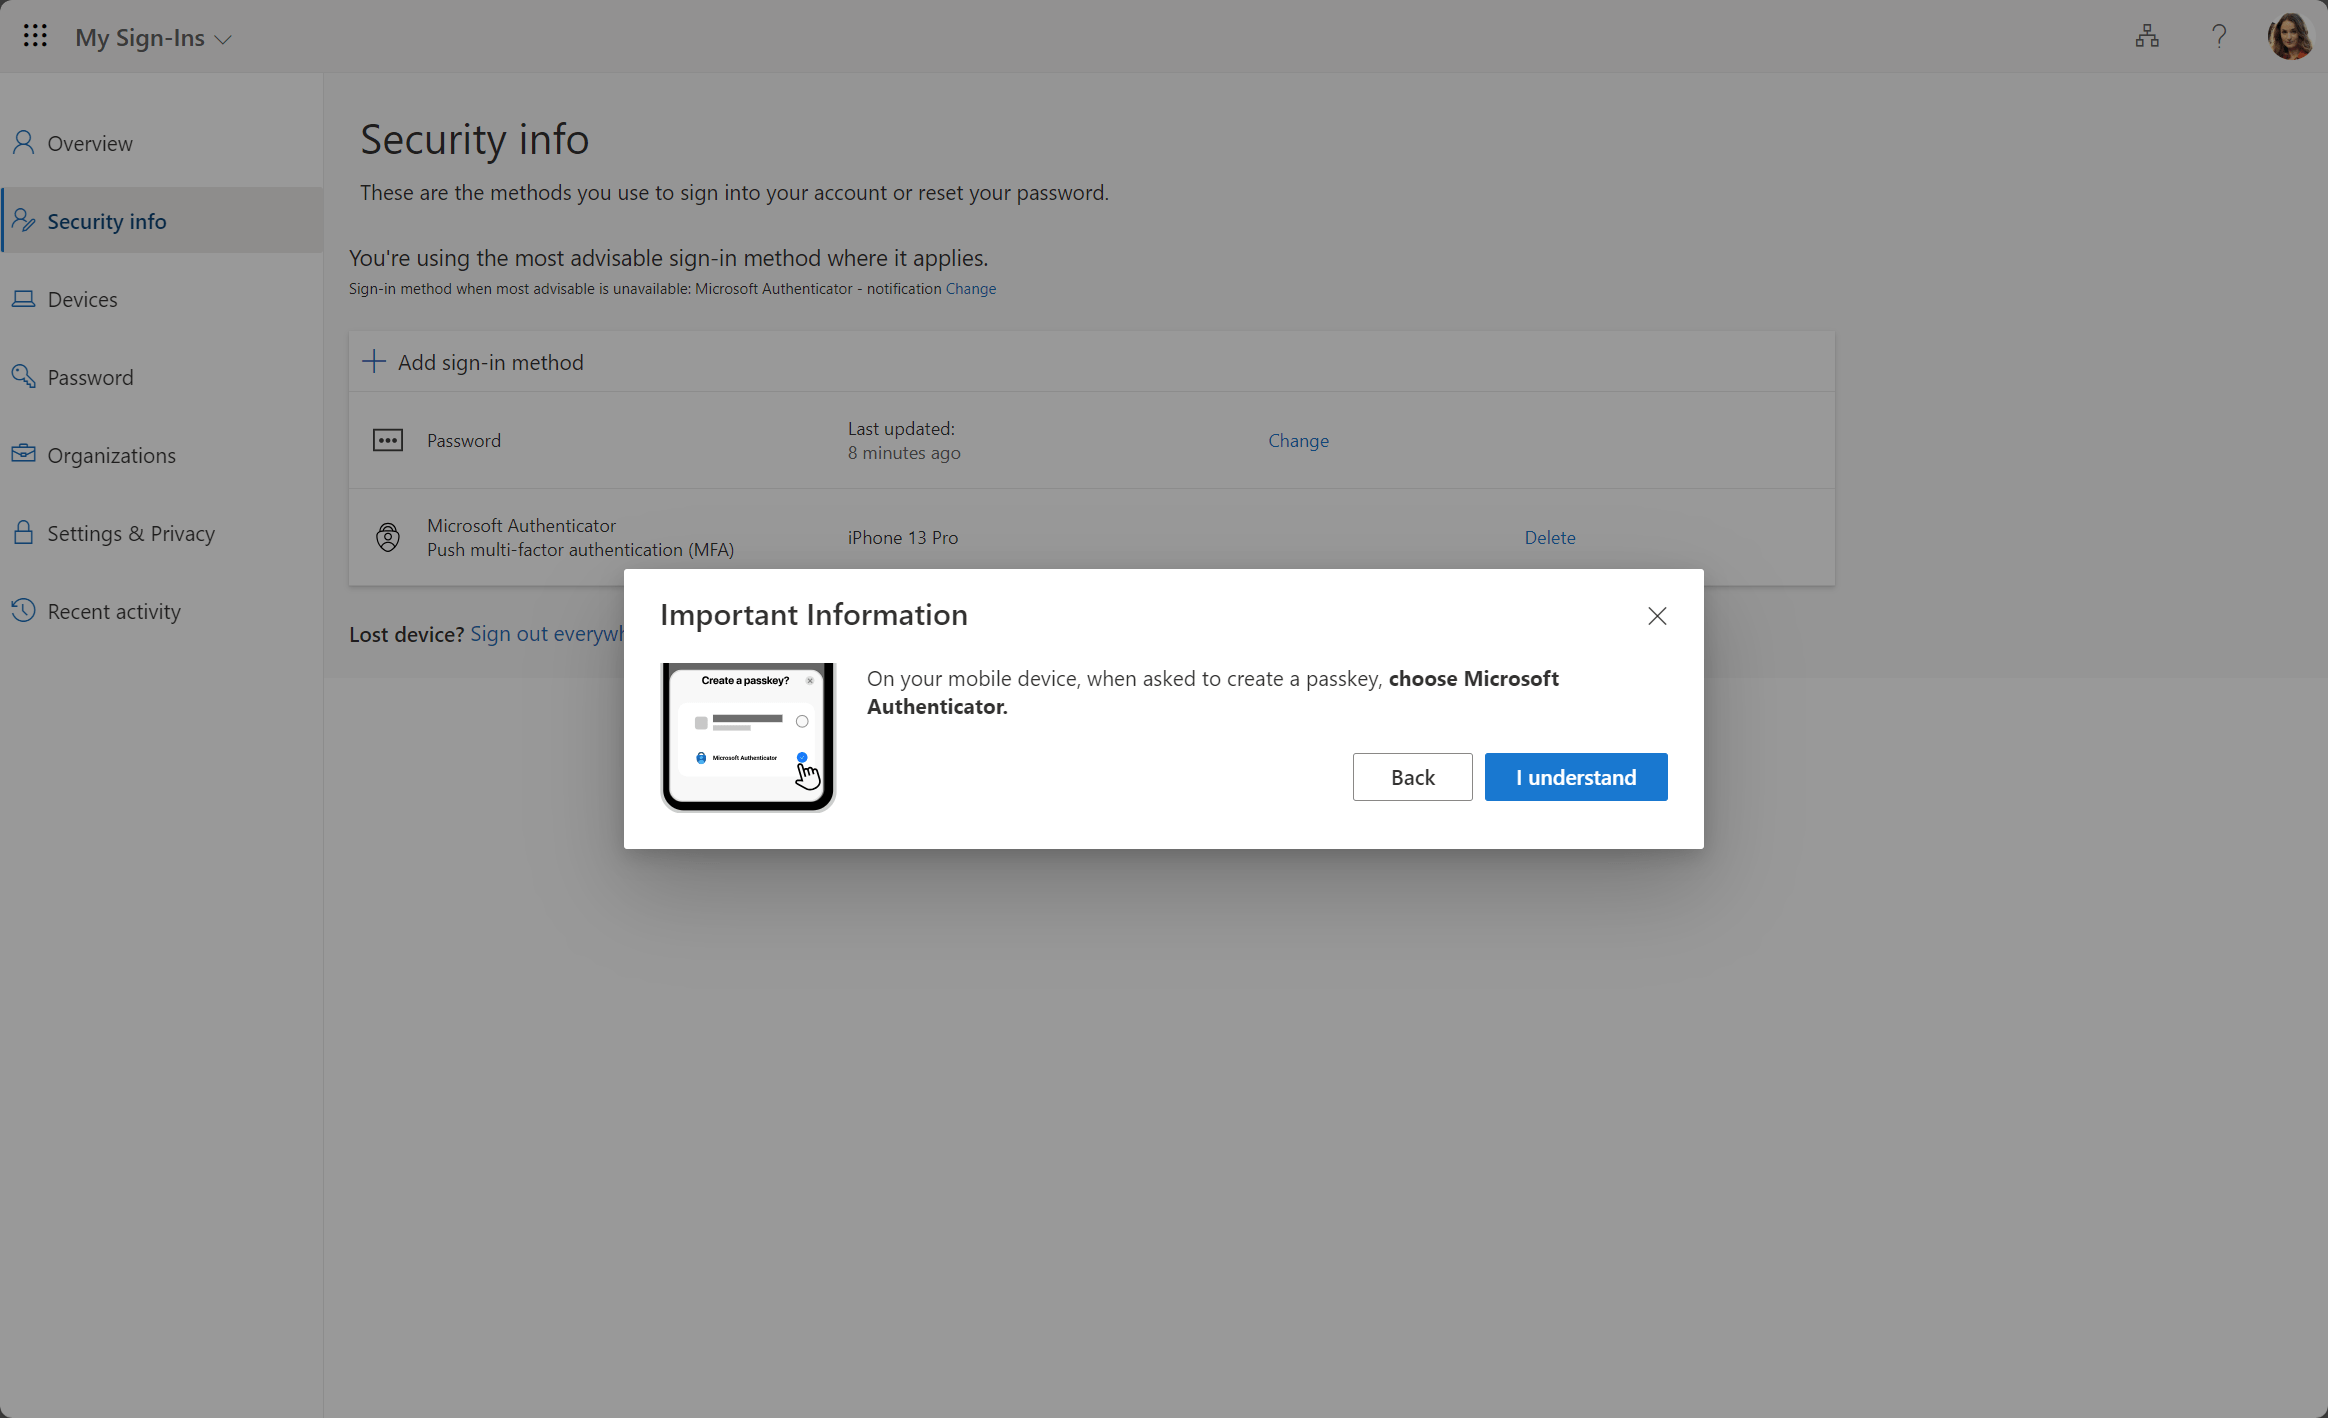
Follow the instructions, and click I understand.
If Windows asks where to save the passkey, pick iPhone, iPad, or Android. This might look different, depending on the browser you are using.
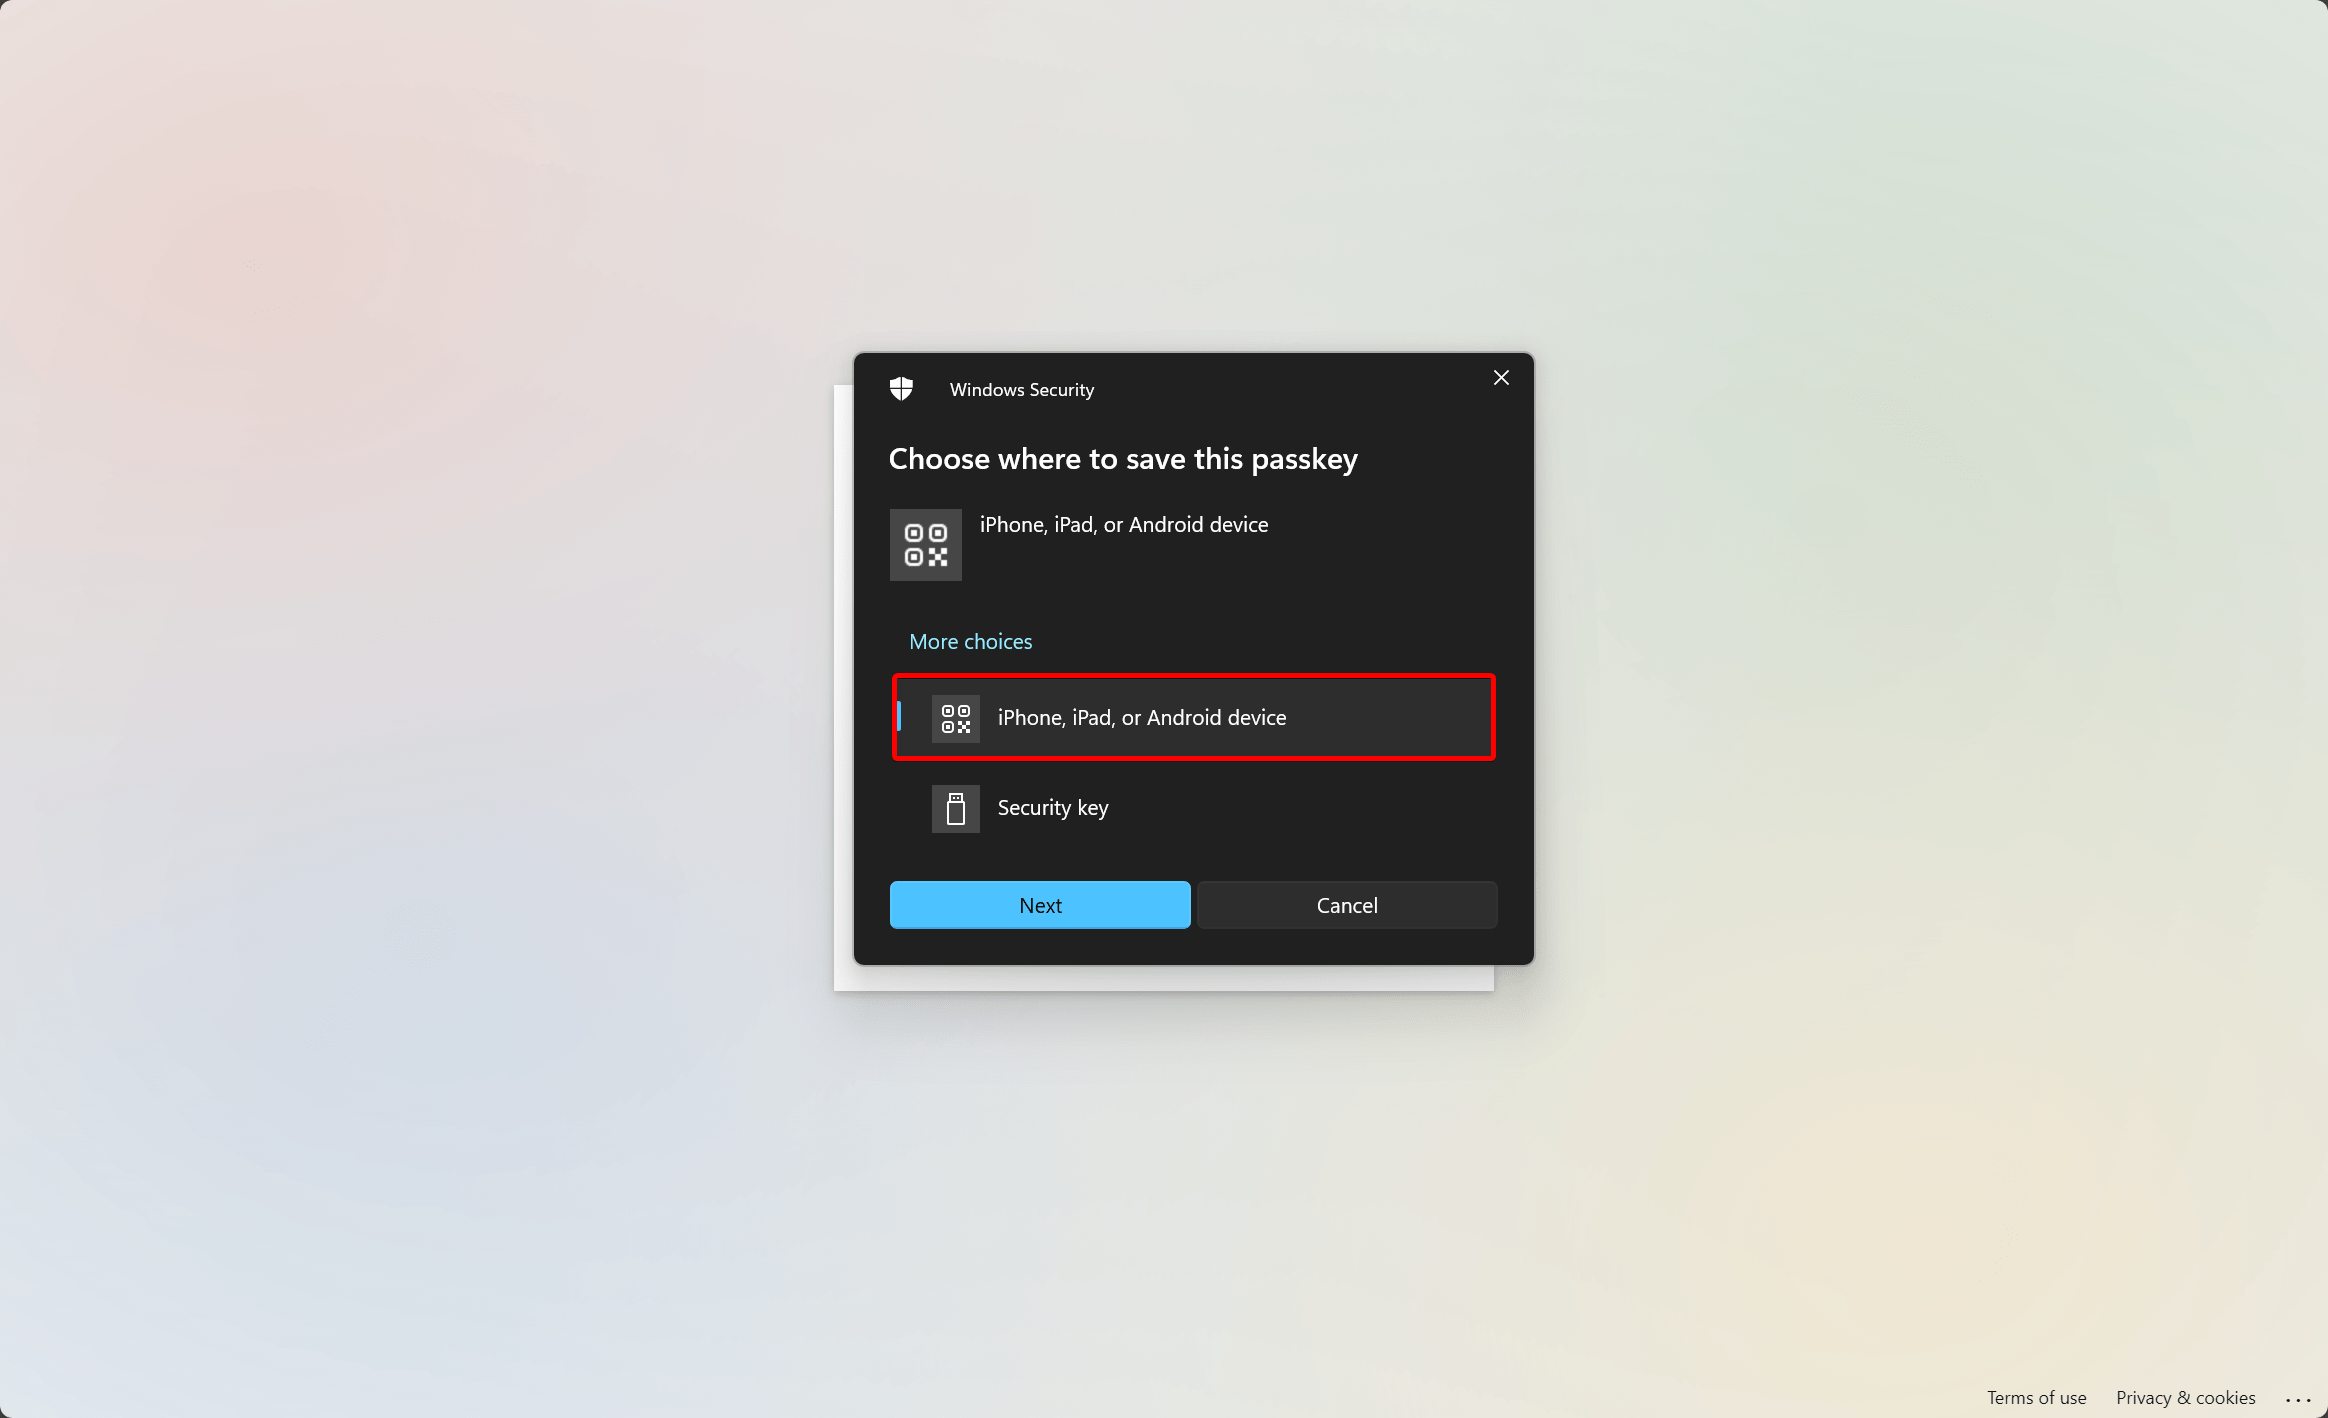
Use your phone camera (so not the QR scan feature from the Authenticator App) and scan the QR code.
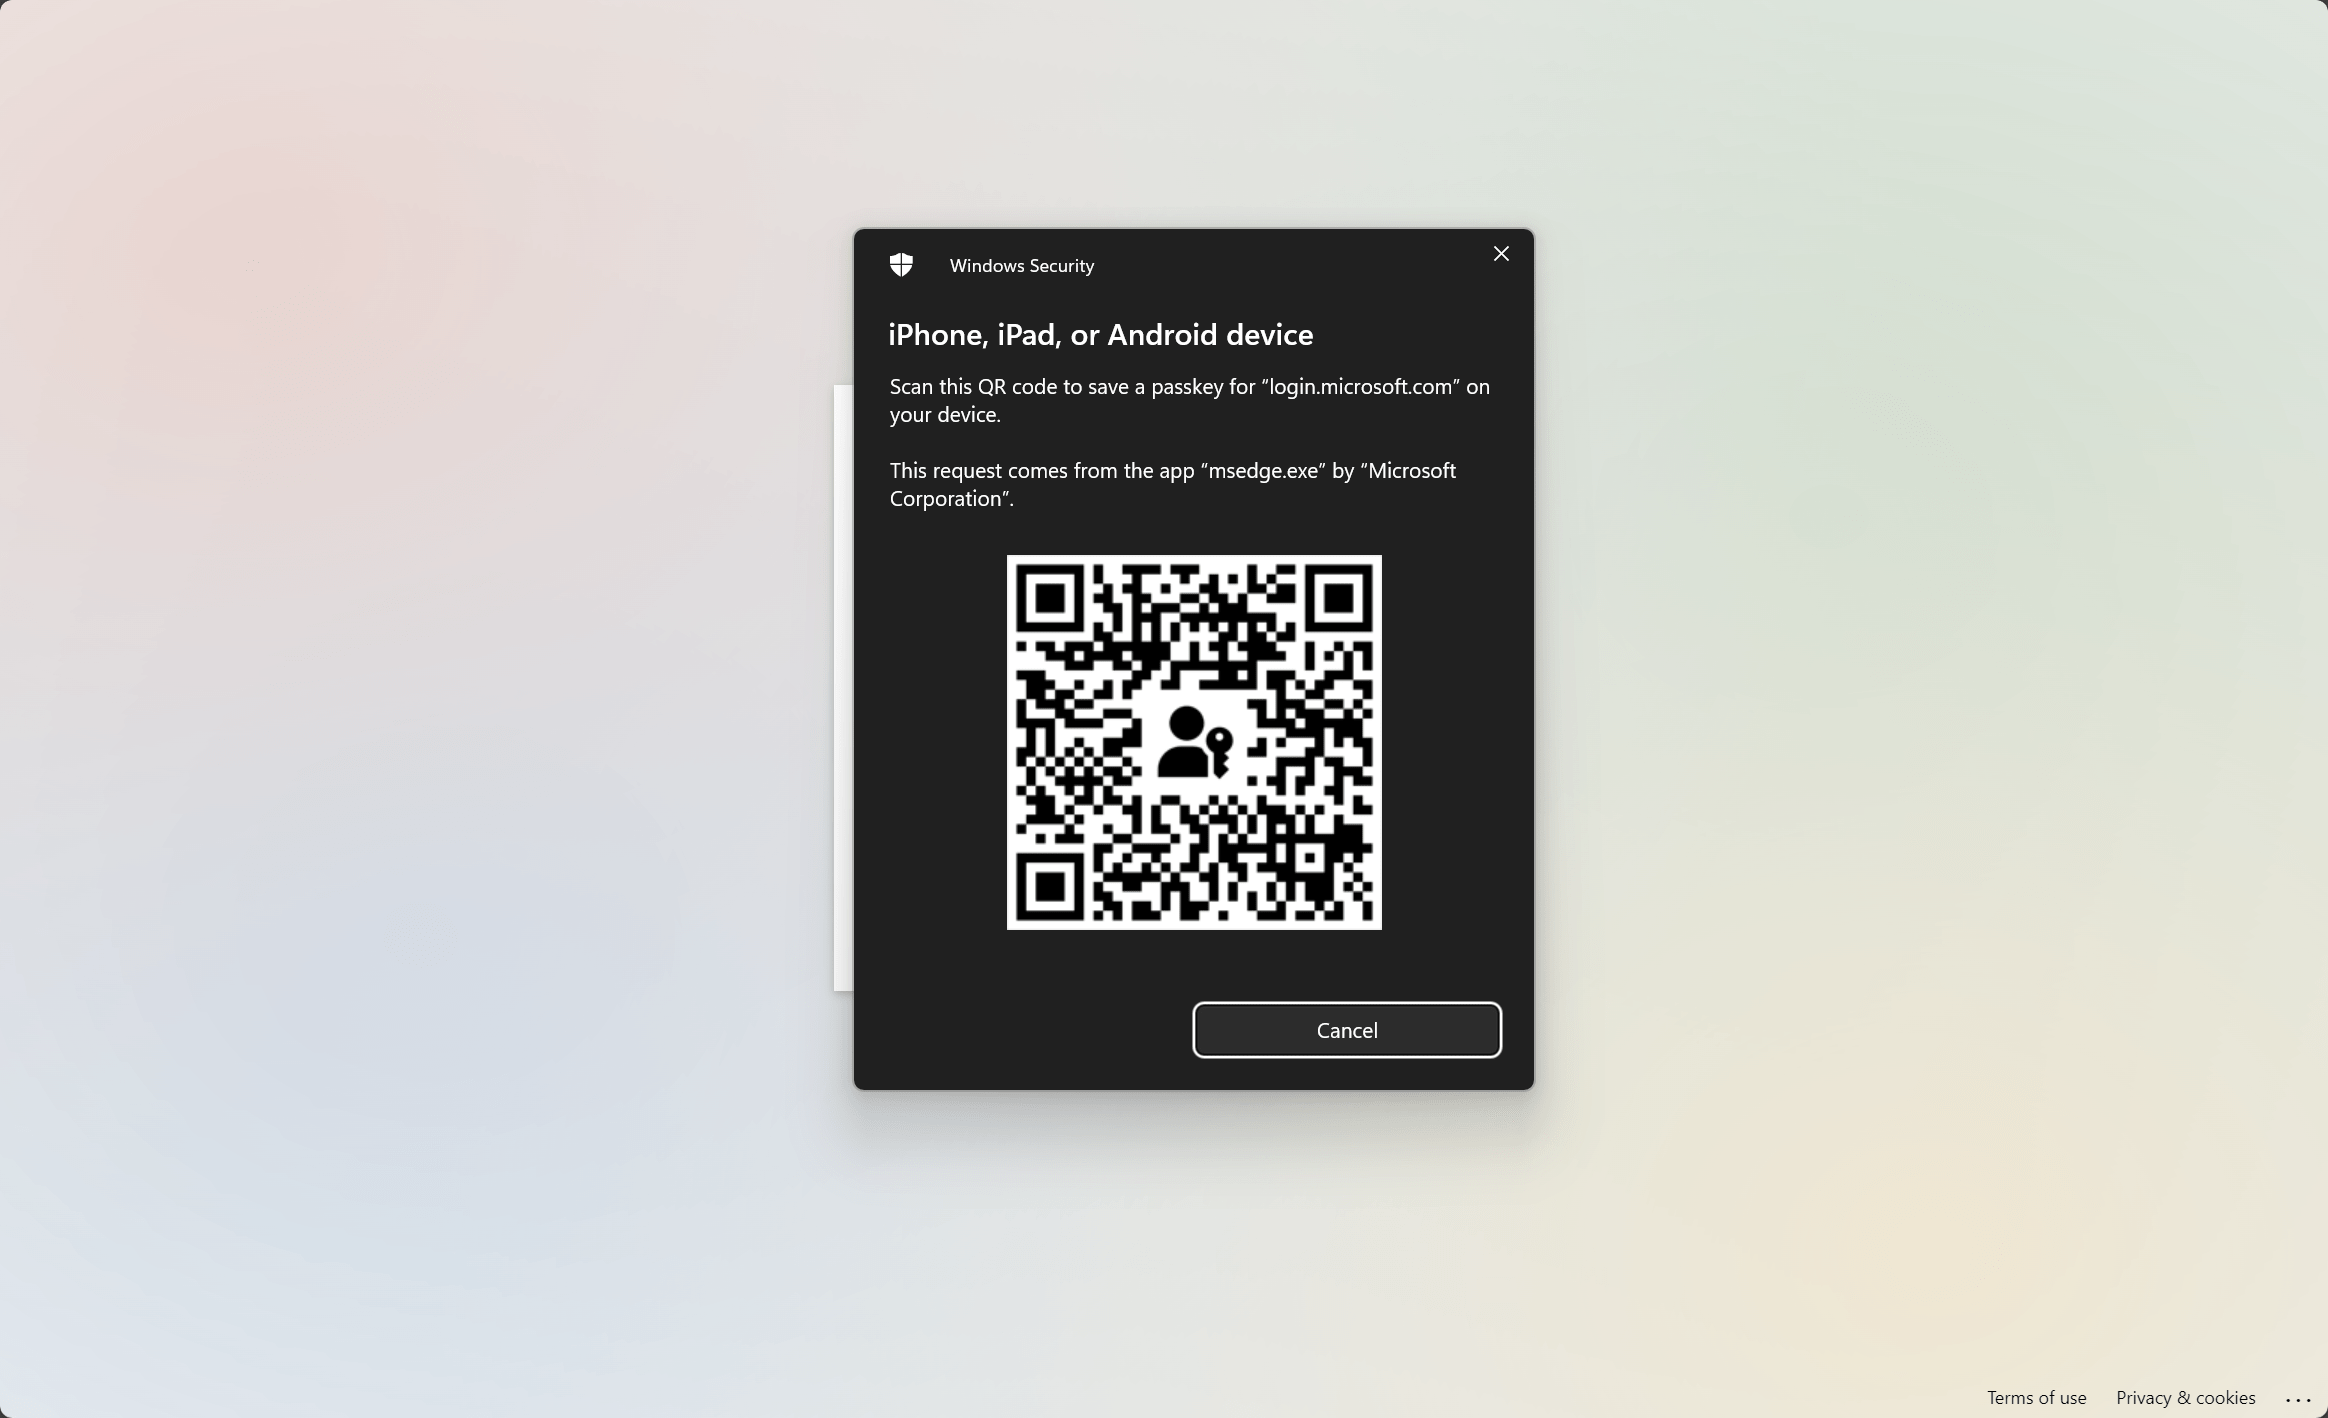
Now tick the “Save a passkey” banner.
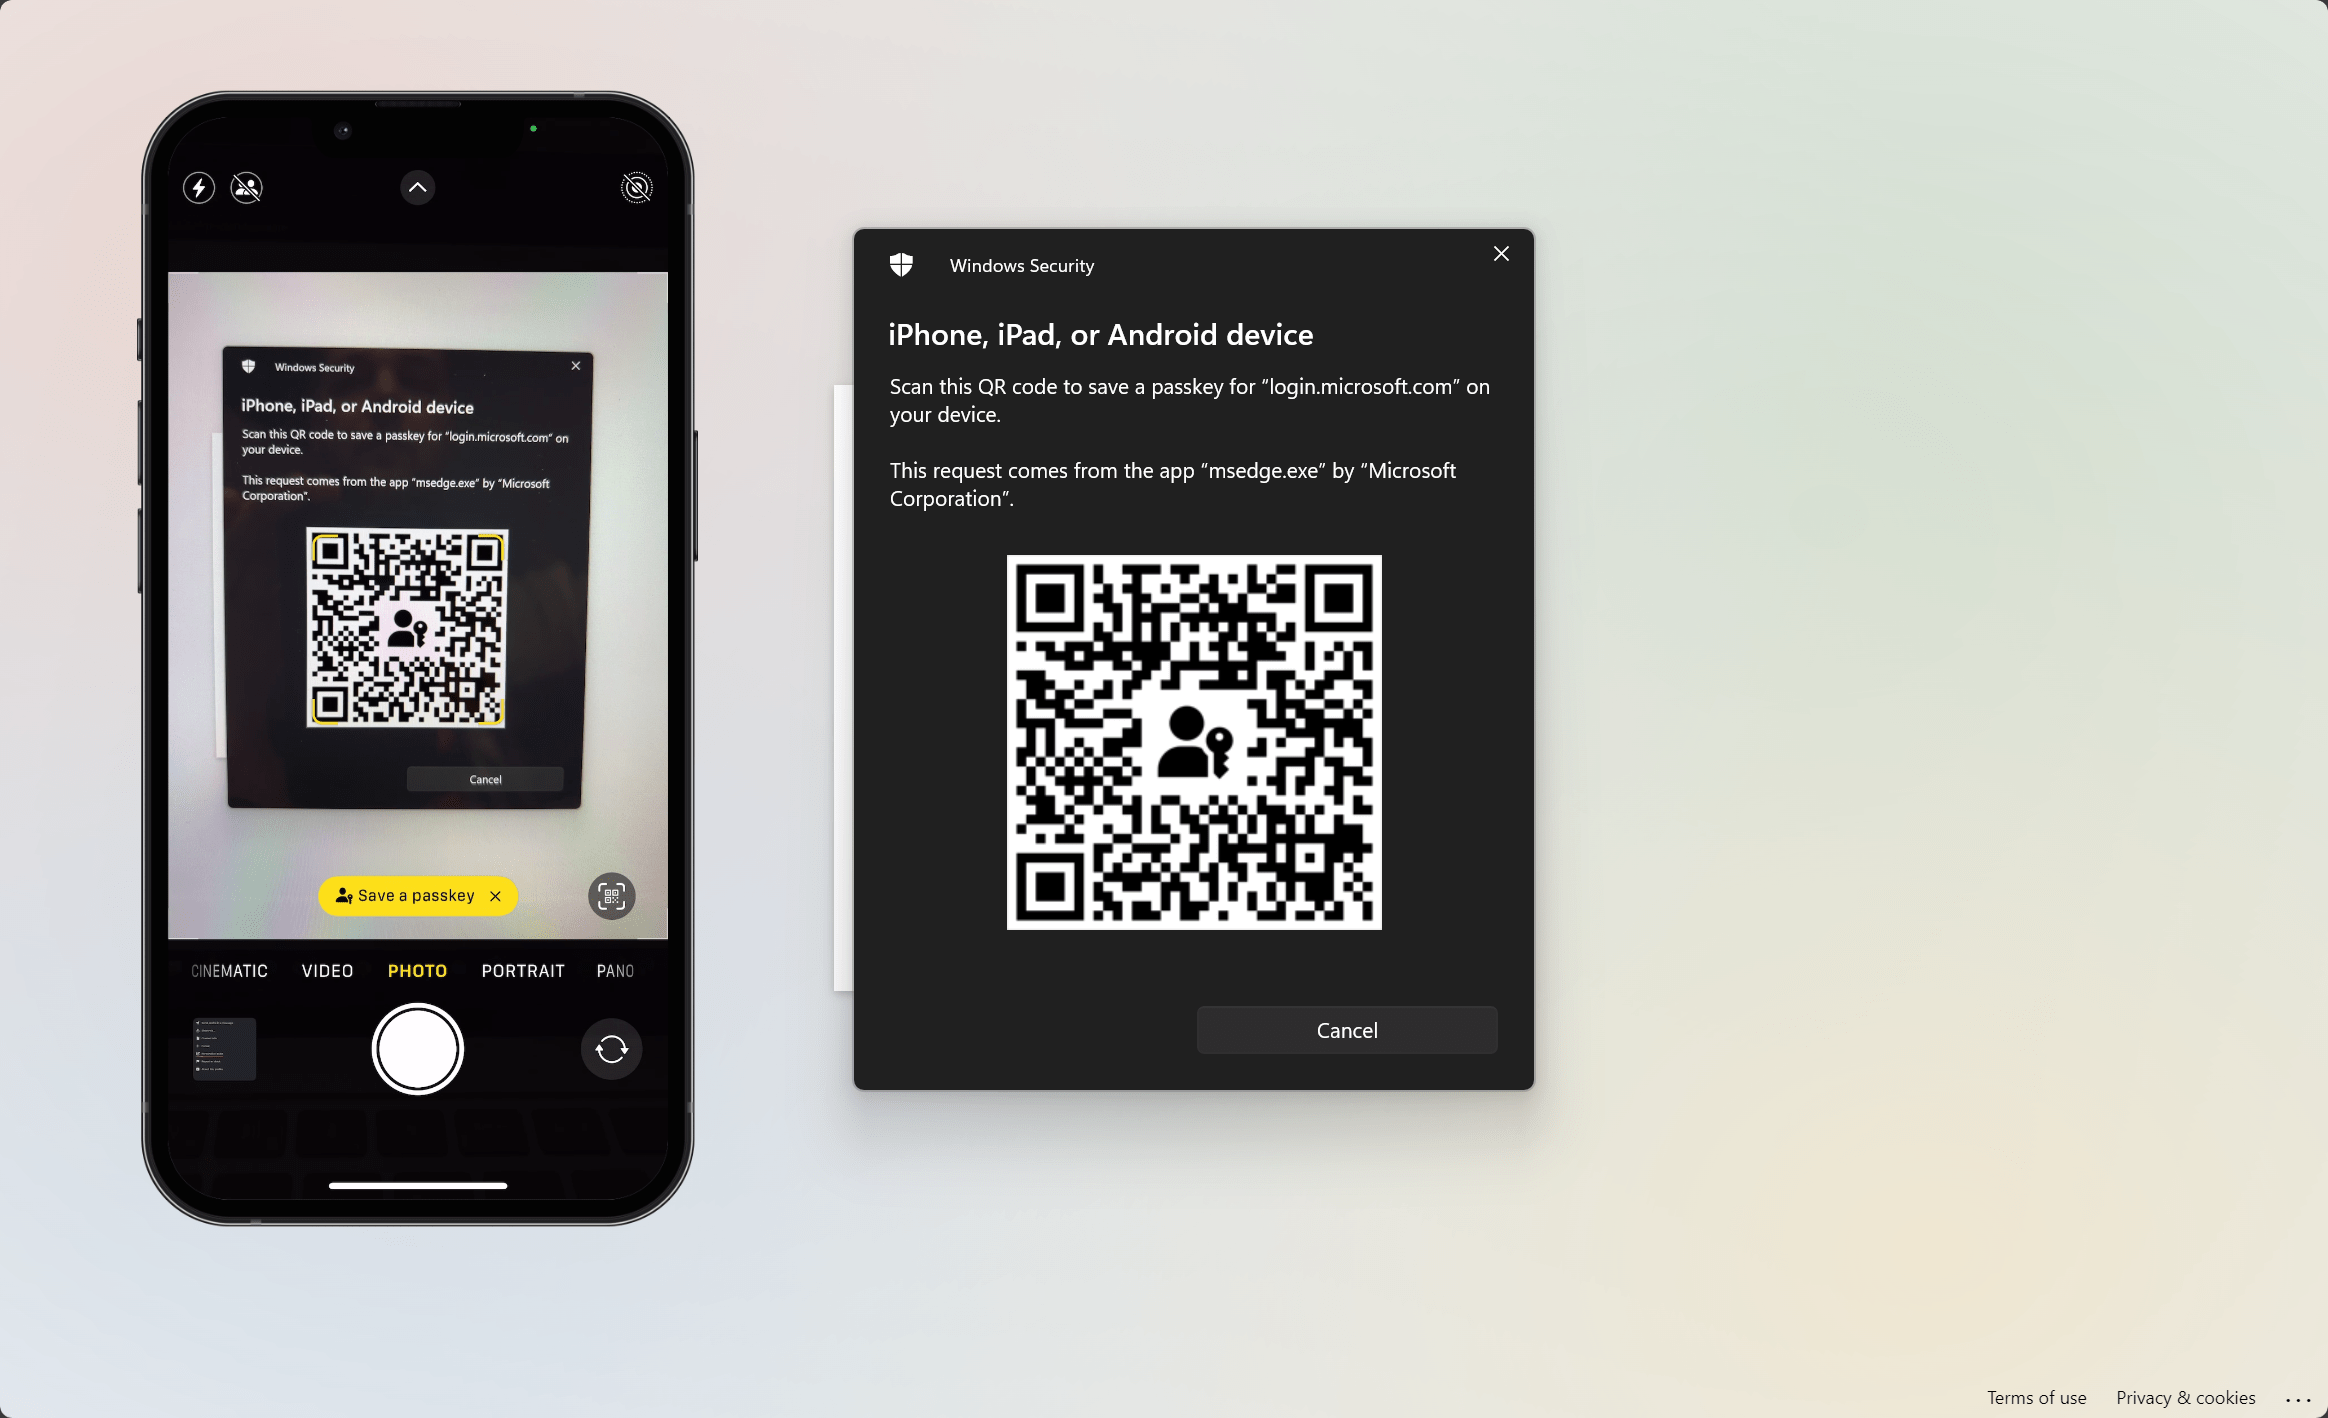
After the device is connected over Bluetooth, select Authenticator from your phone and click Continue.
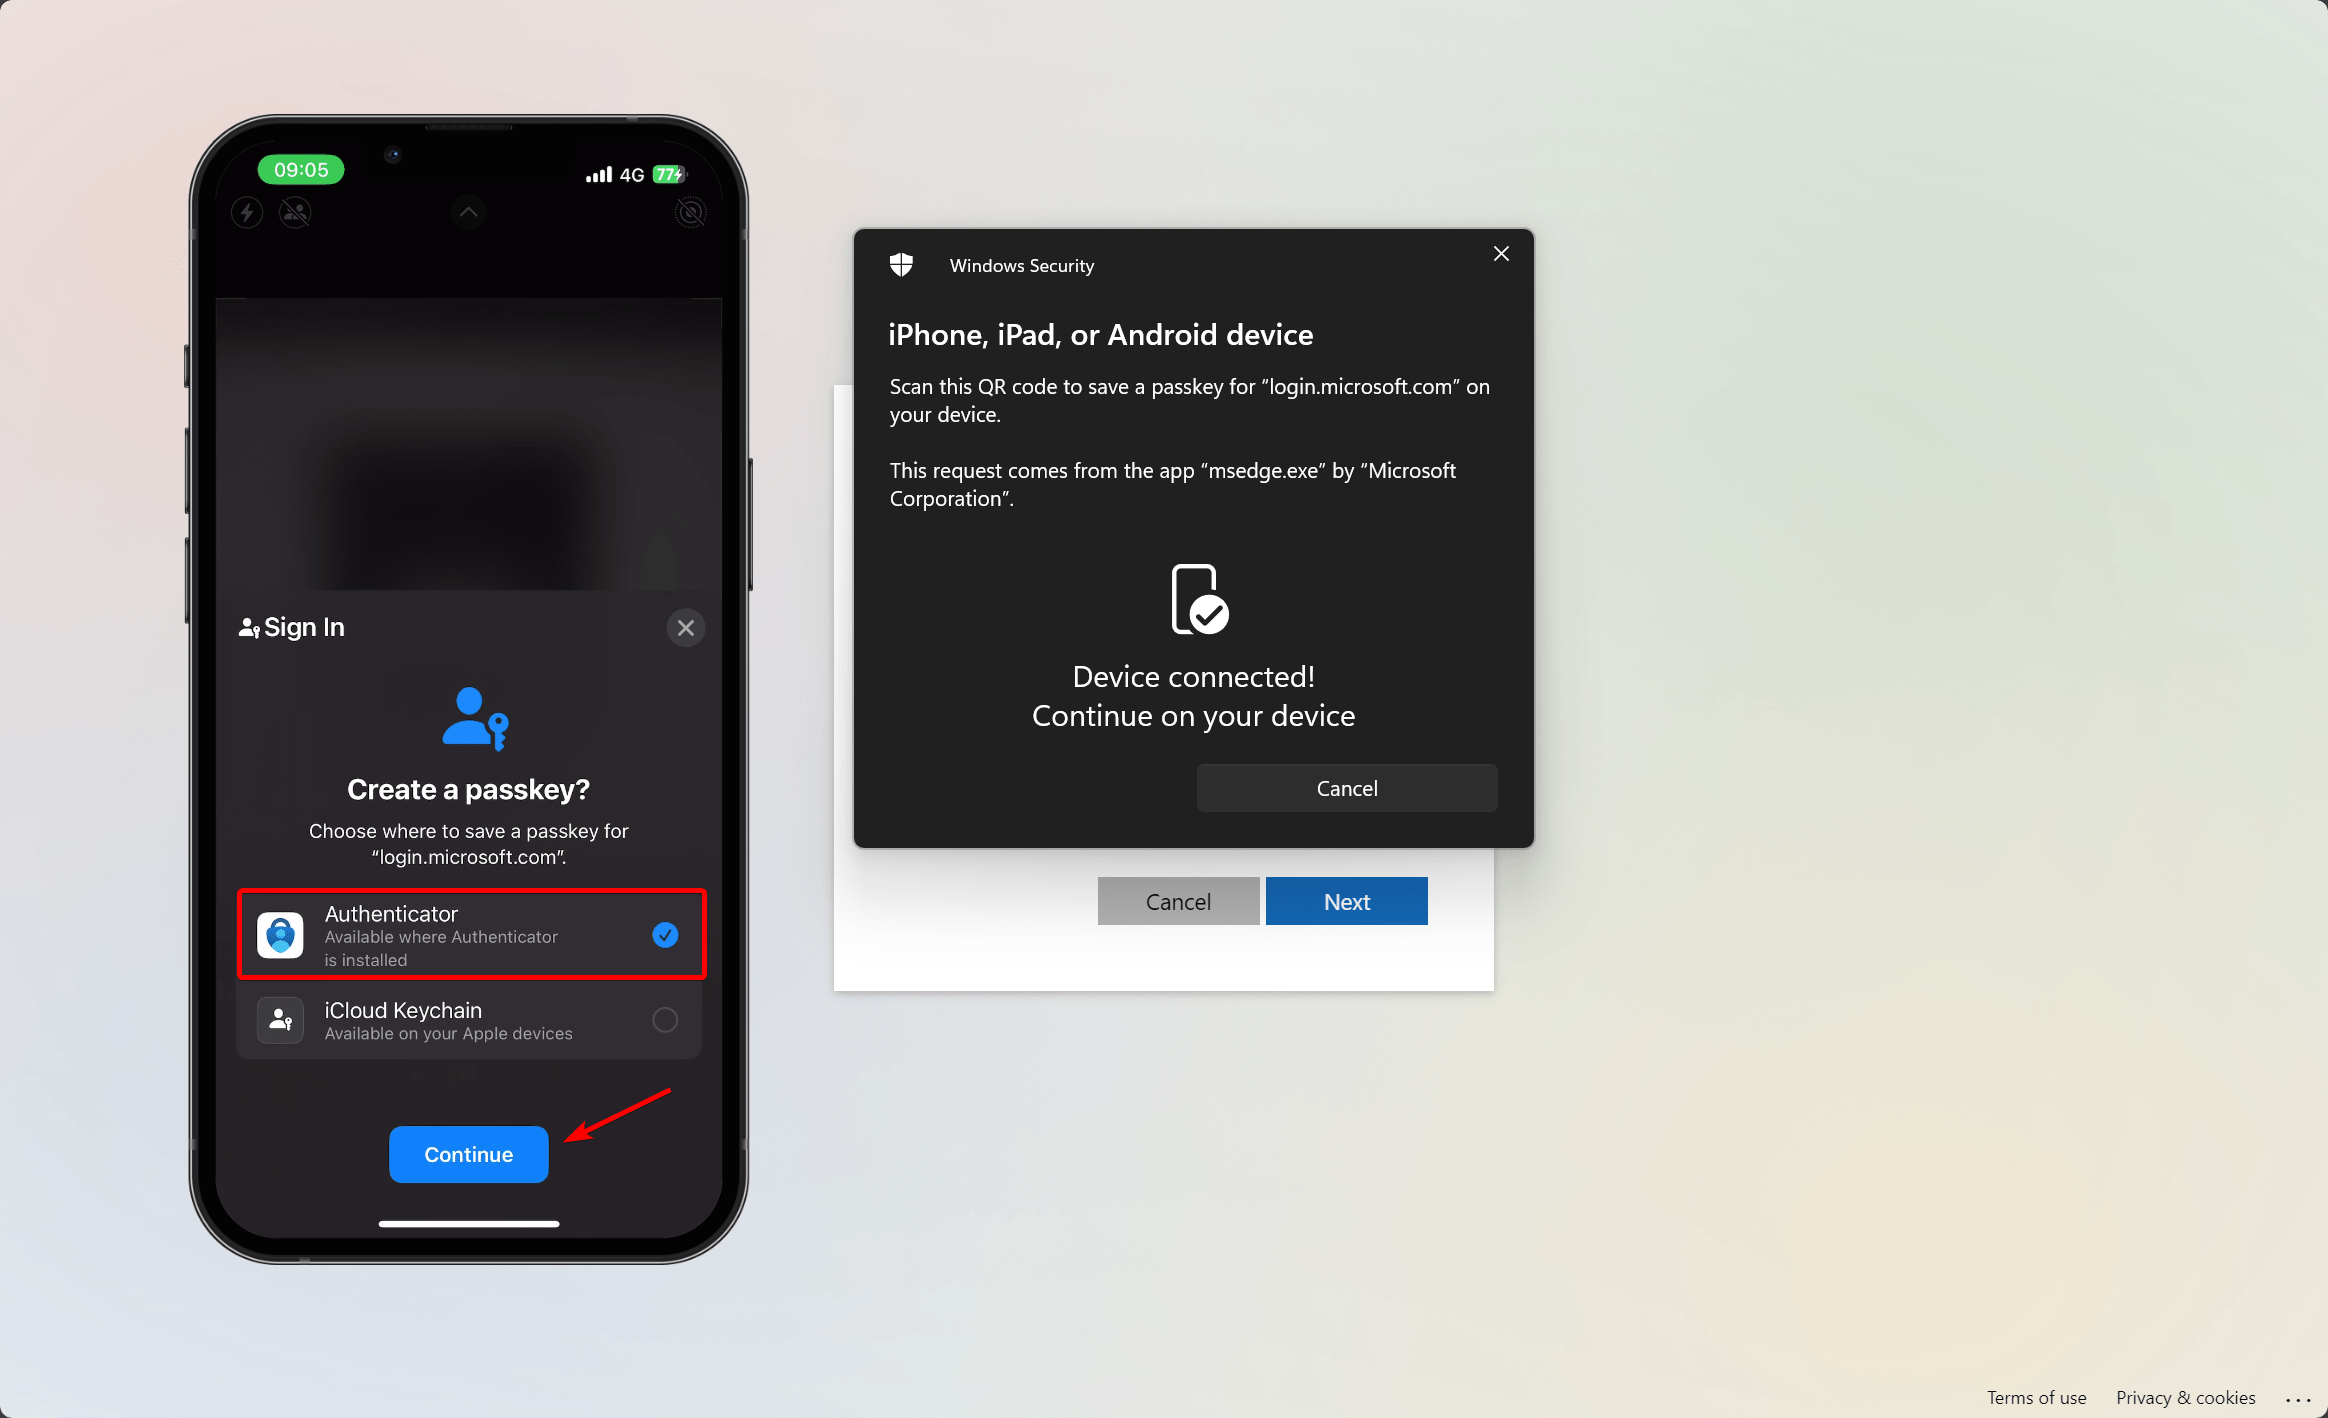
If this was successful, the passkey is now saved.
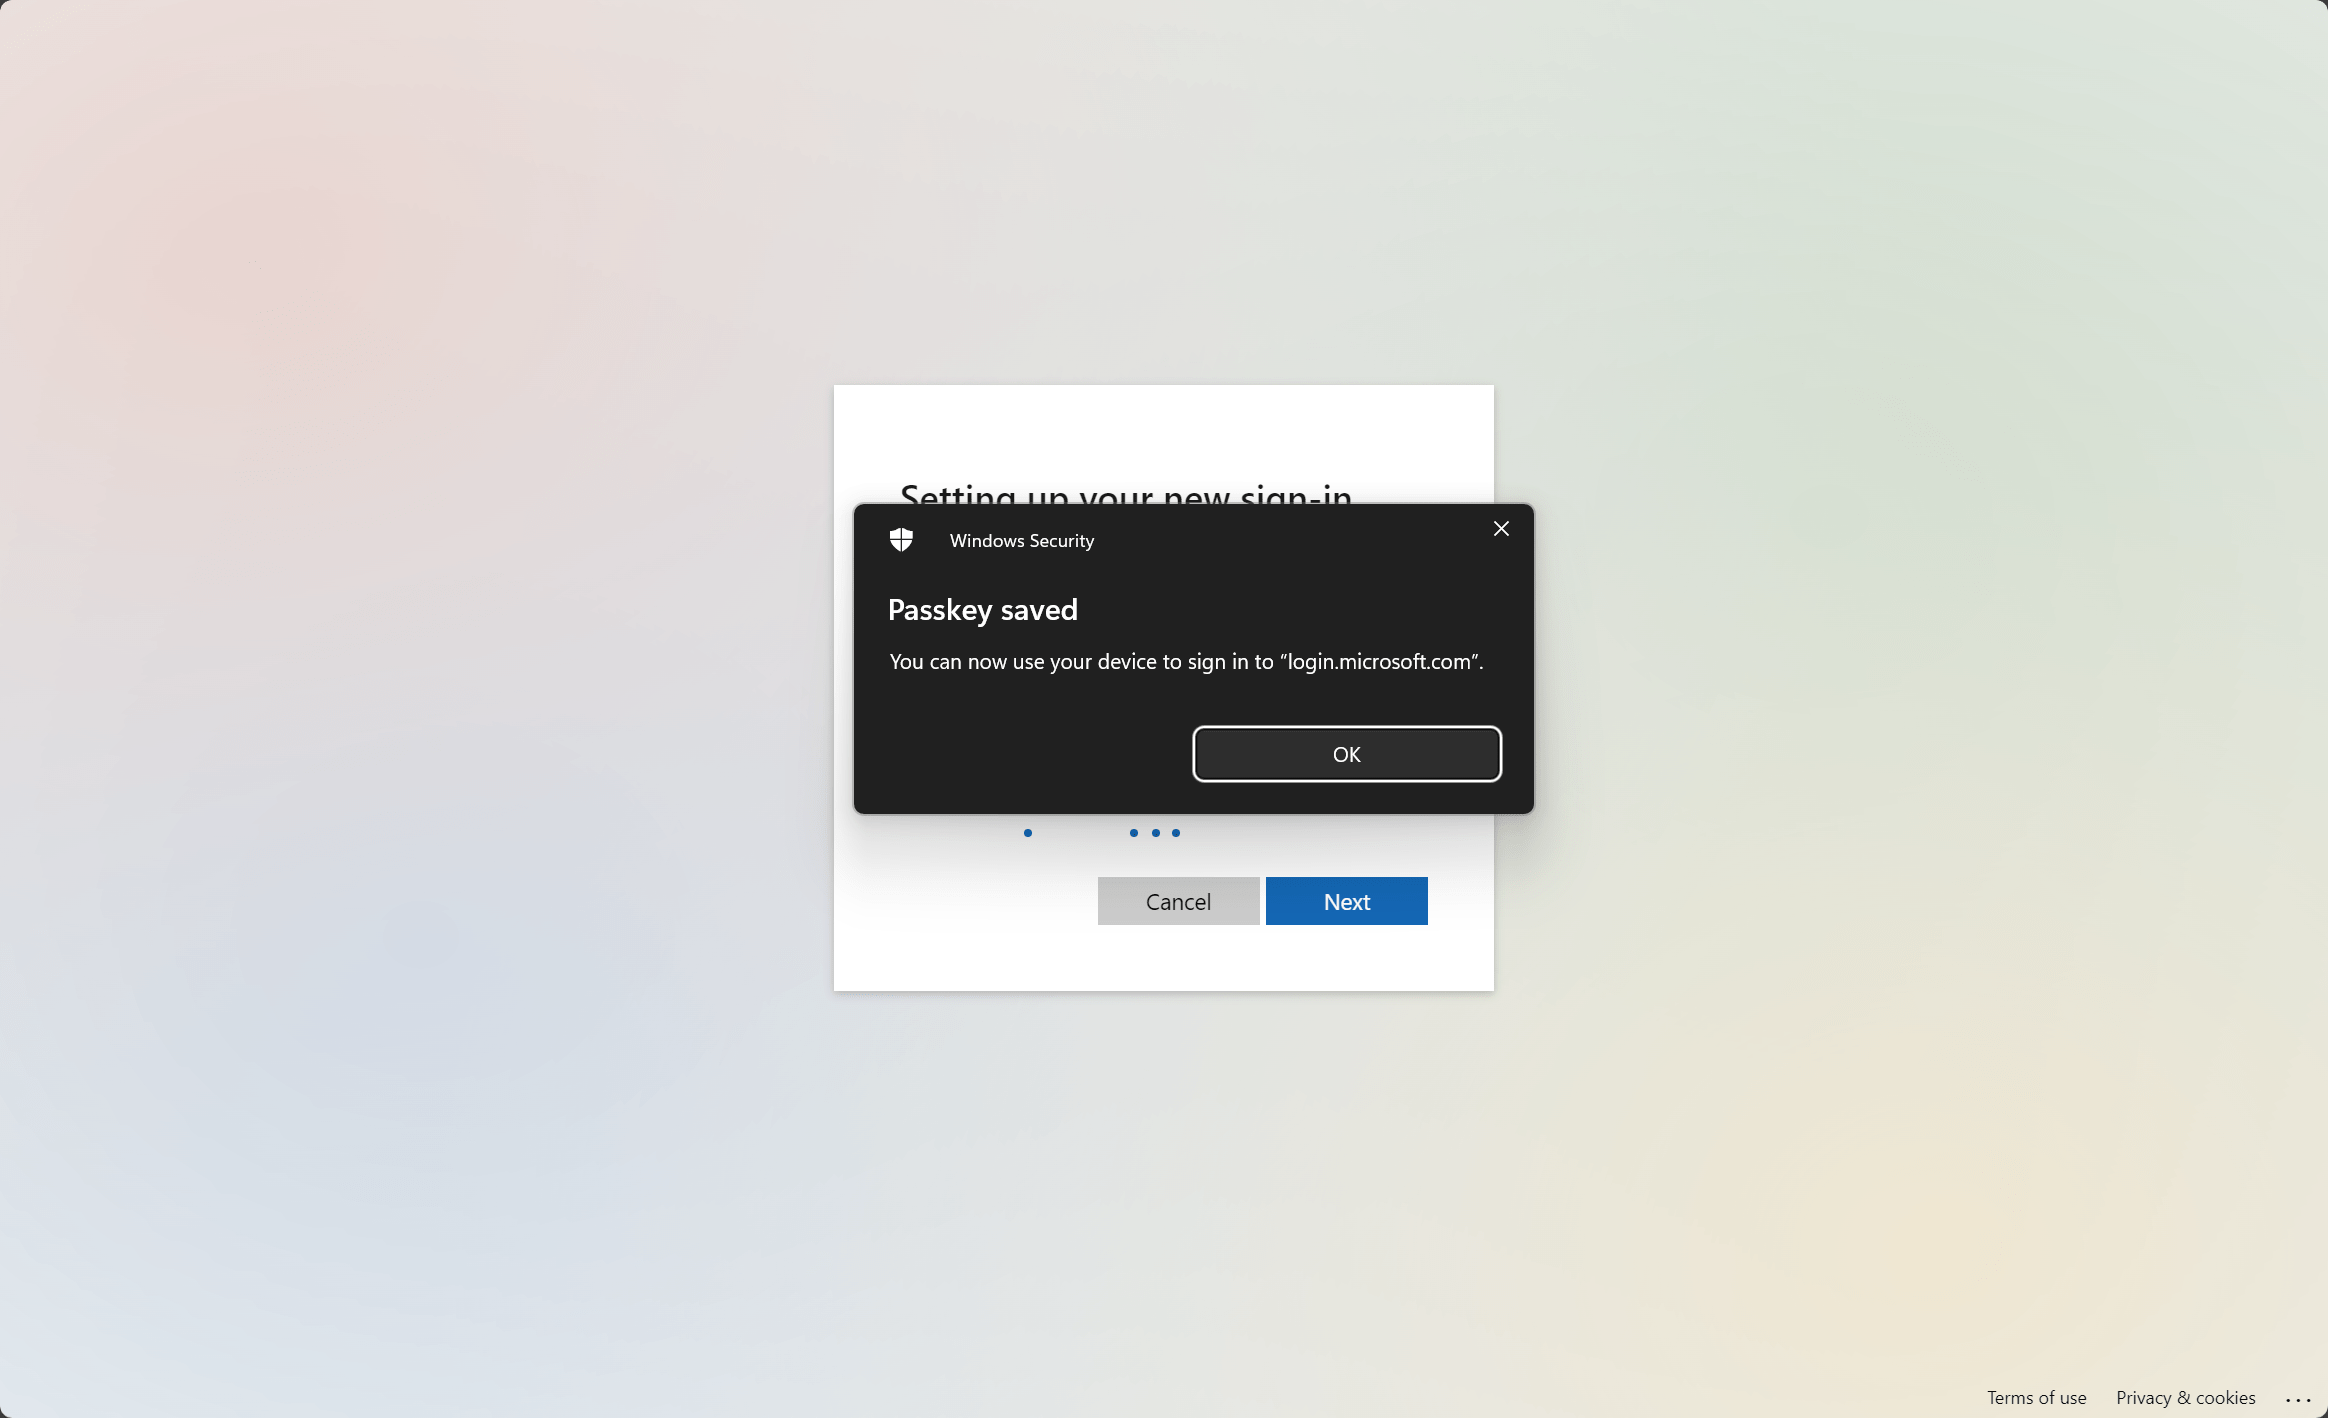
The only thing that remains is coming up with a sensible name for your passkey.
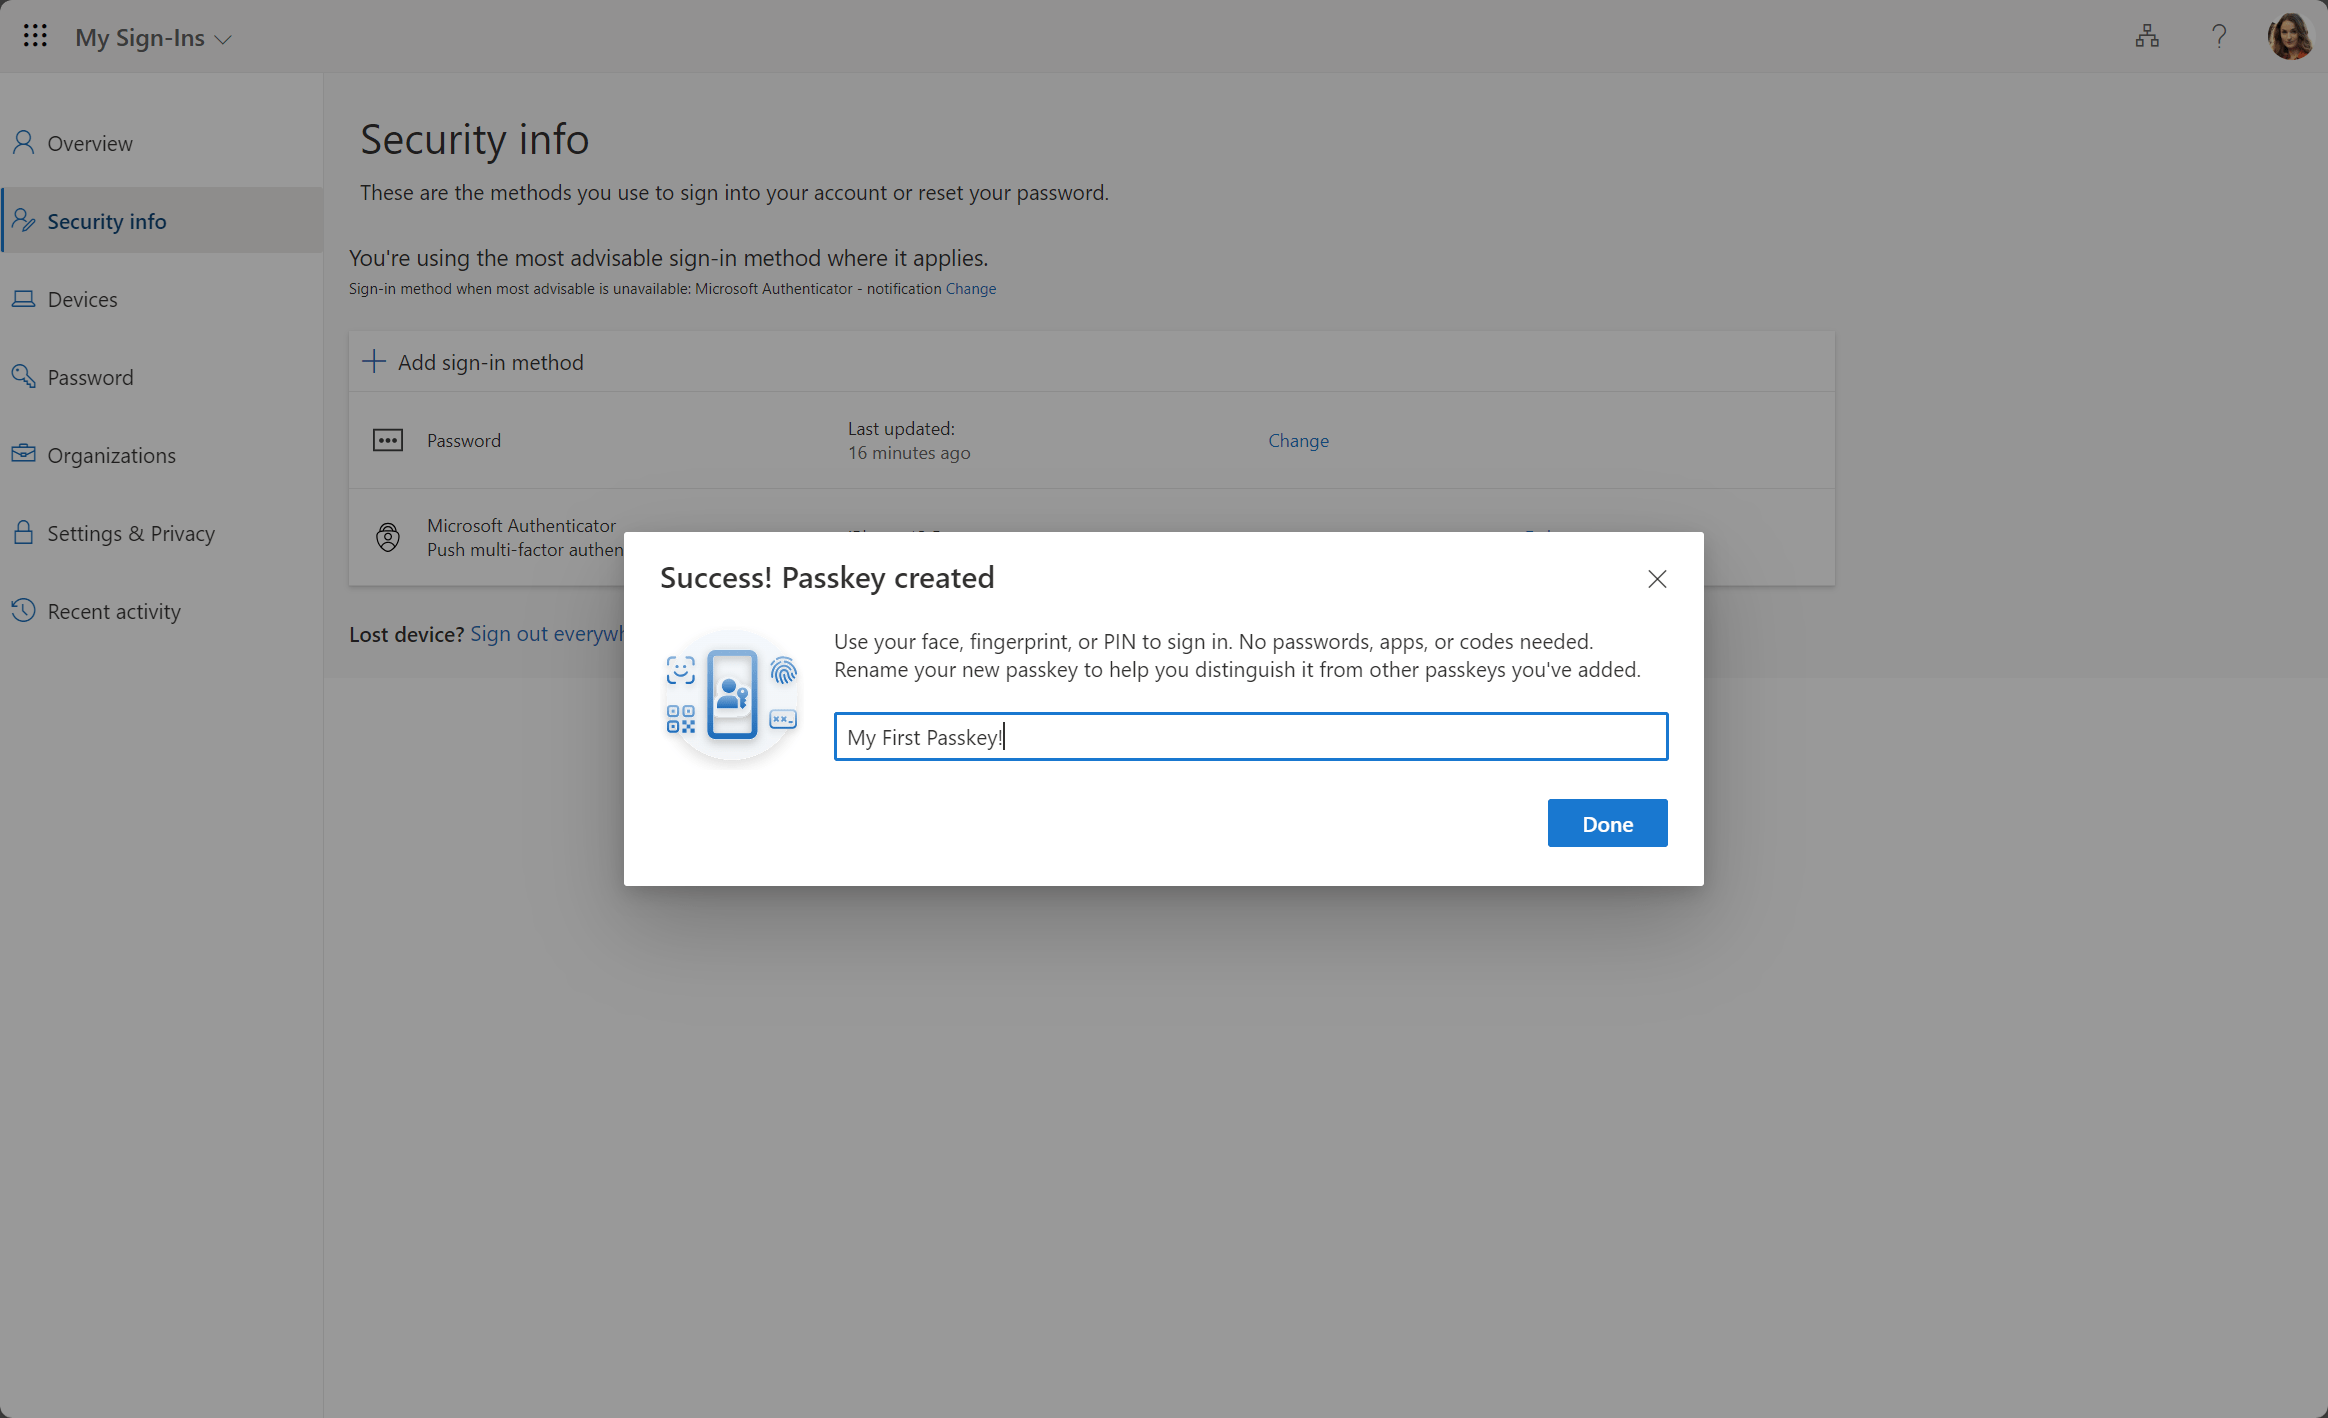
Take a moment to celebrate this memorable moment. You just added your first passkey to Microsoft 365! That’s a cool story for the grandkids.
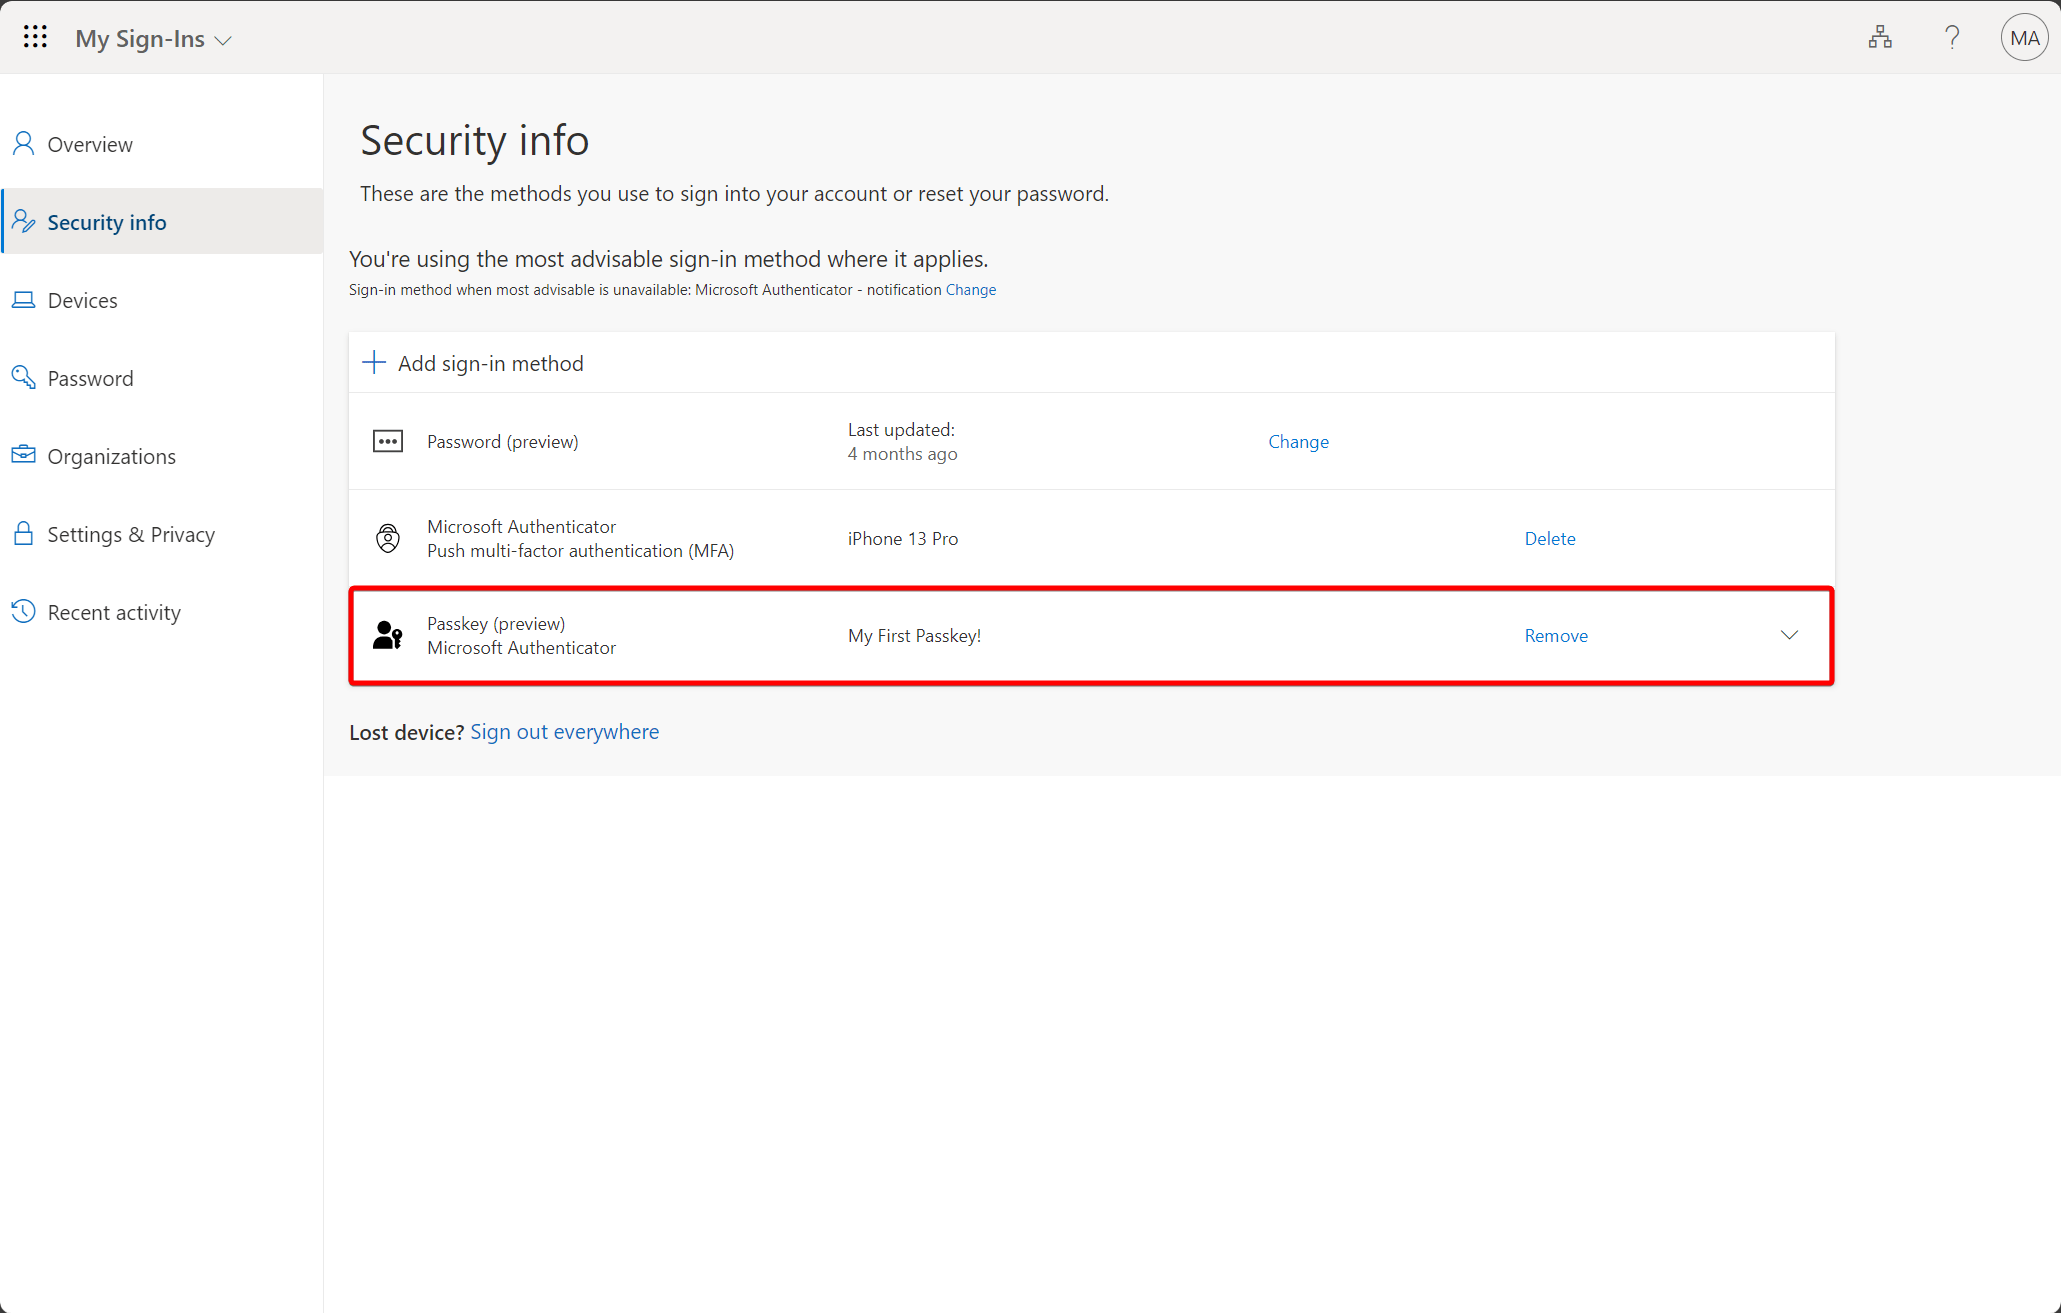
I’ve created a quick video to demonstrate the steps:
End-user experience - Direct registration of a device-bound passkey in Microsoft Authenticator – iOS + Android#
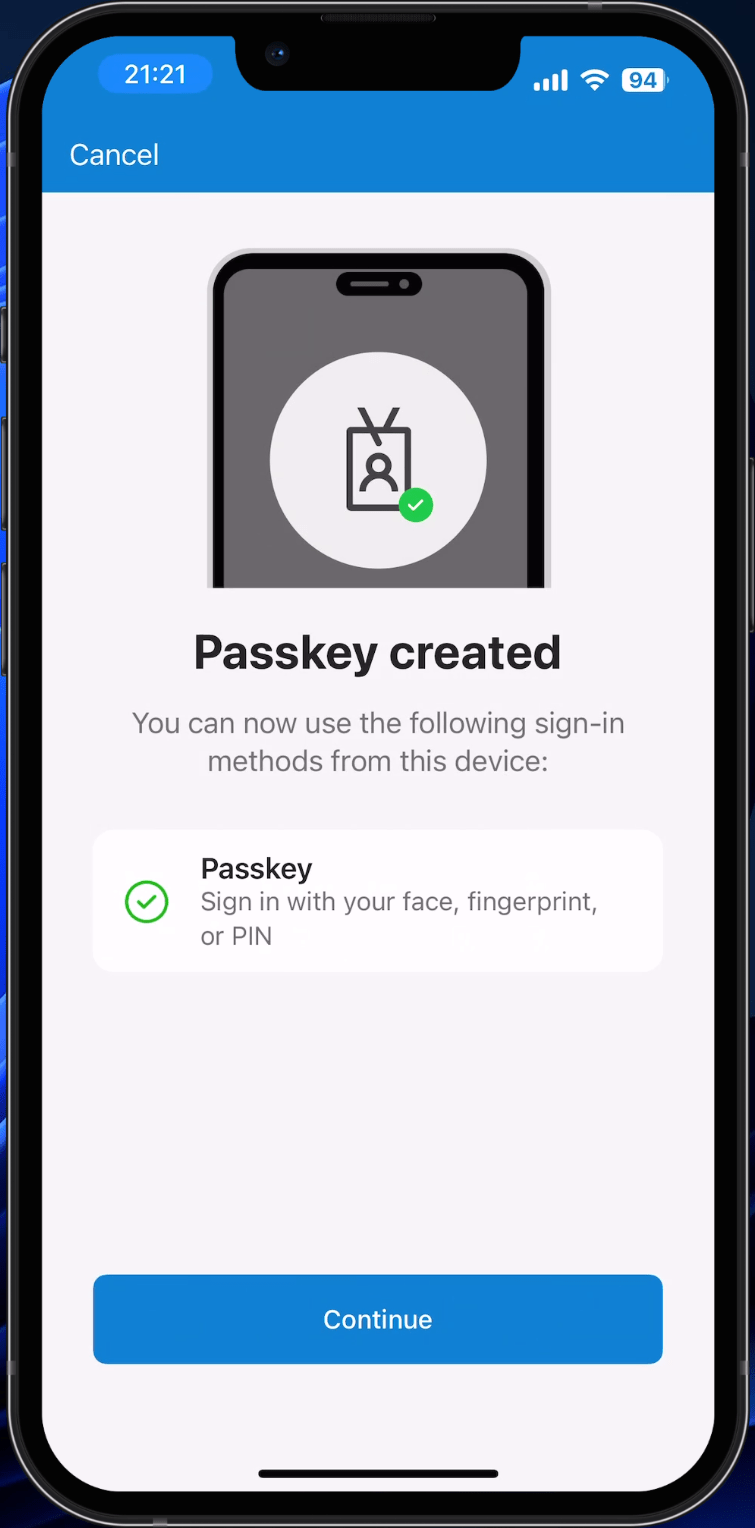
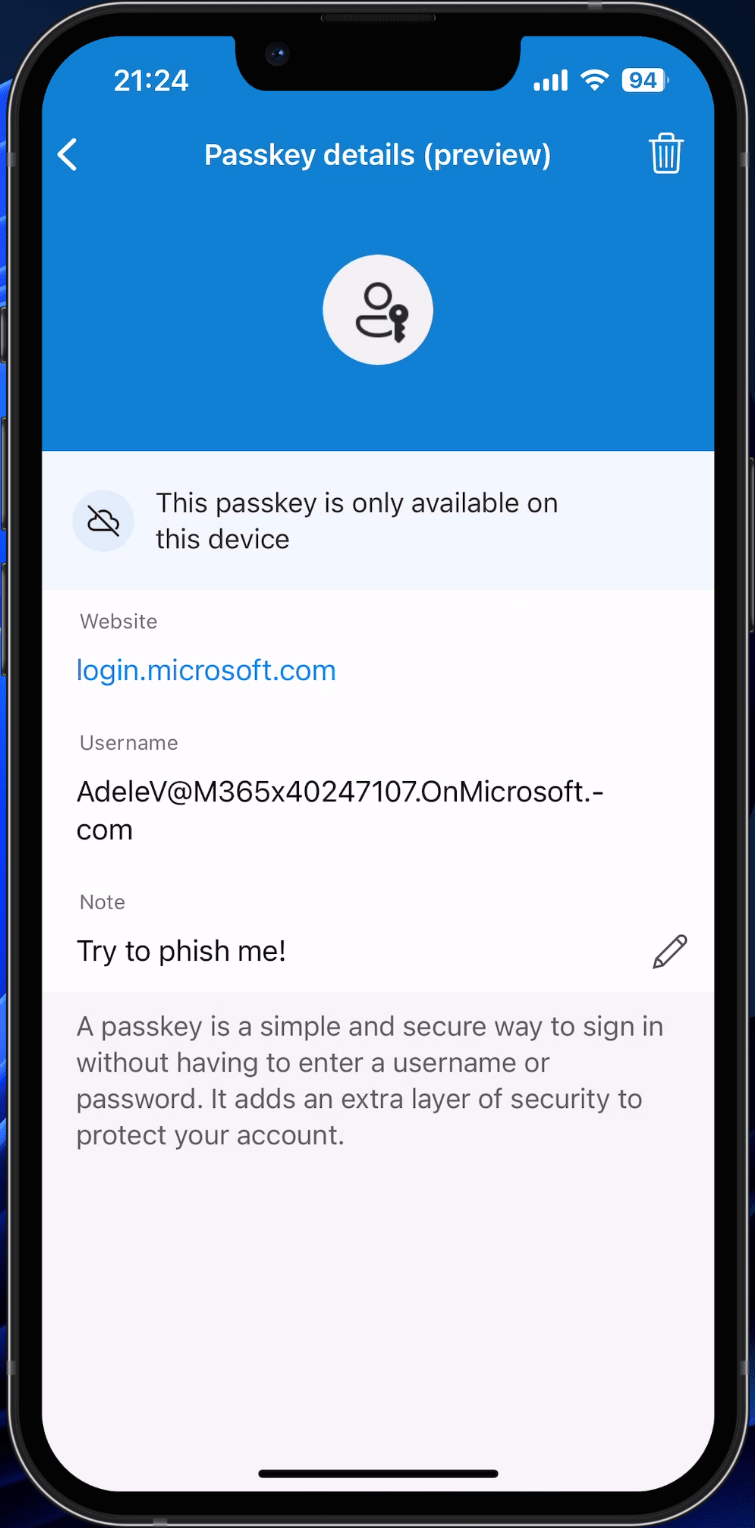
It’s also possible to register the passkey directly from the Authenticator app using a Temporary Access Pass.
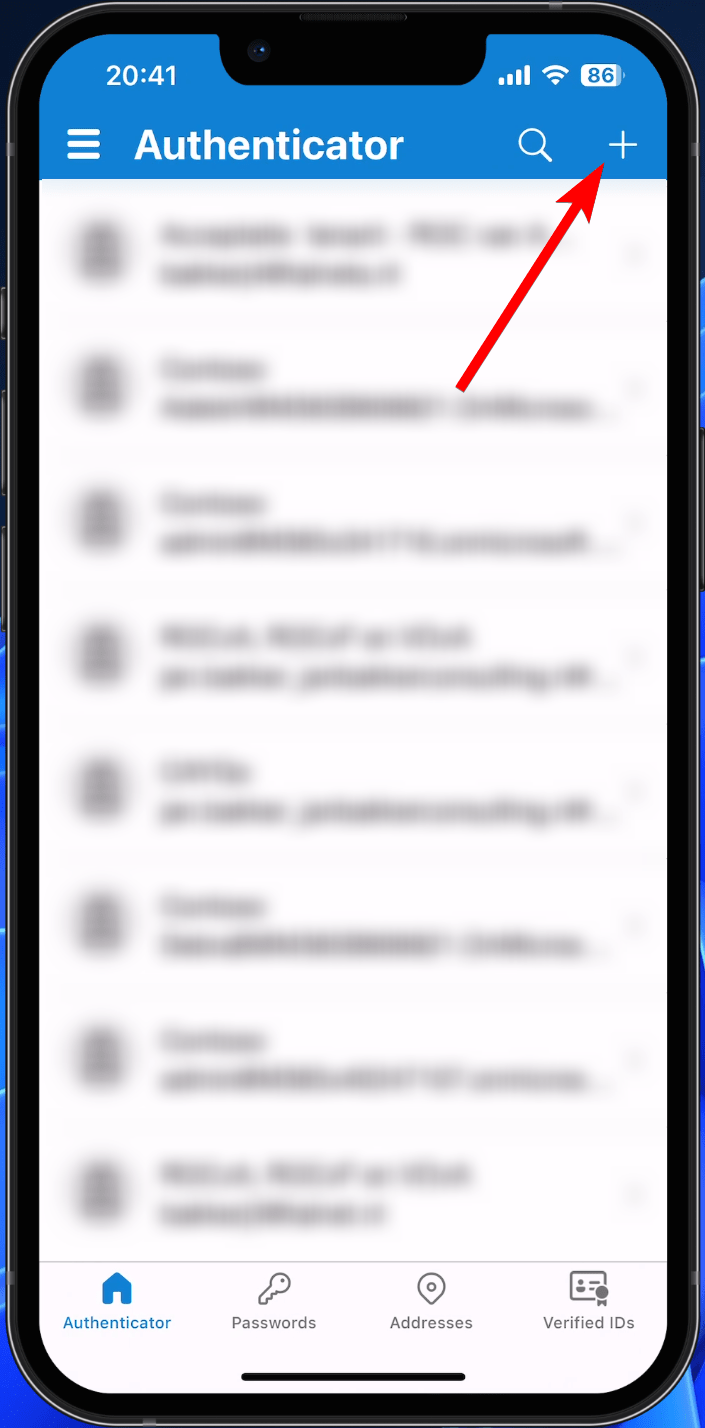
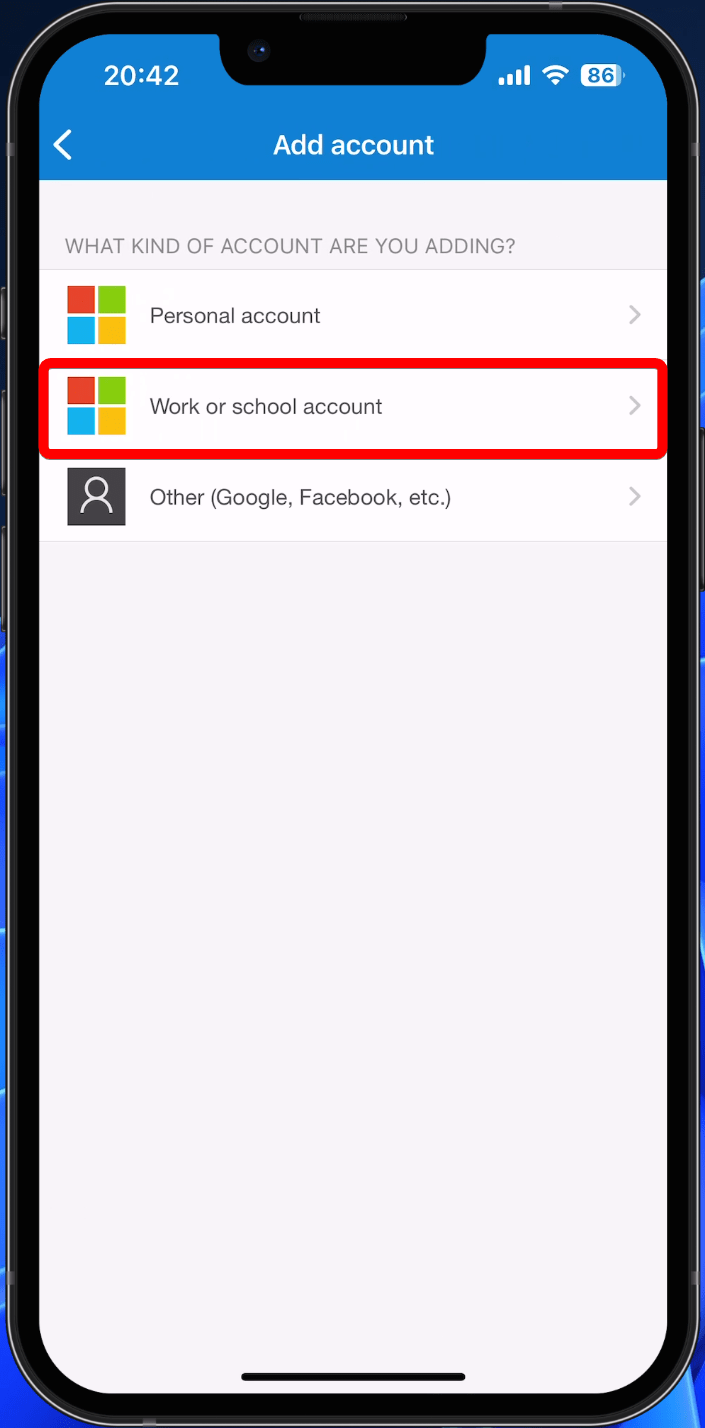
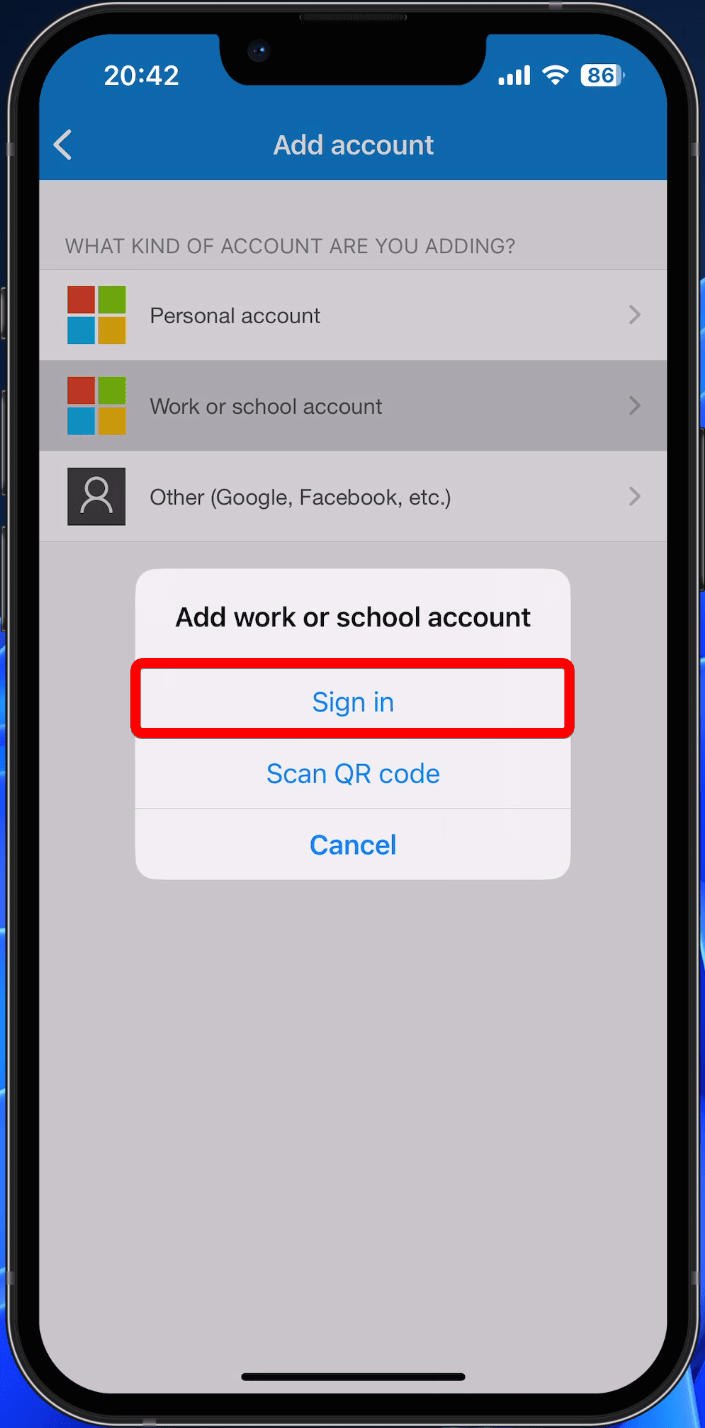
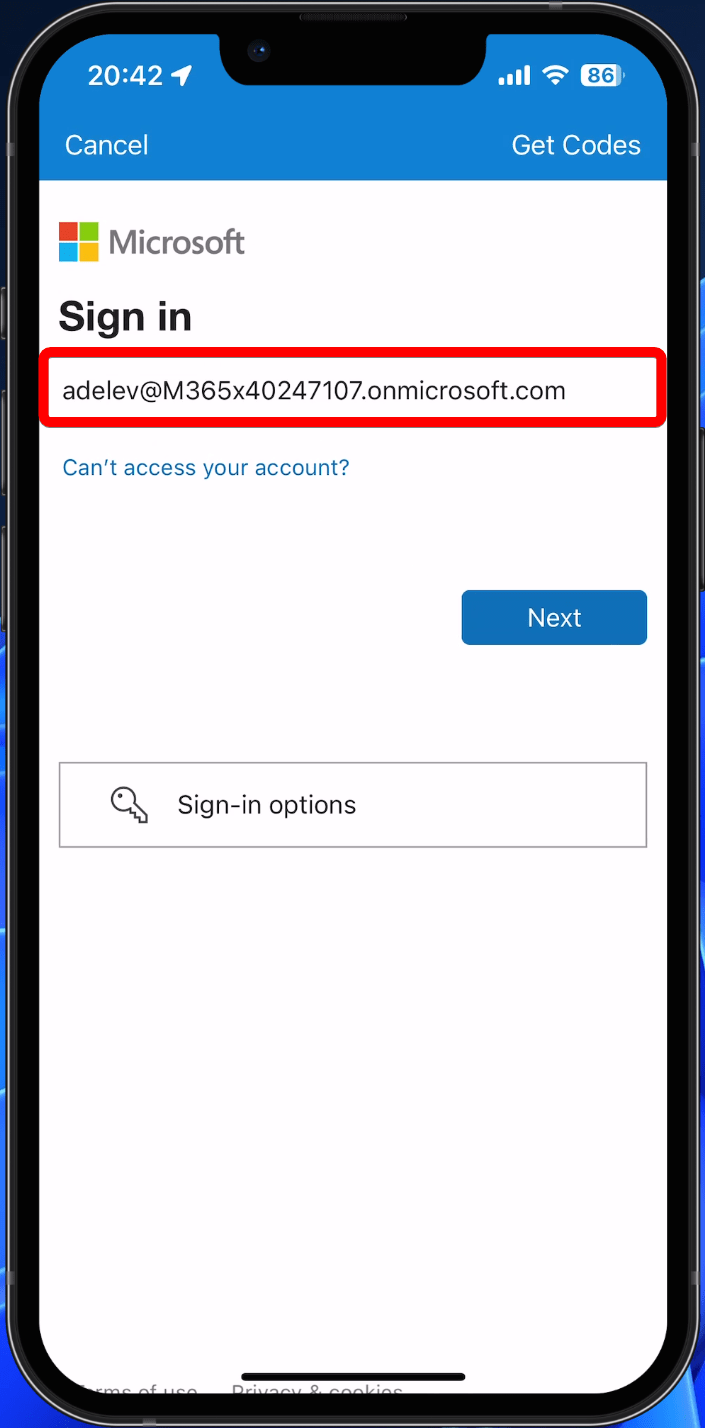
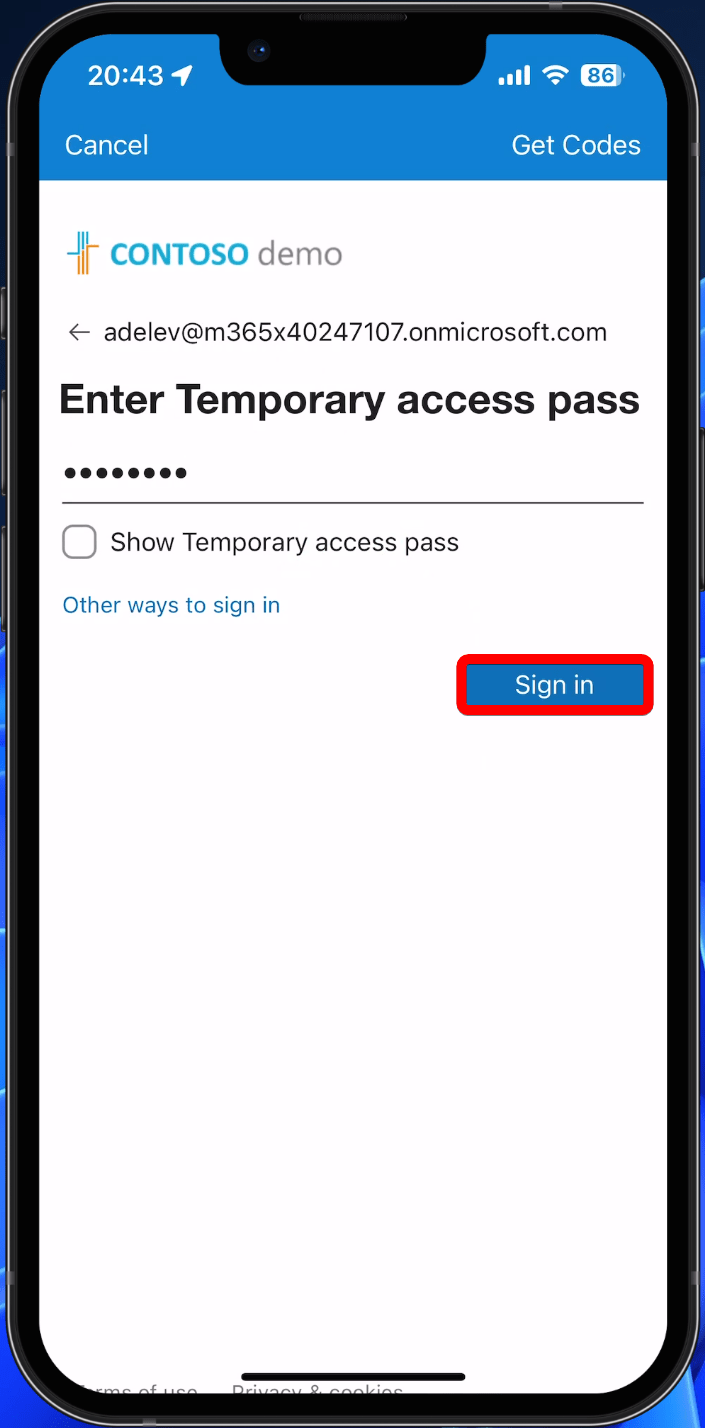
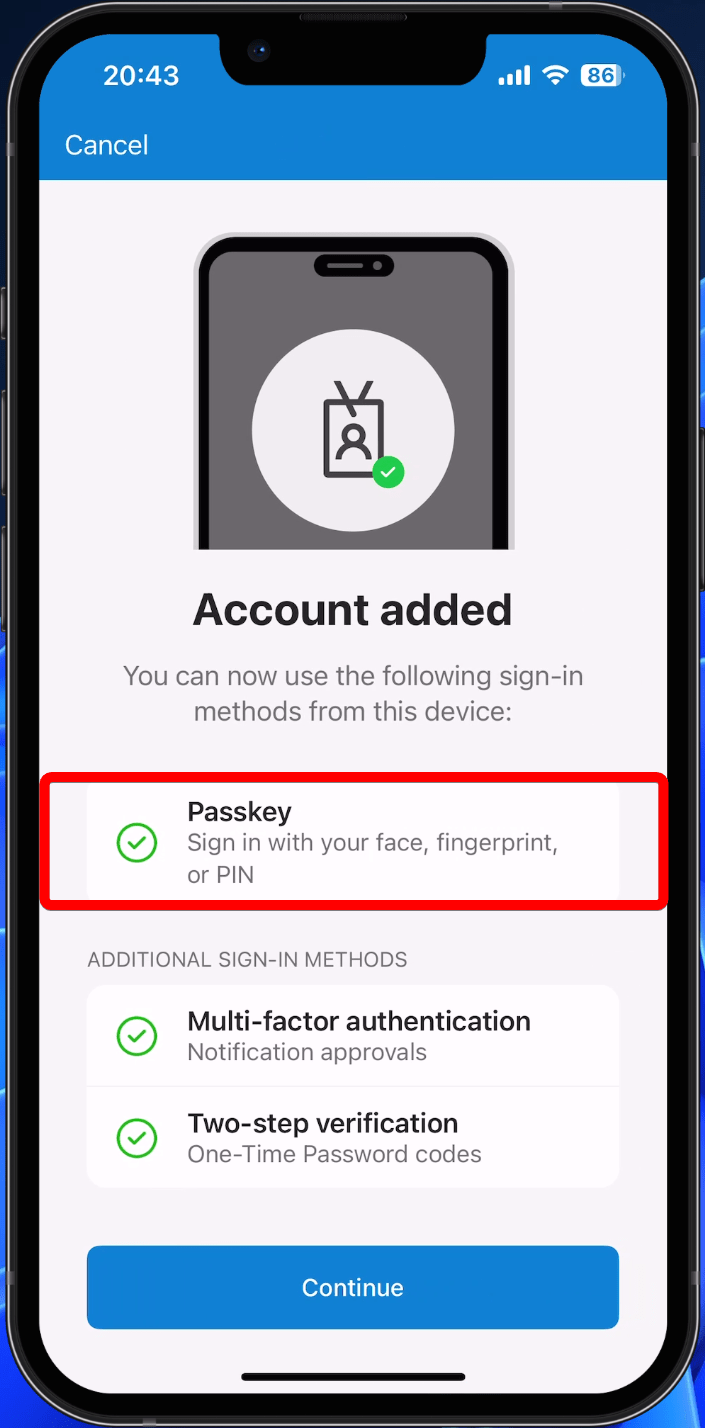
Note: if you are also eligible for other authentication methods like Passwordless Phone Sign-in (PSI), Two-step verification with a One-time password code (TOTP), or Mult-factor authentication using push notification, these methods are also registered. For PSI, the device also needs to be registered, so additional steps are required.
If the user is only eligible for passkeys, only device-bound passkeys will be registered.
End-user experience - iOS device sign-in Outlook app#
- User opens their Outlook app on their mobile device.
- User enters their username and taps on “Next”.
Note: If the user’s most recently used auth method is not a passkey in Authenticator app or a security key, then the user must click on “Use Face, fingerprint, PIN, or security key instead” or “Other ways to sign-in” then “Face, fingerprint, PIN, or security key” to prompt the operating system dialog in the next step.
- Since the user has a passkey setup in the Authenticator app, the OS prompts the user to sign-in with the passkey stored in their Authenticator app.\
- User goes through the bio/device PIN to sign-in with their passkey and they are then logged in.
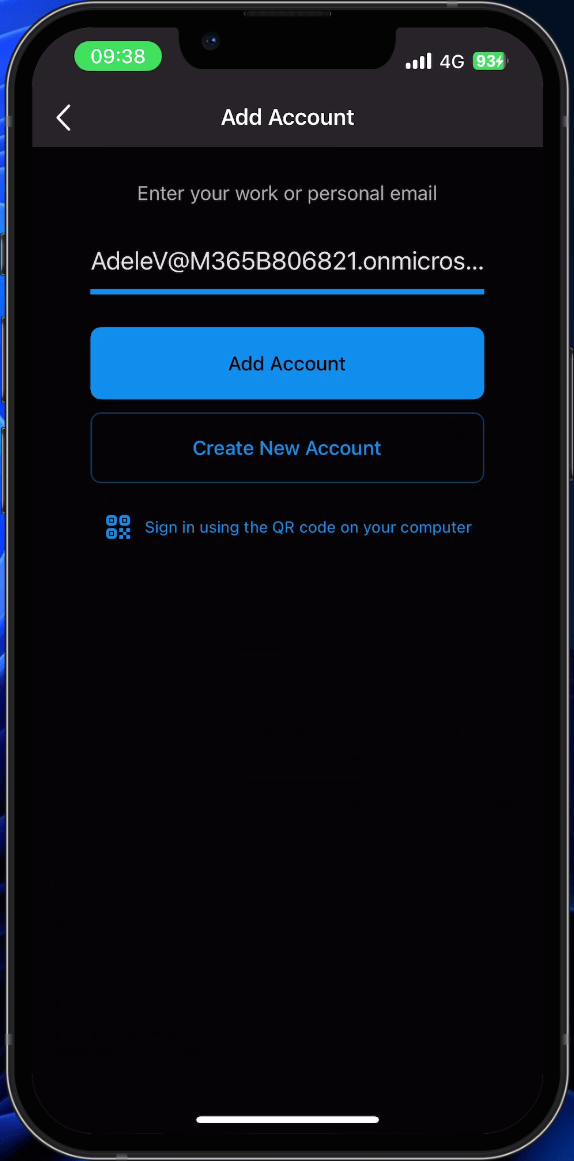
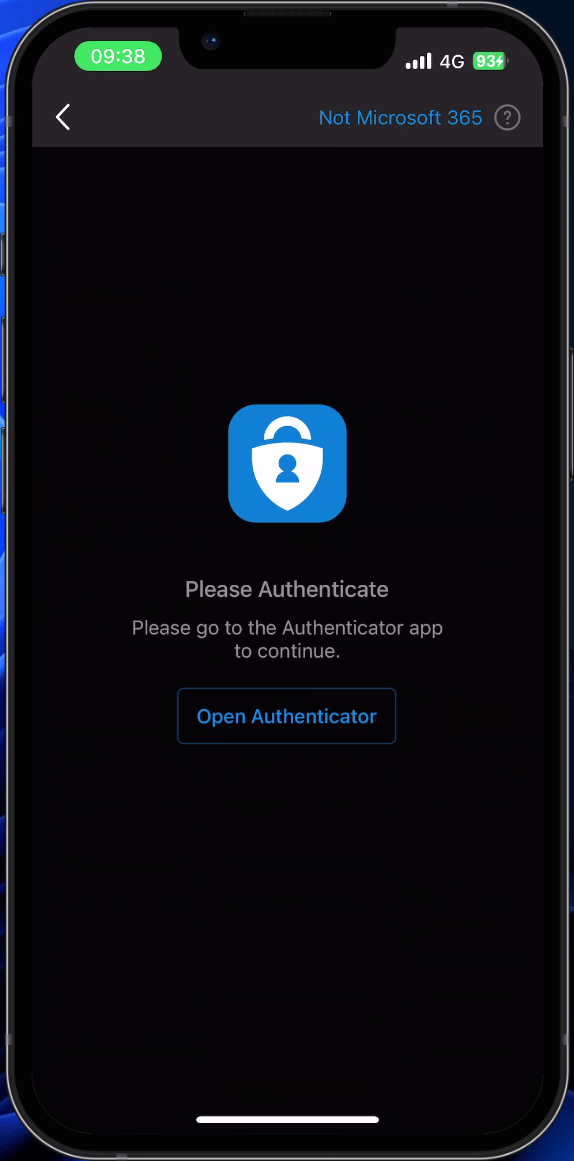
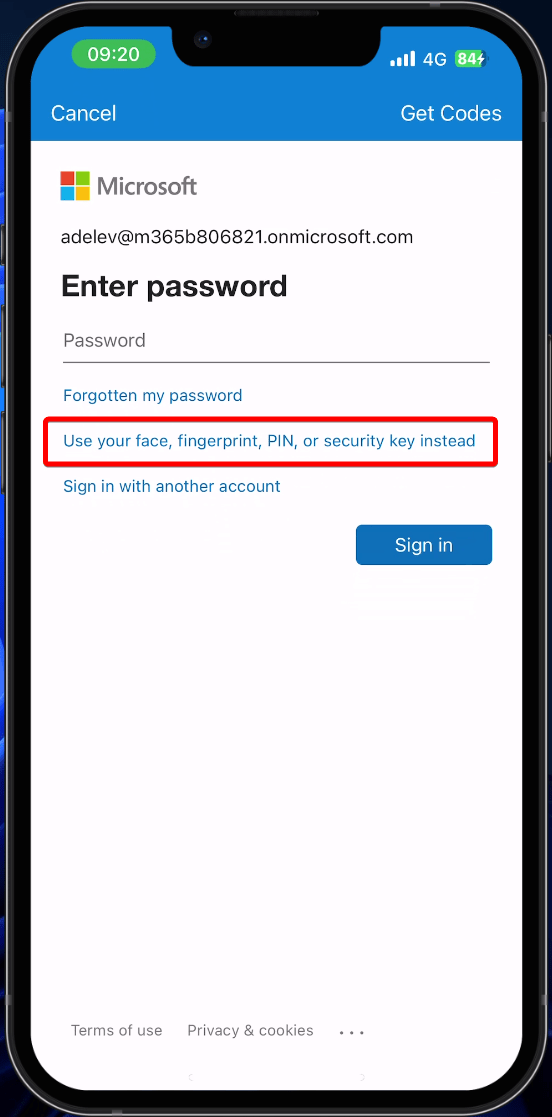
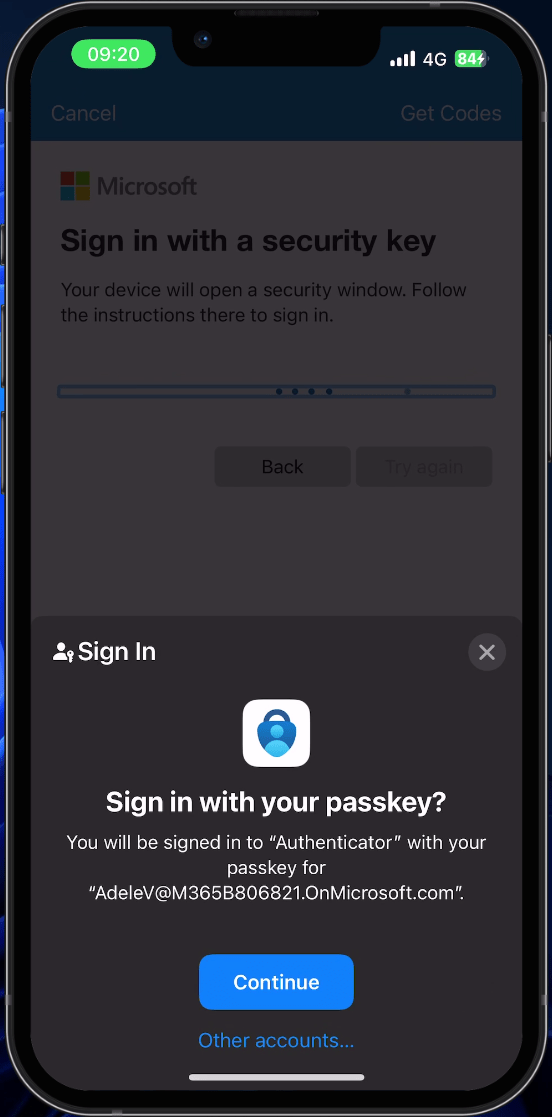
This experience is similar to MacOs and the Outlook app, but is only supported when the device meets the following requirements:
- Device is signed into the latest installed version of Microsoft Intune Company Portal
- Device is enrolled in mobile device management (MDM)
- Device is using the Microsoft Enterprise SSO plug-in
Cross-device user experience - Windows#
To sign-in using a passkey on Windows, follow these steps:
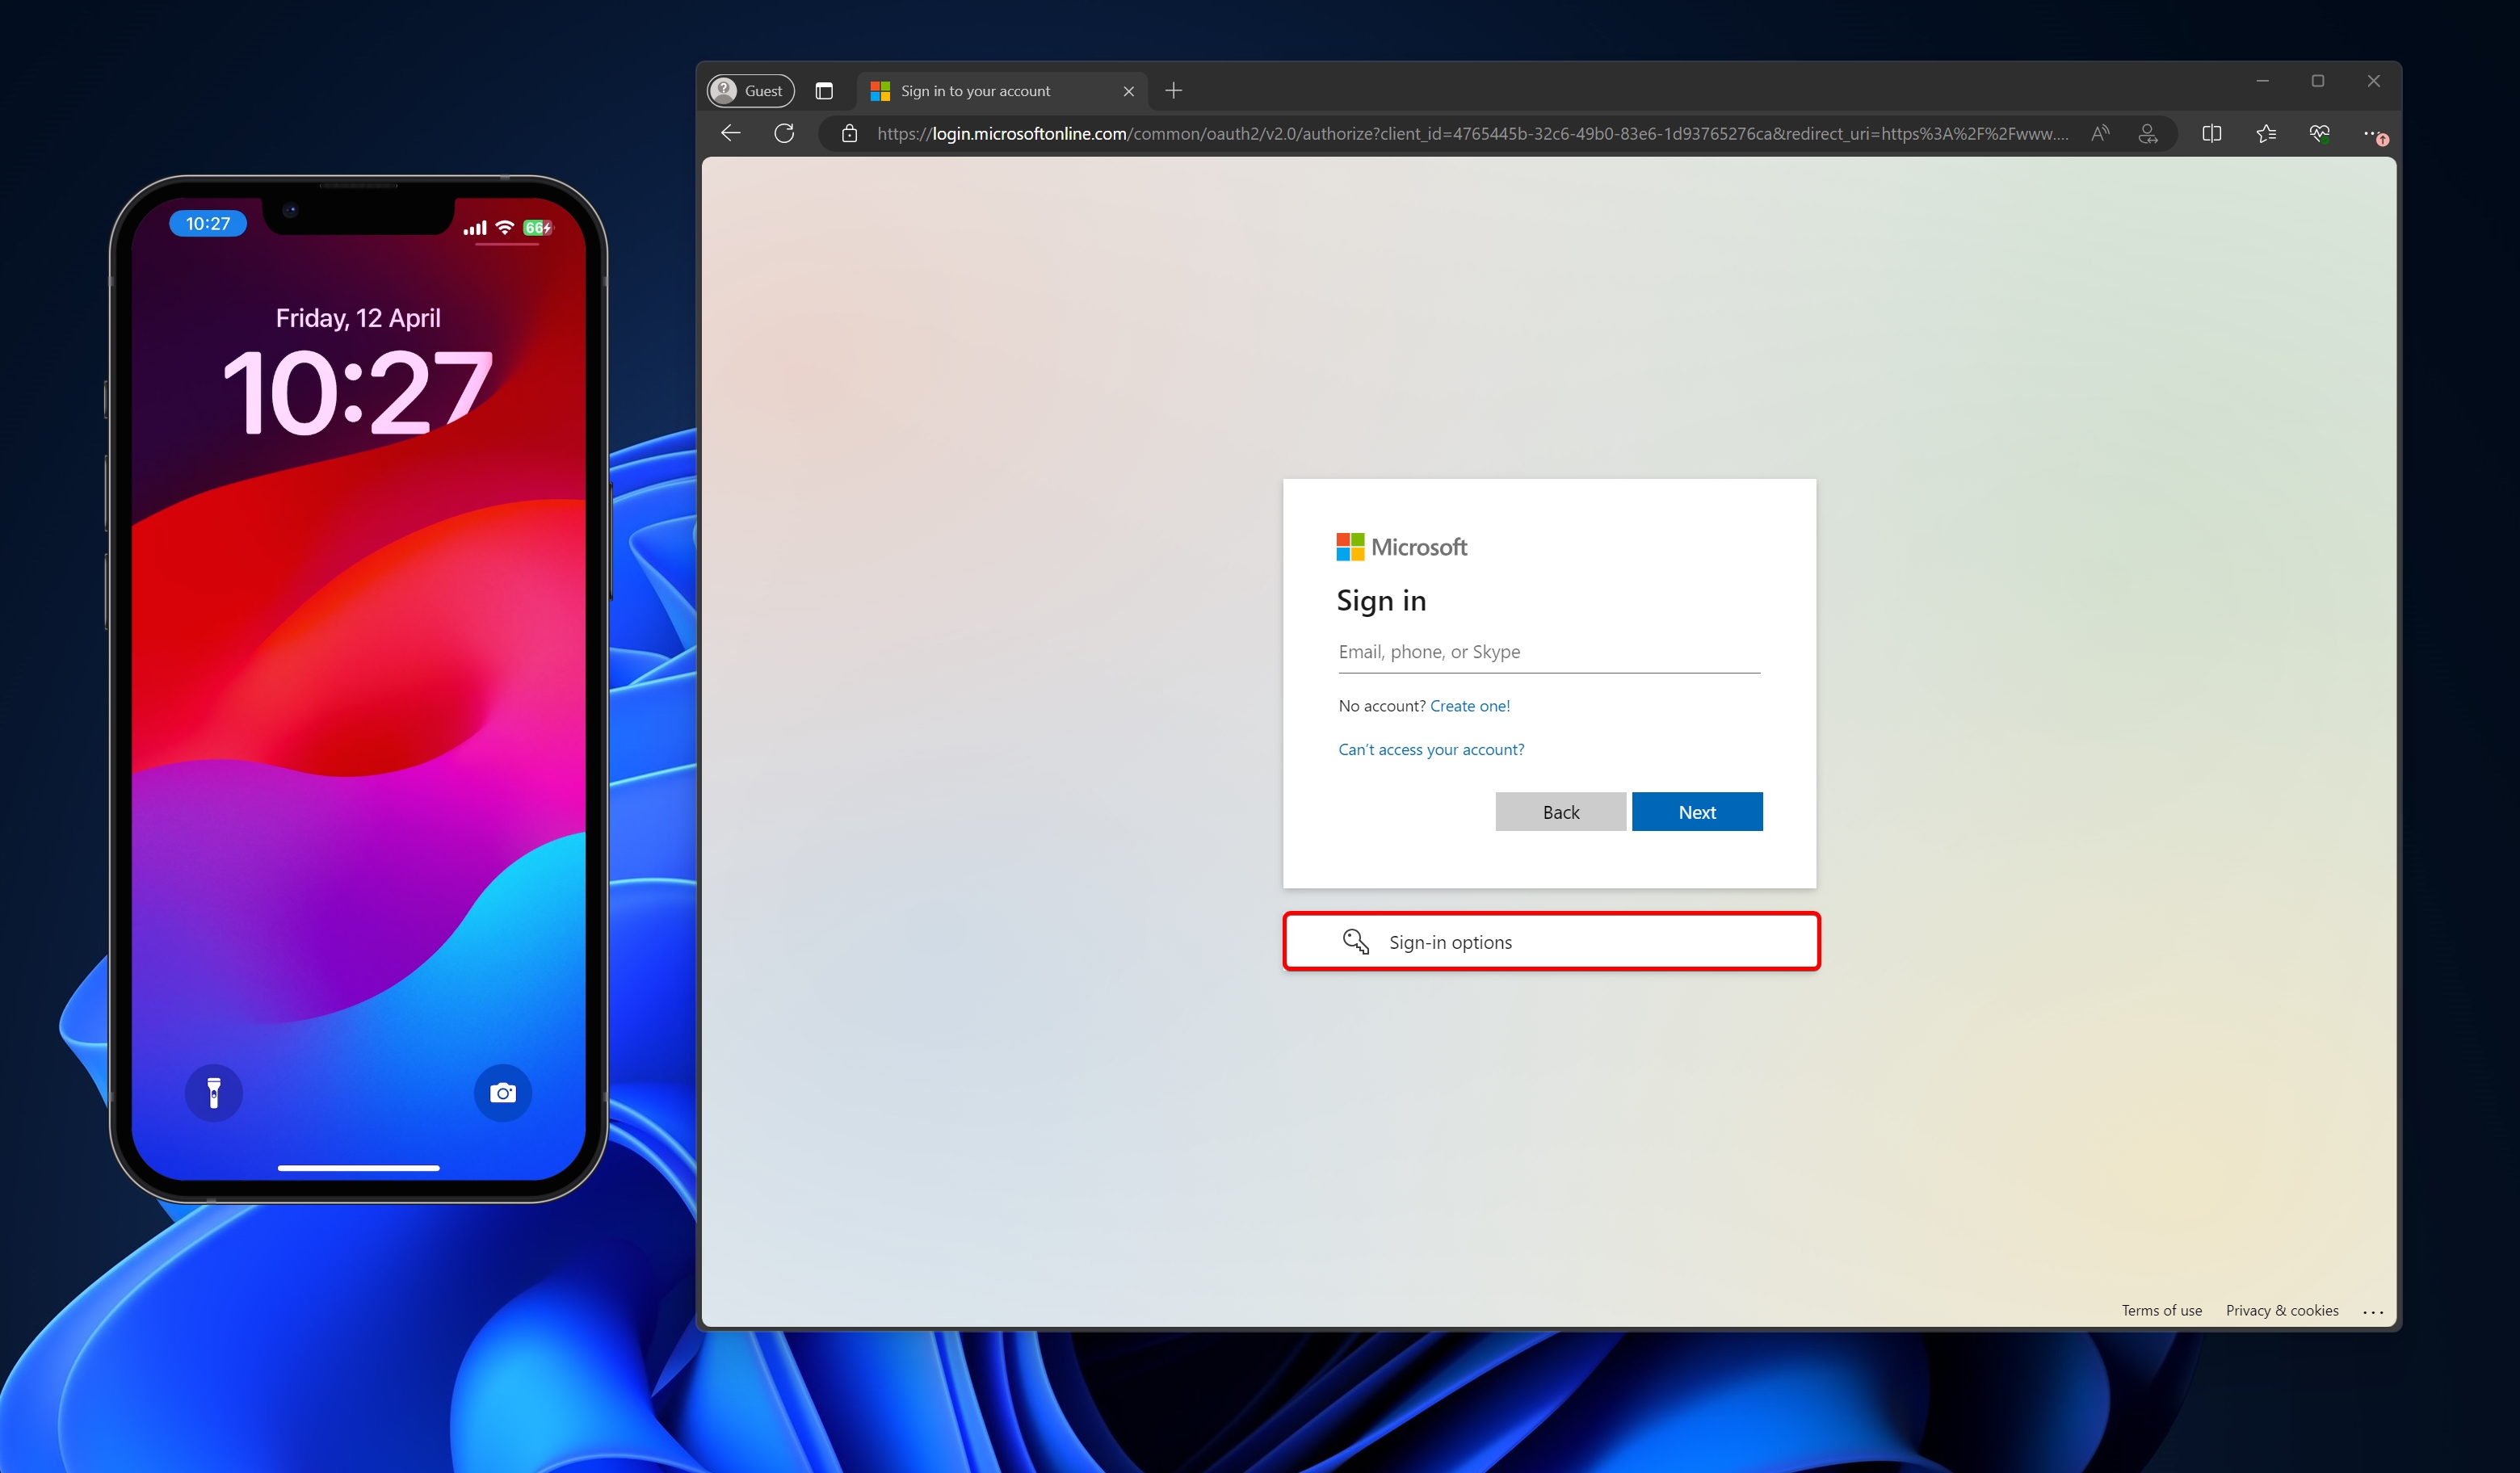
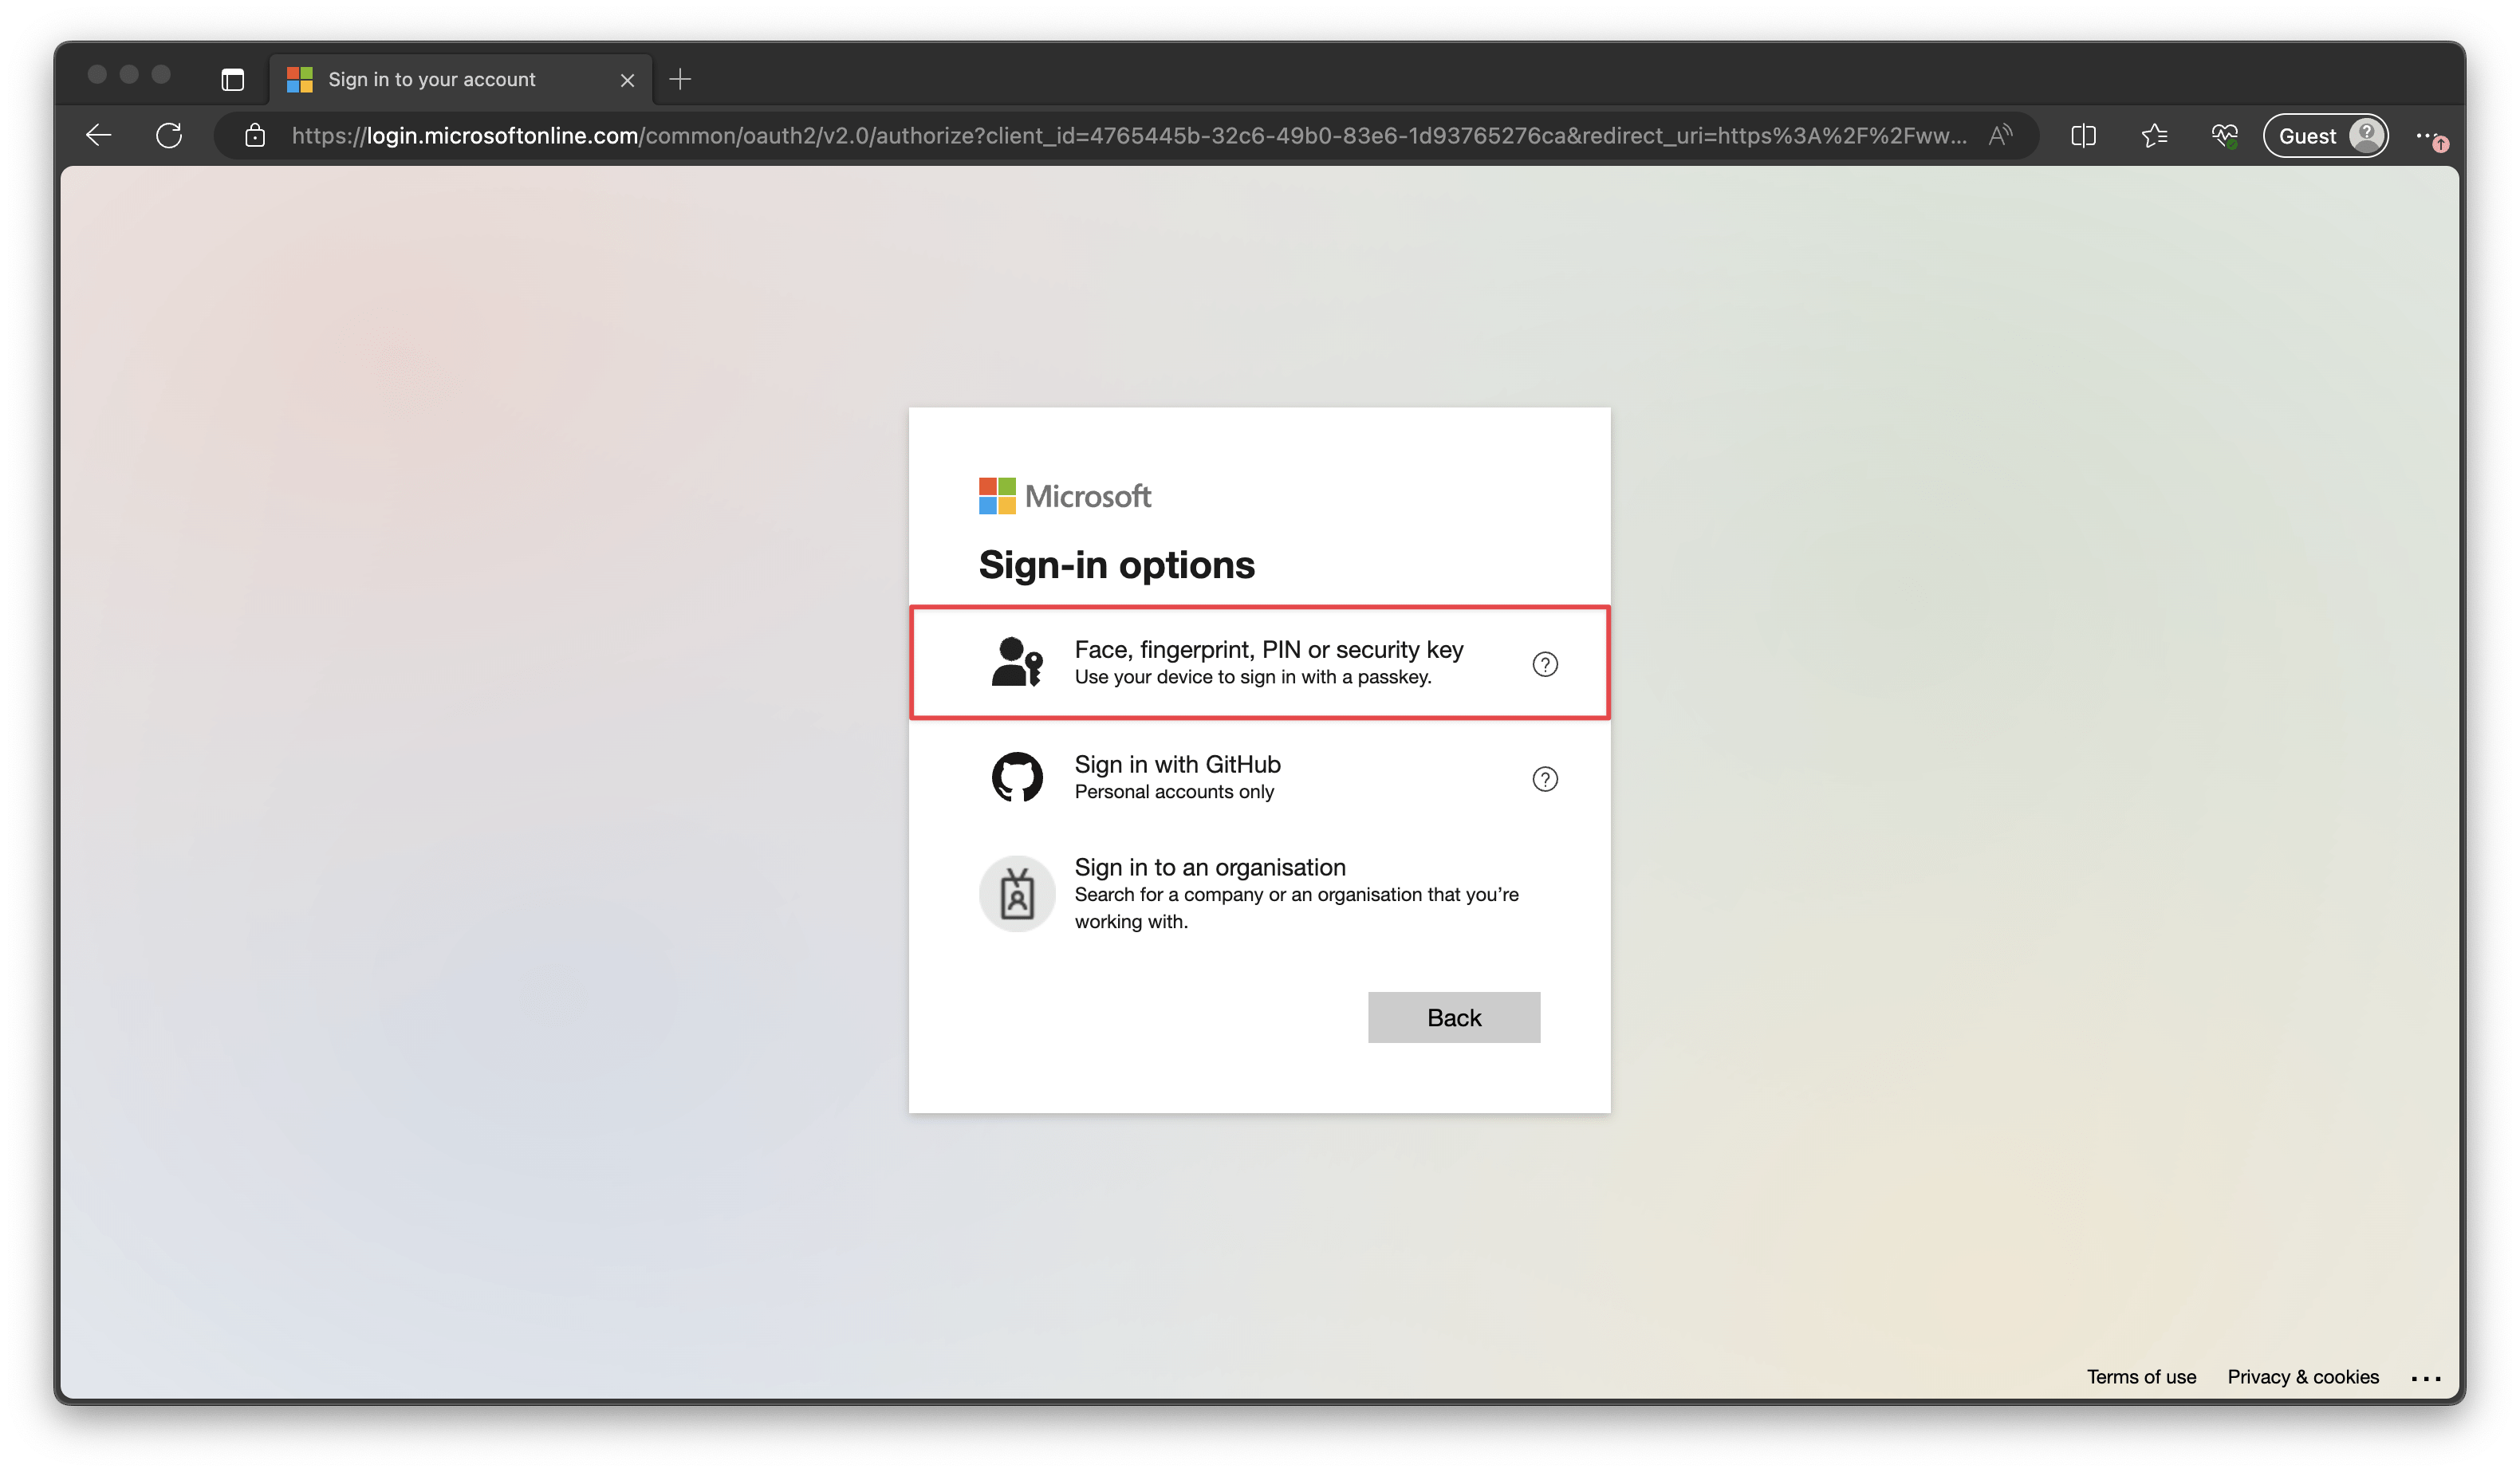
On the sign-in screen, select Sign-in options.
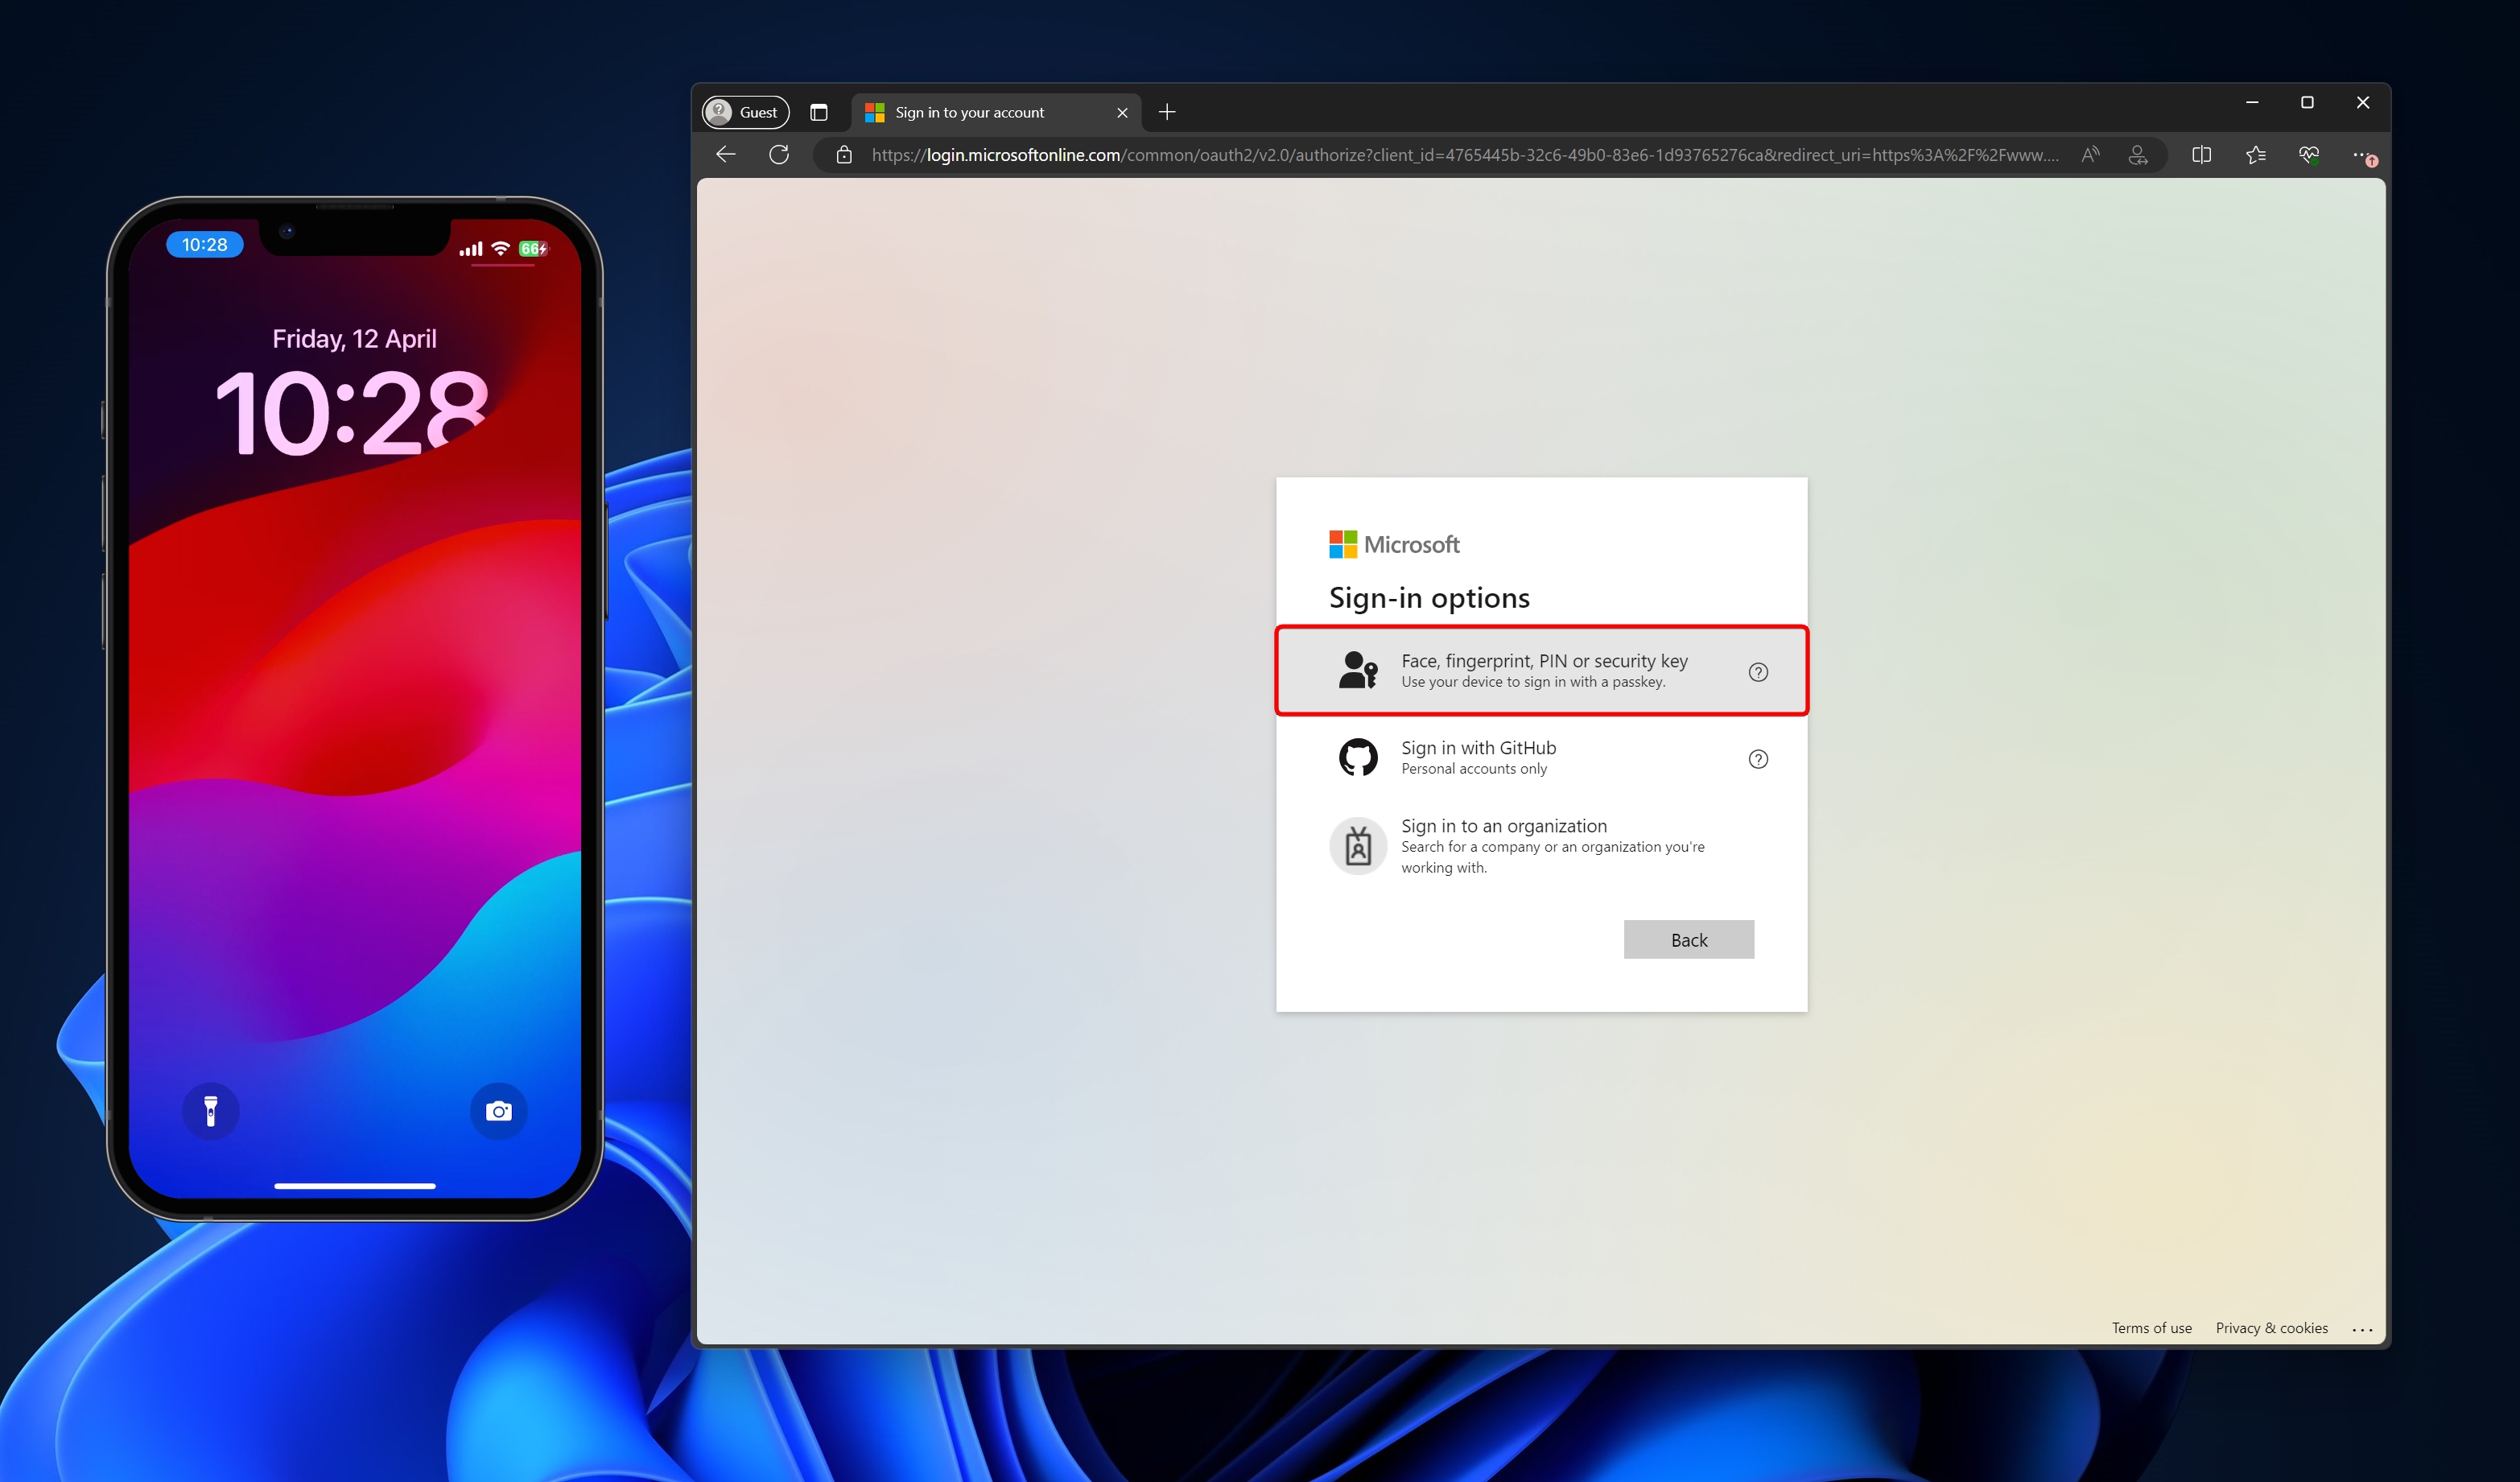
Next, pick Face, fingerprint, PIN or security key.
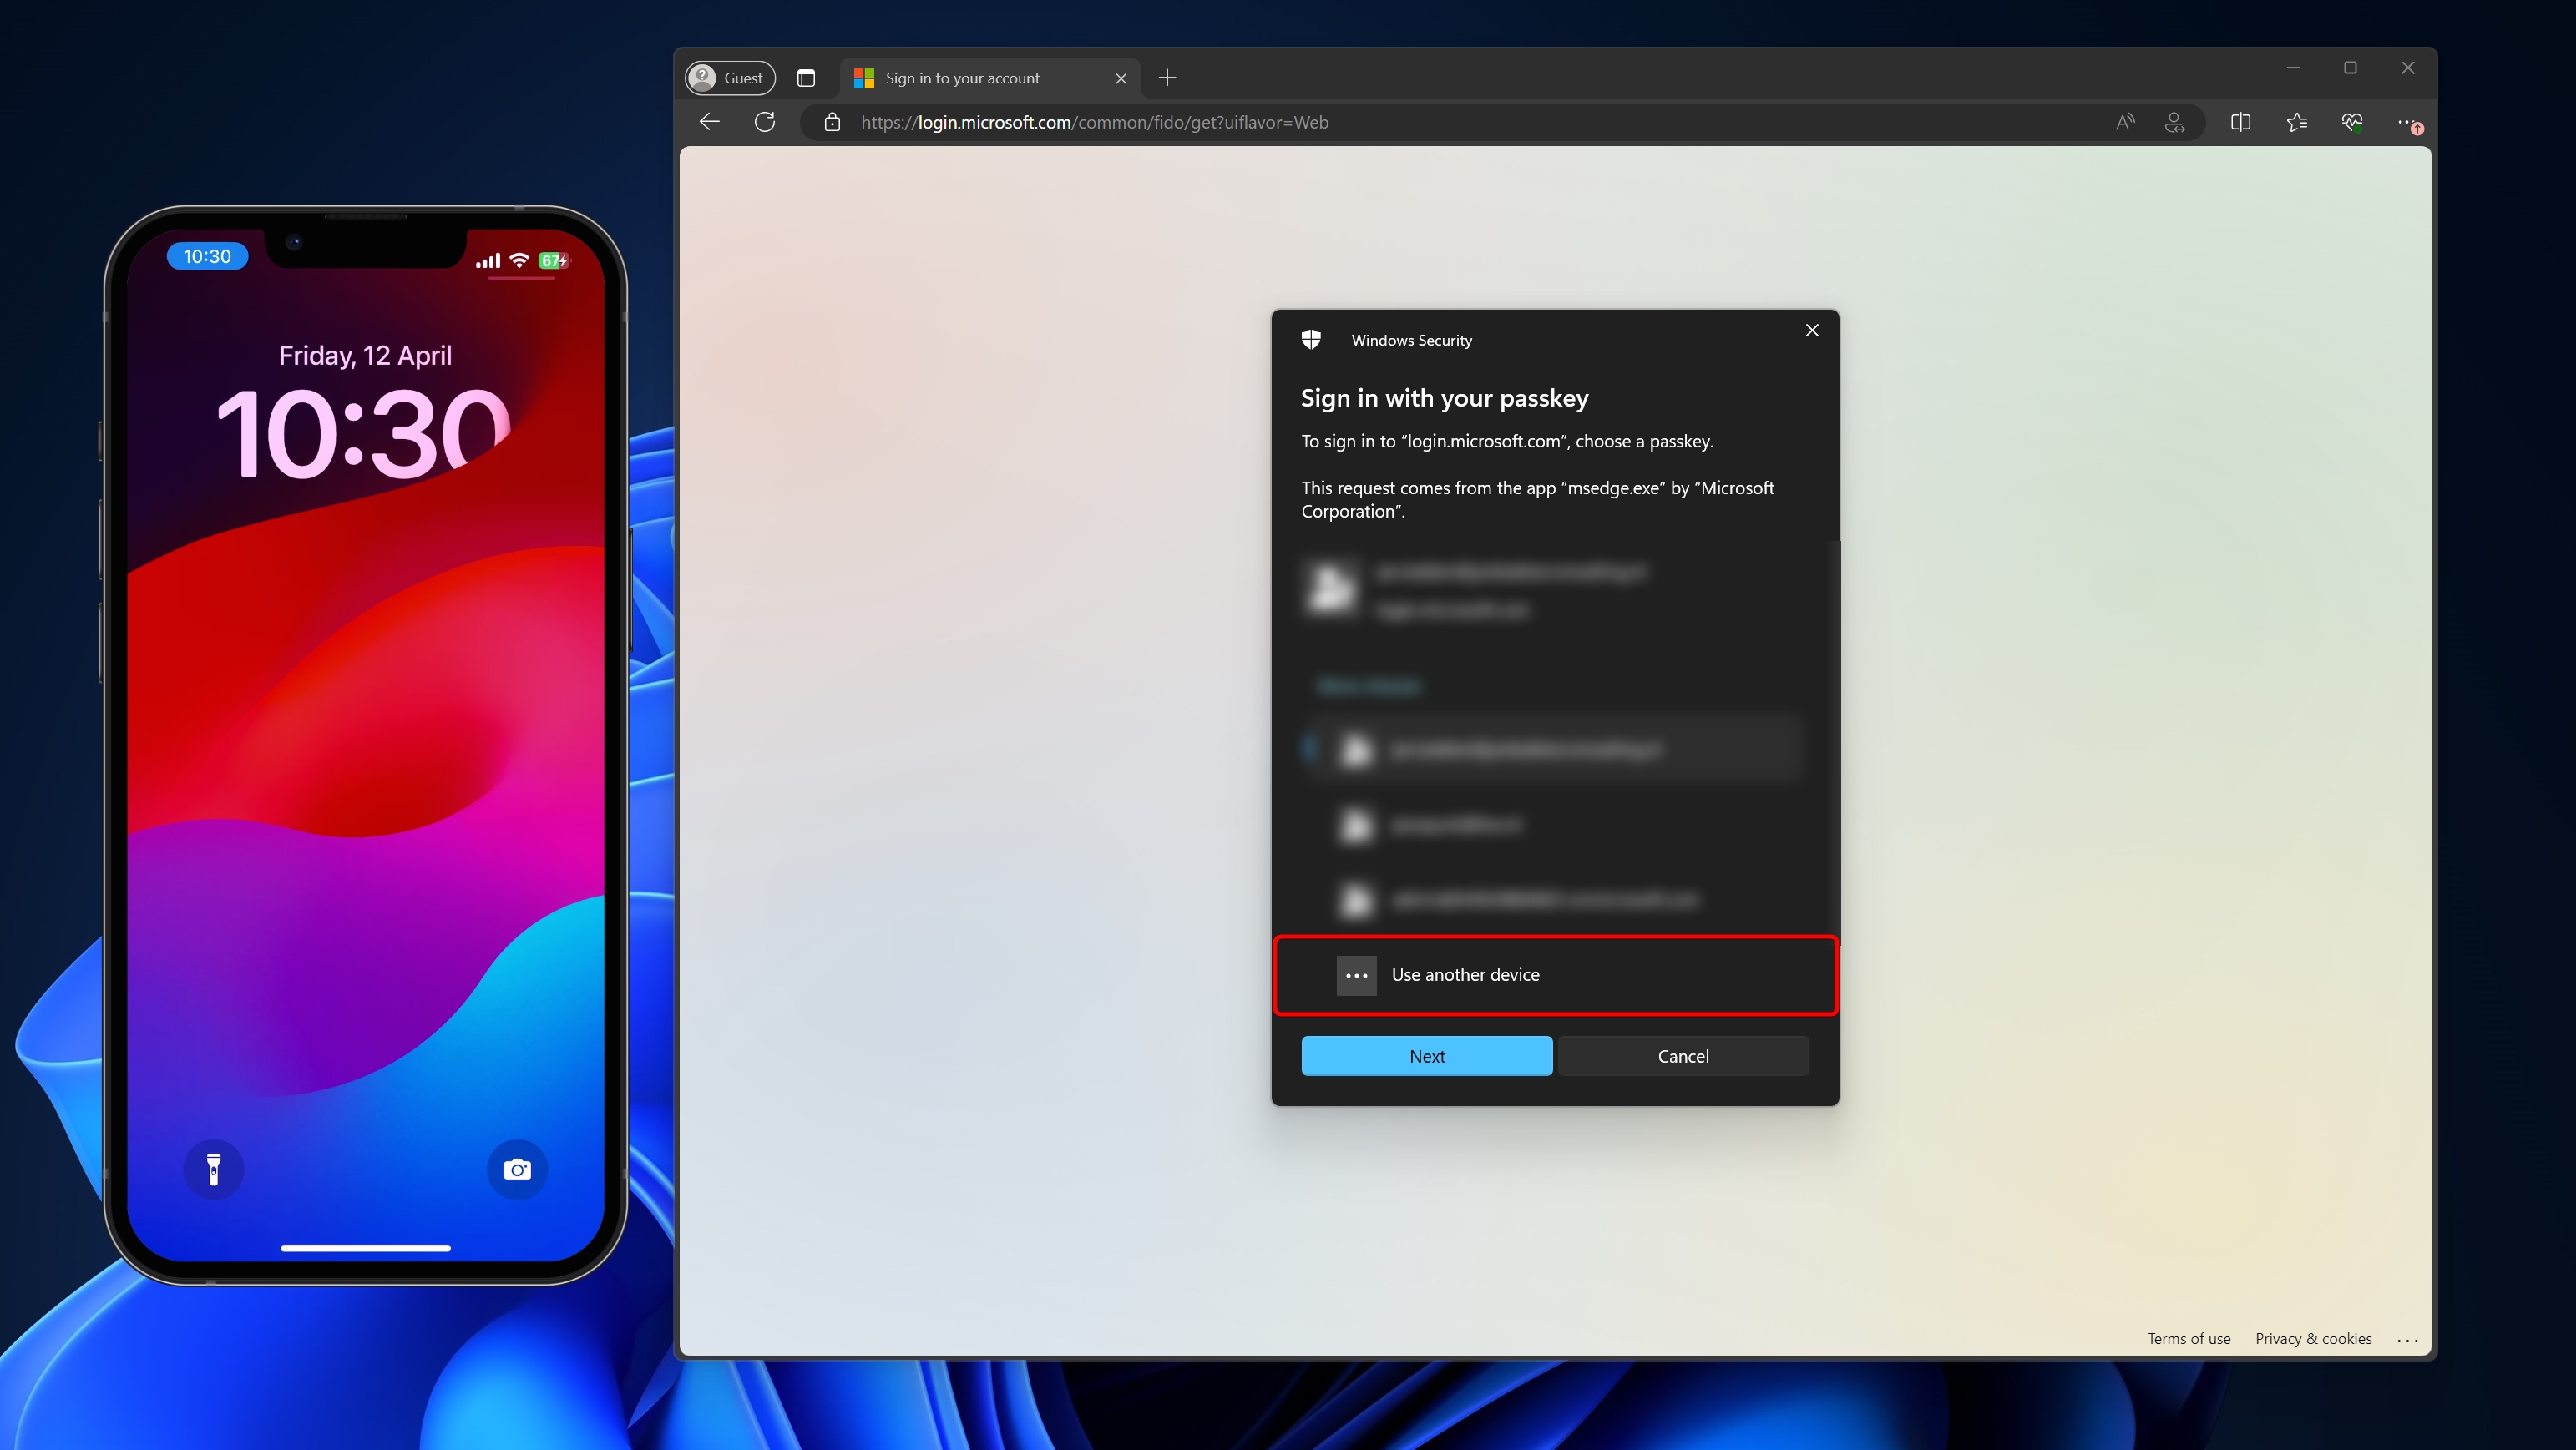
Select: Use another device.
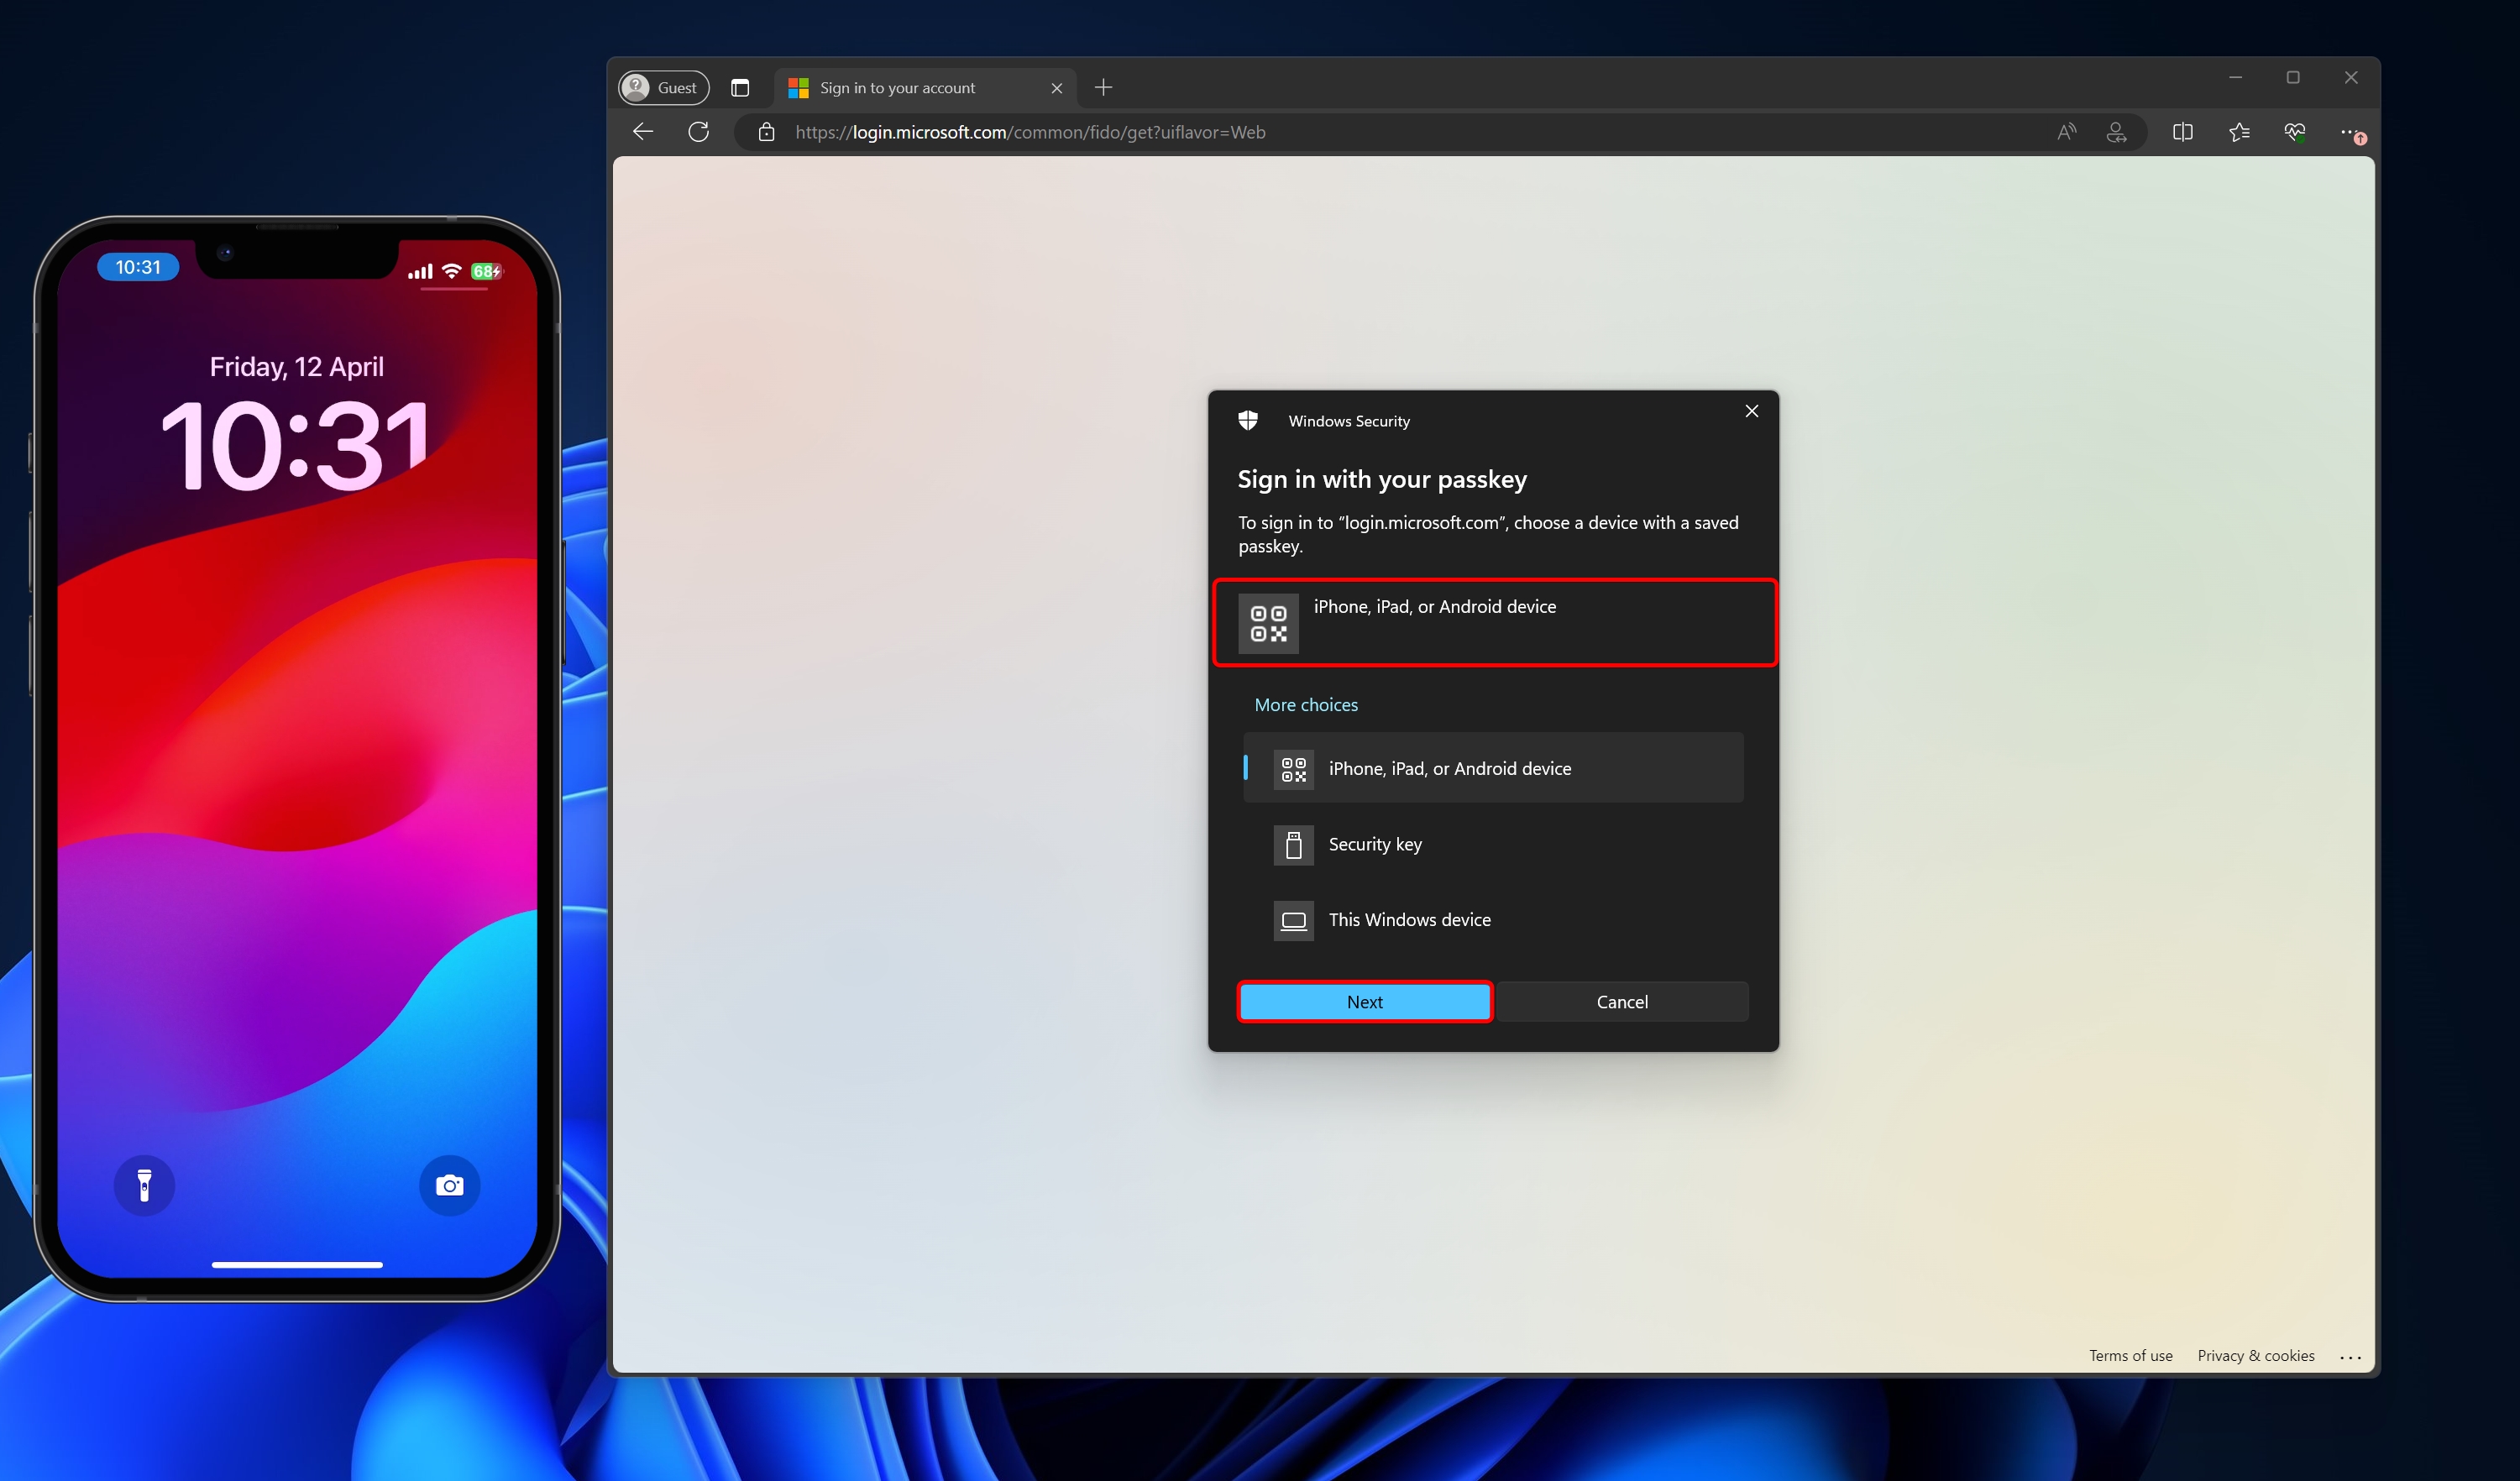
In this step, select iPhone, iPad or Android device.
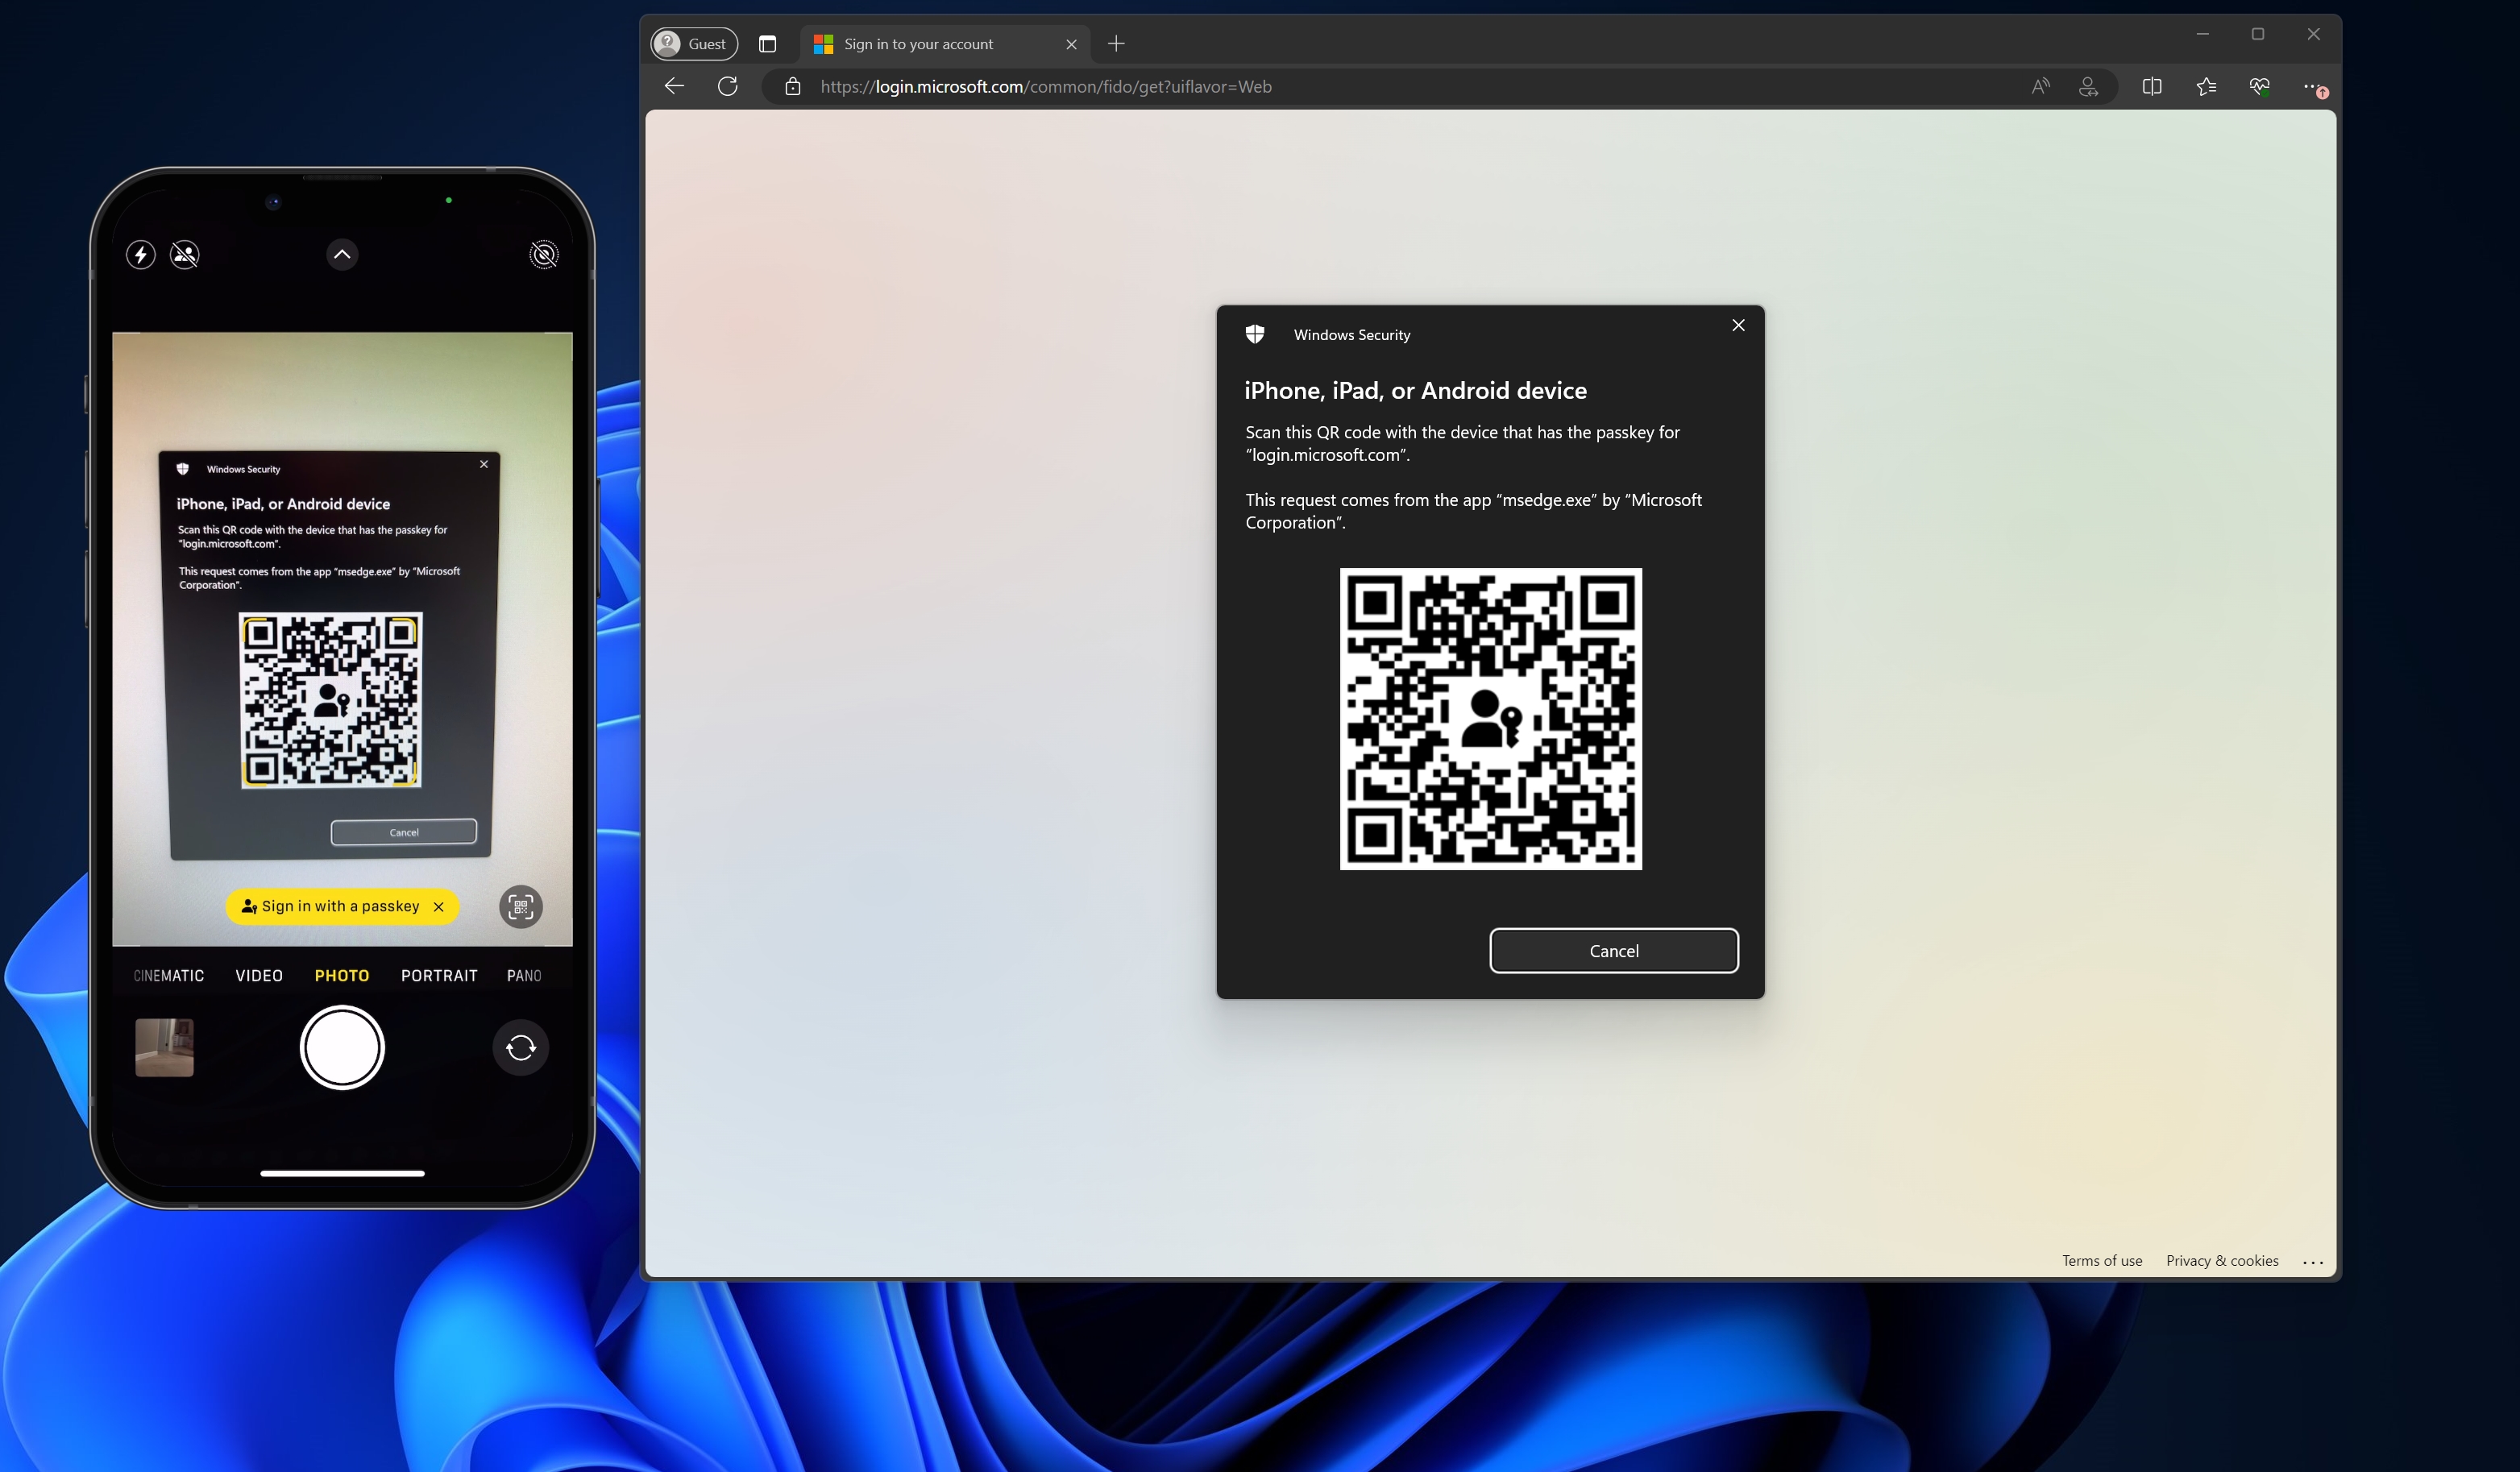
For iOS, use the system camera to scan the QR code. Android users can also use the QR scanner from the Authenticator app. When prompted, select: Sign in with a passkey.
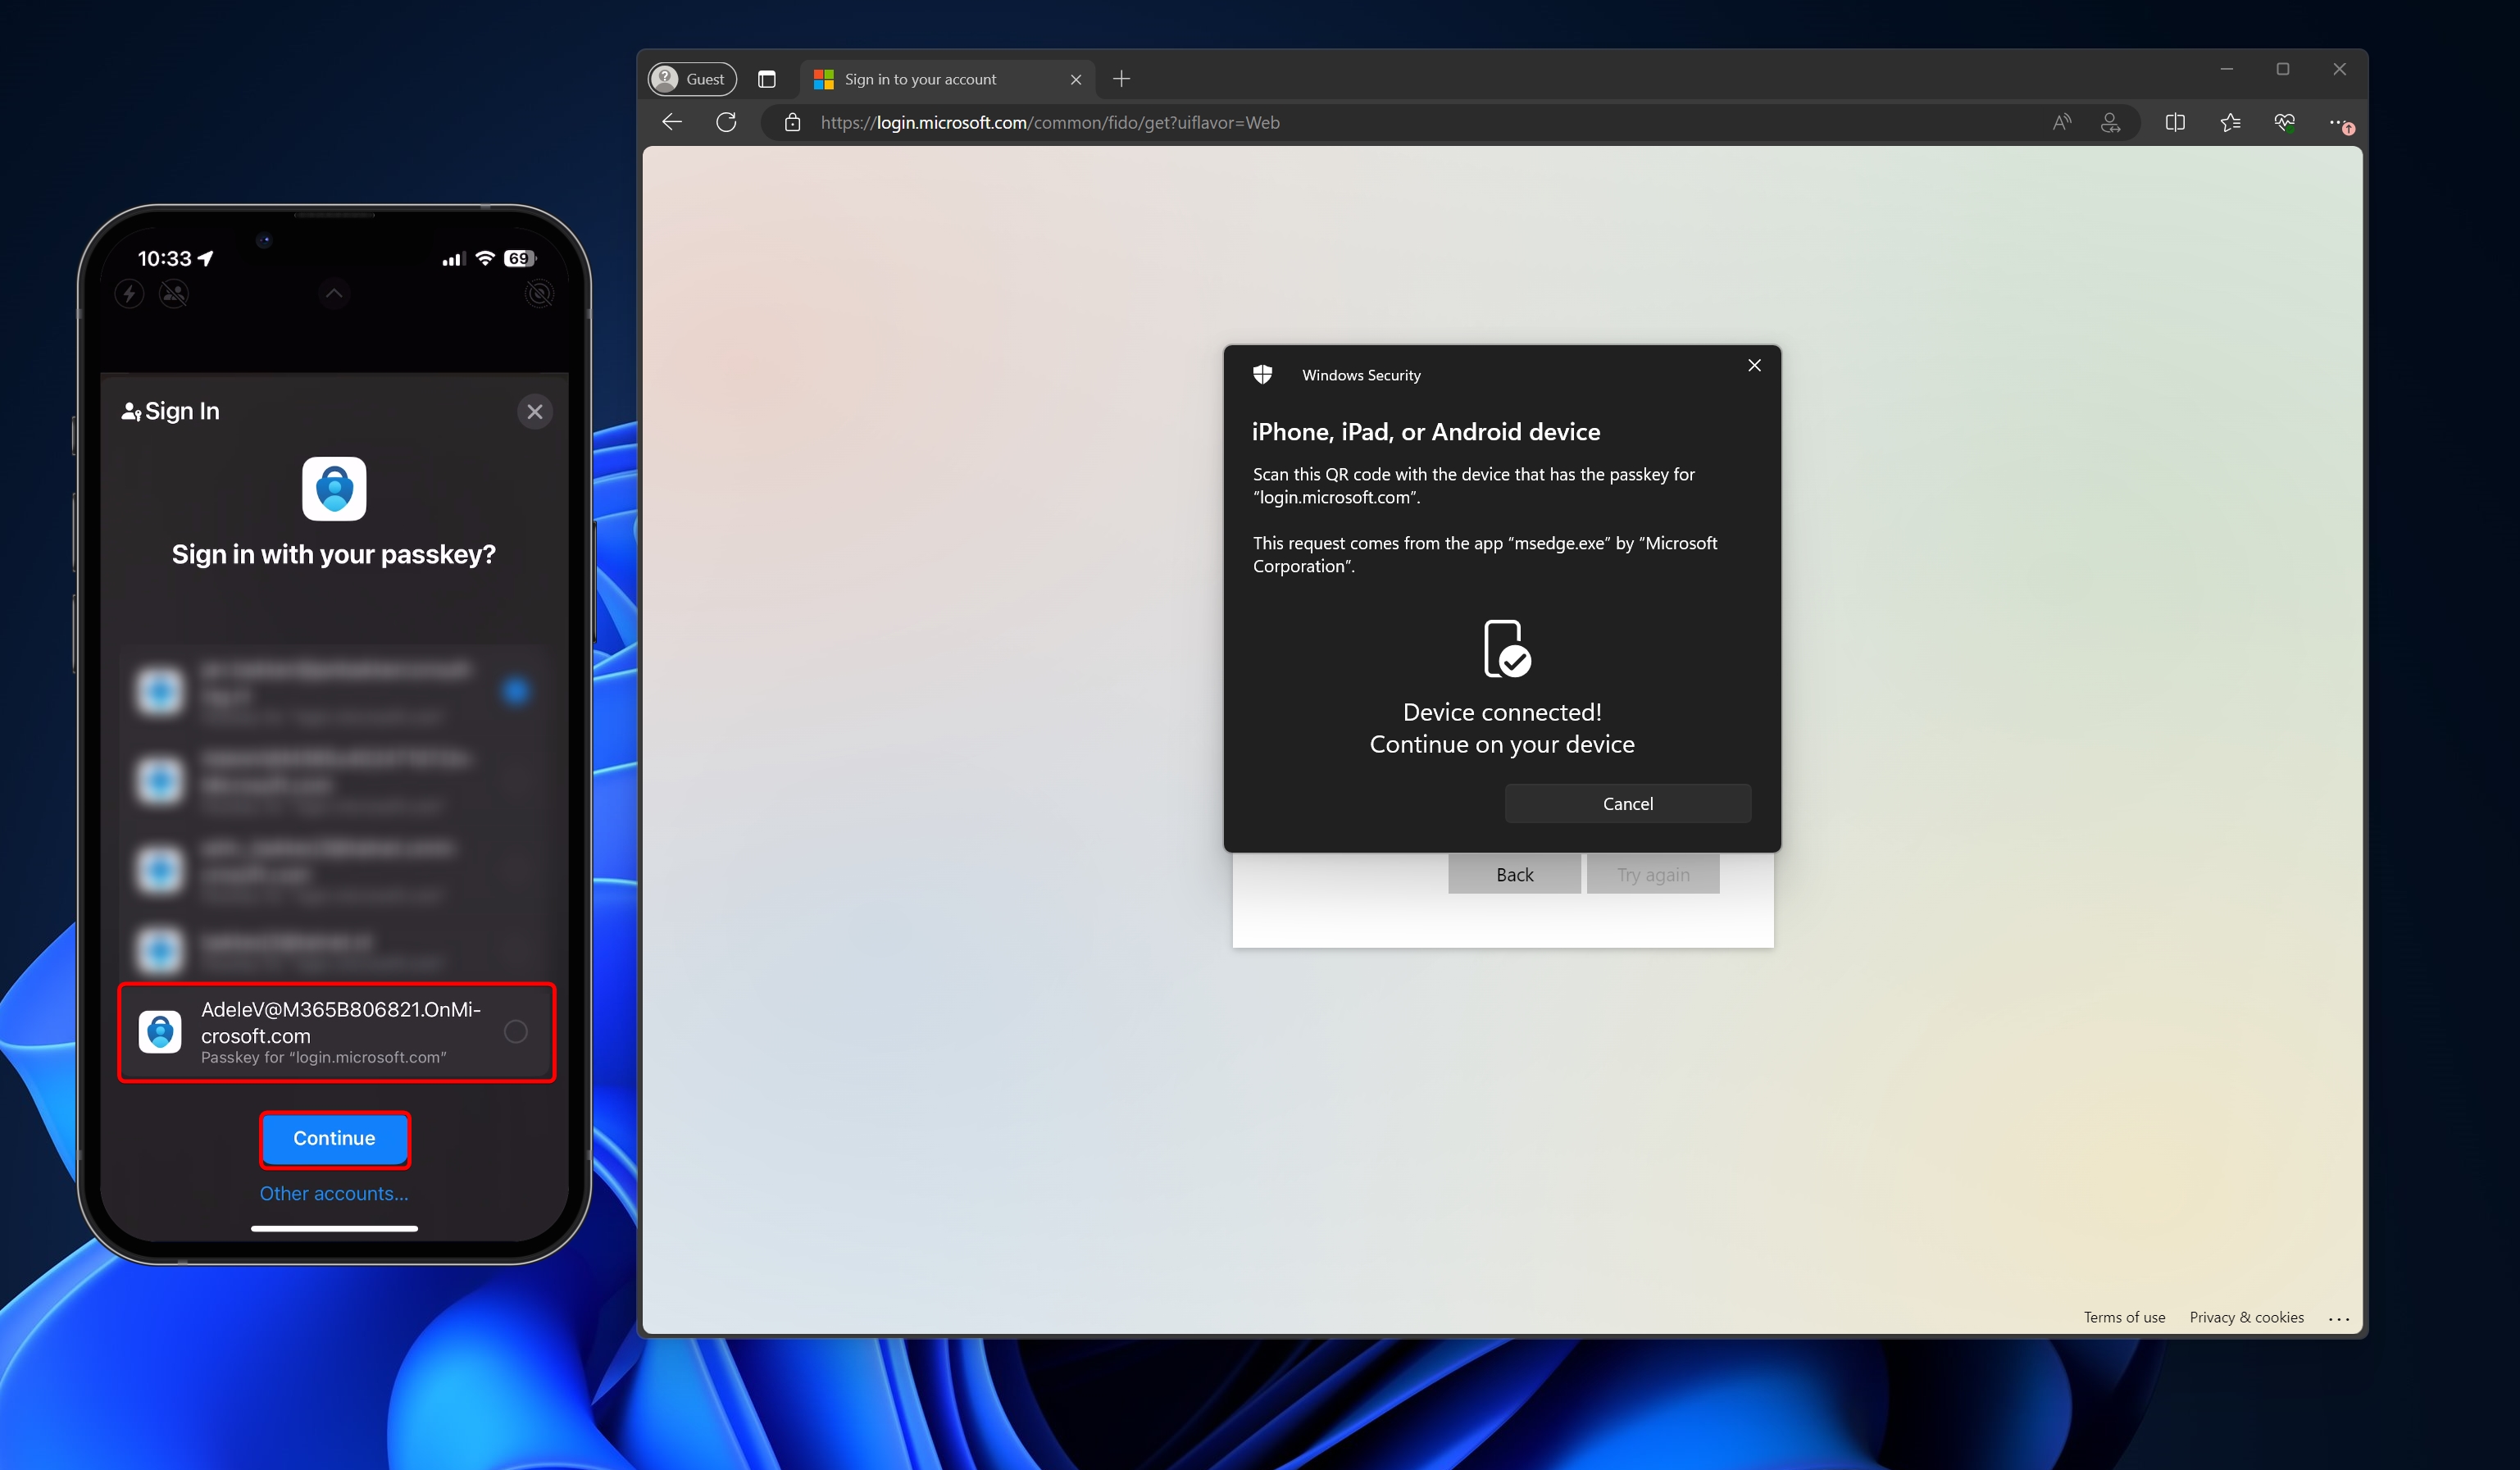
Next, the device will connect over Bluetooth. After the device is connected, you will be prompted with your passkeys. Click Continue to sign in with the passkey of your choice.
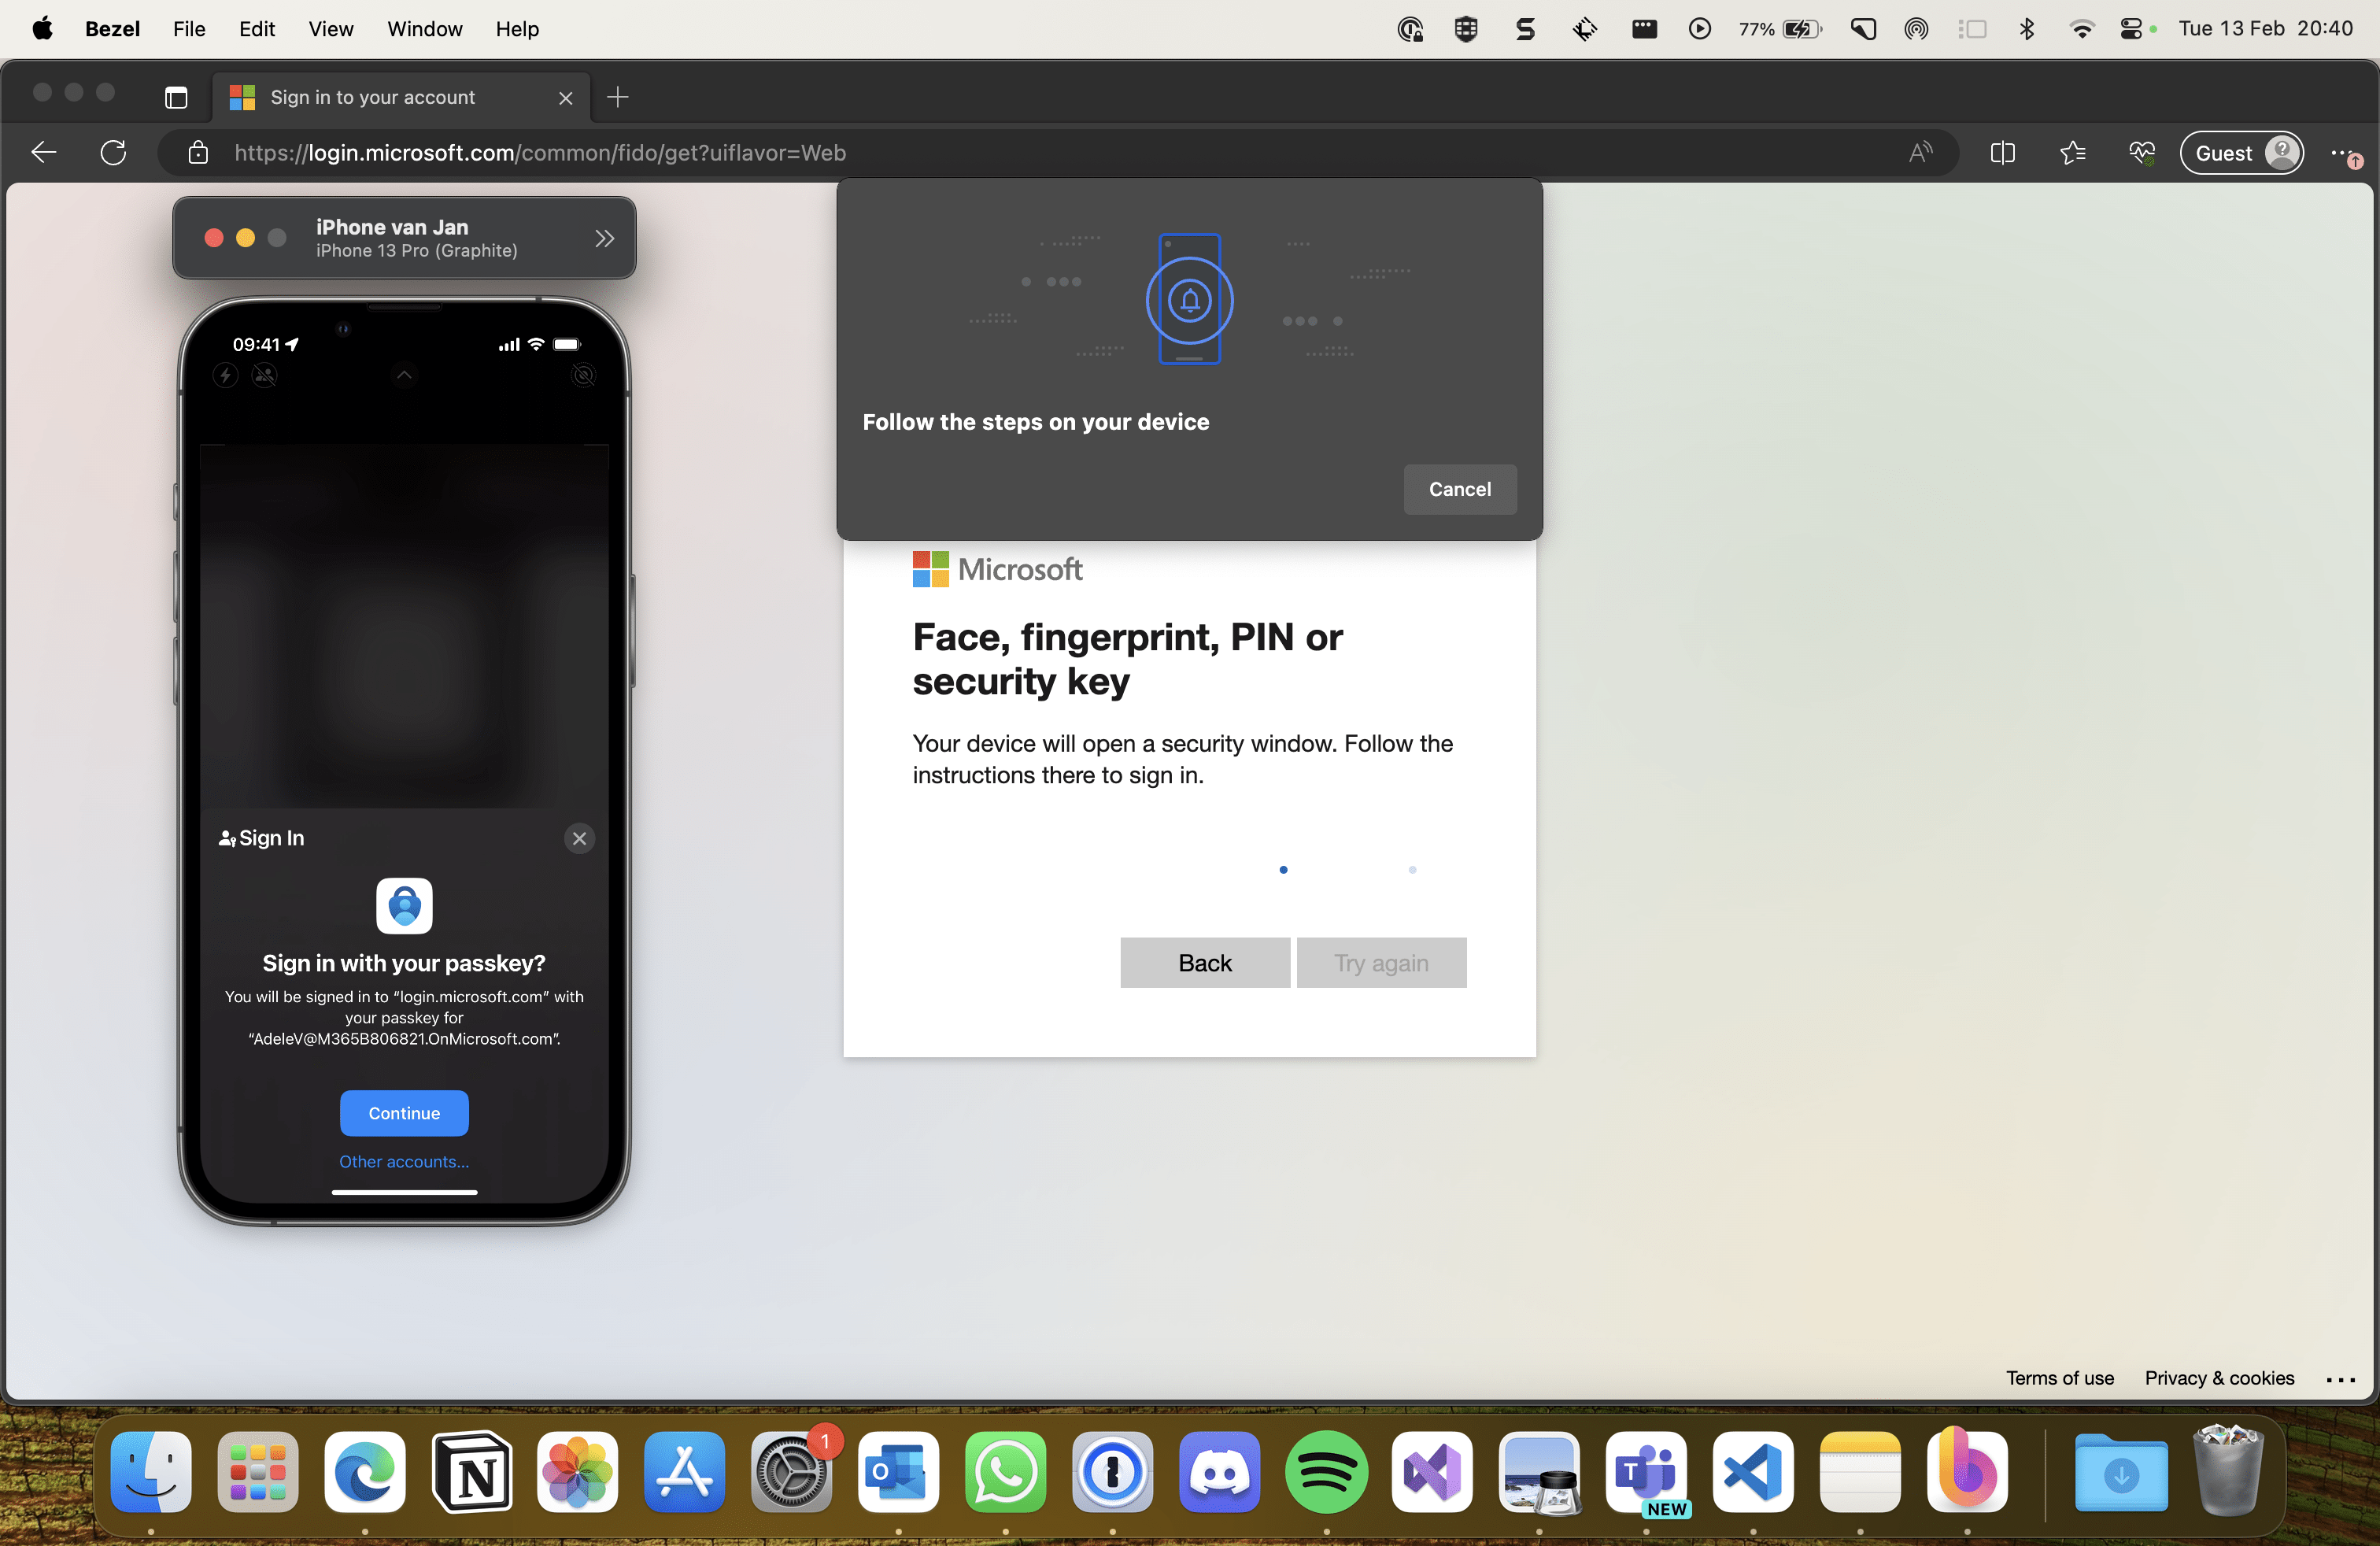
Cross-device user experience - macOS#
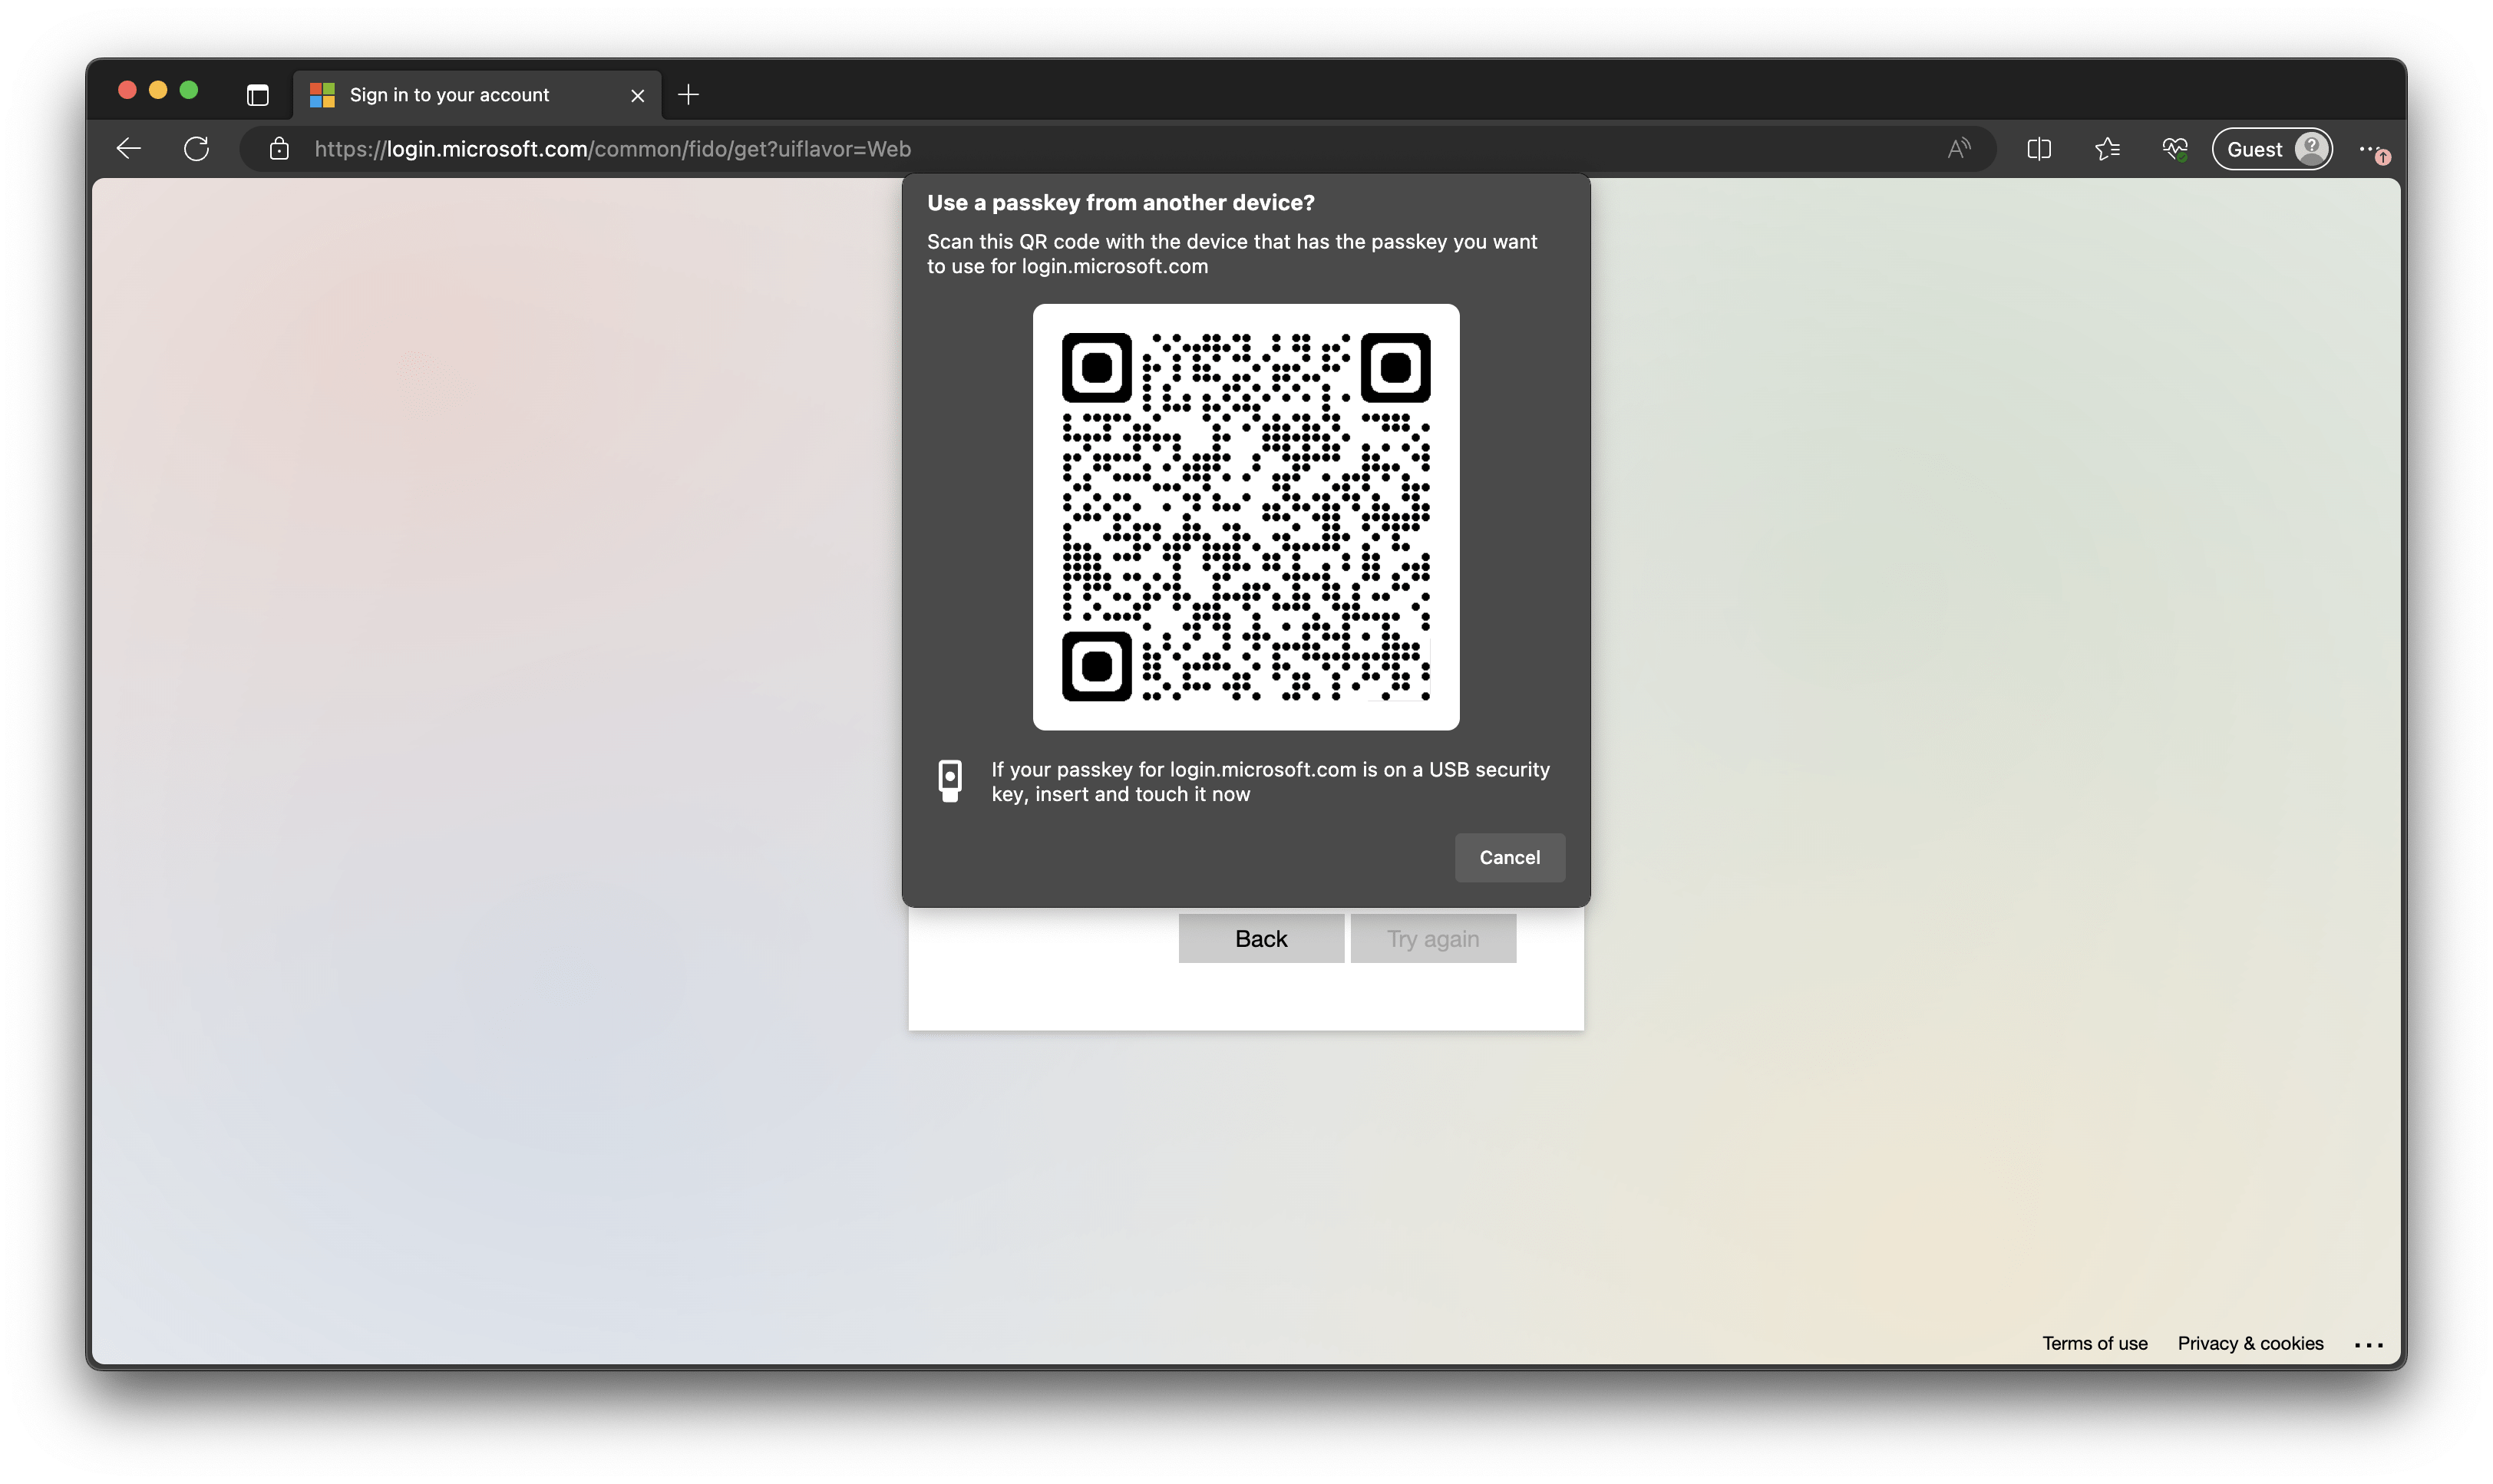
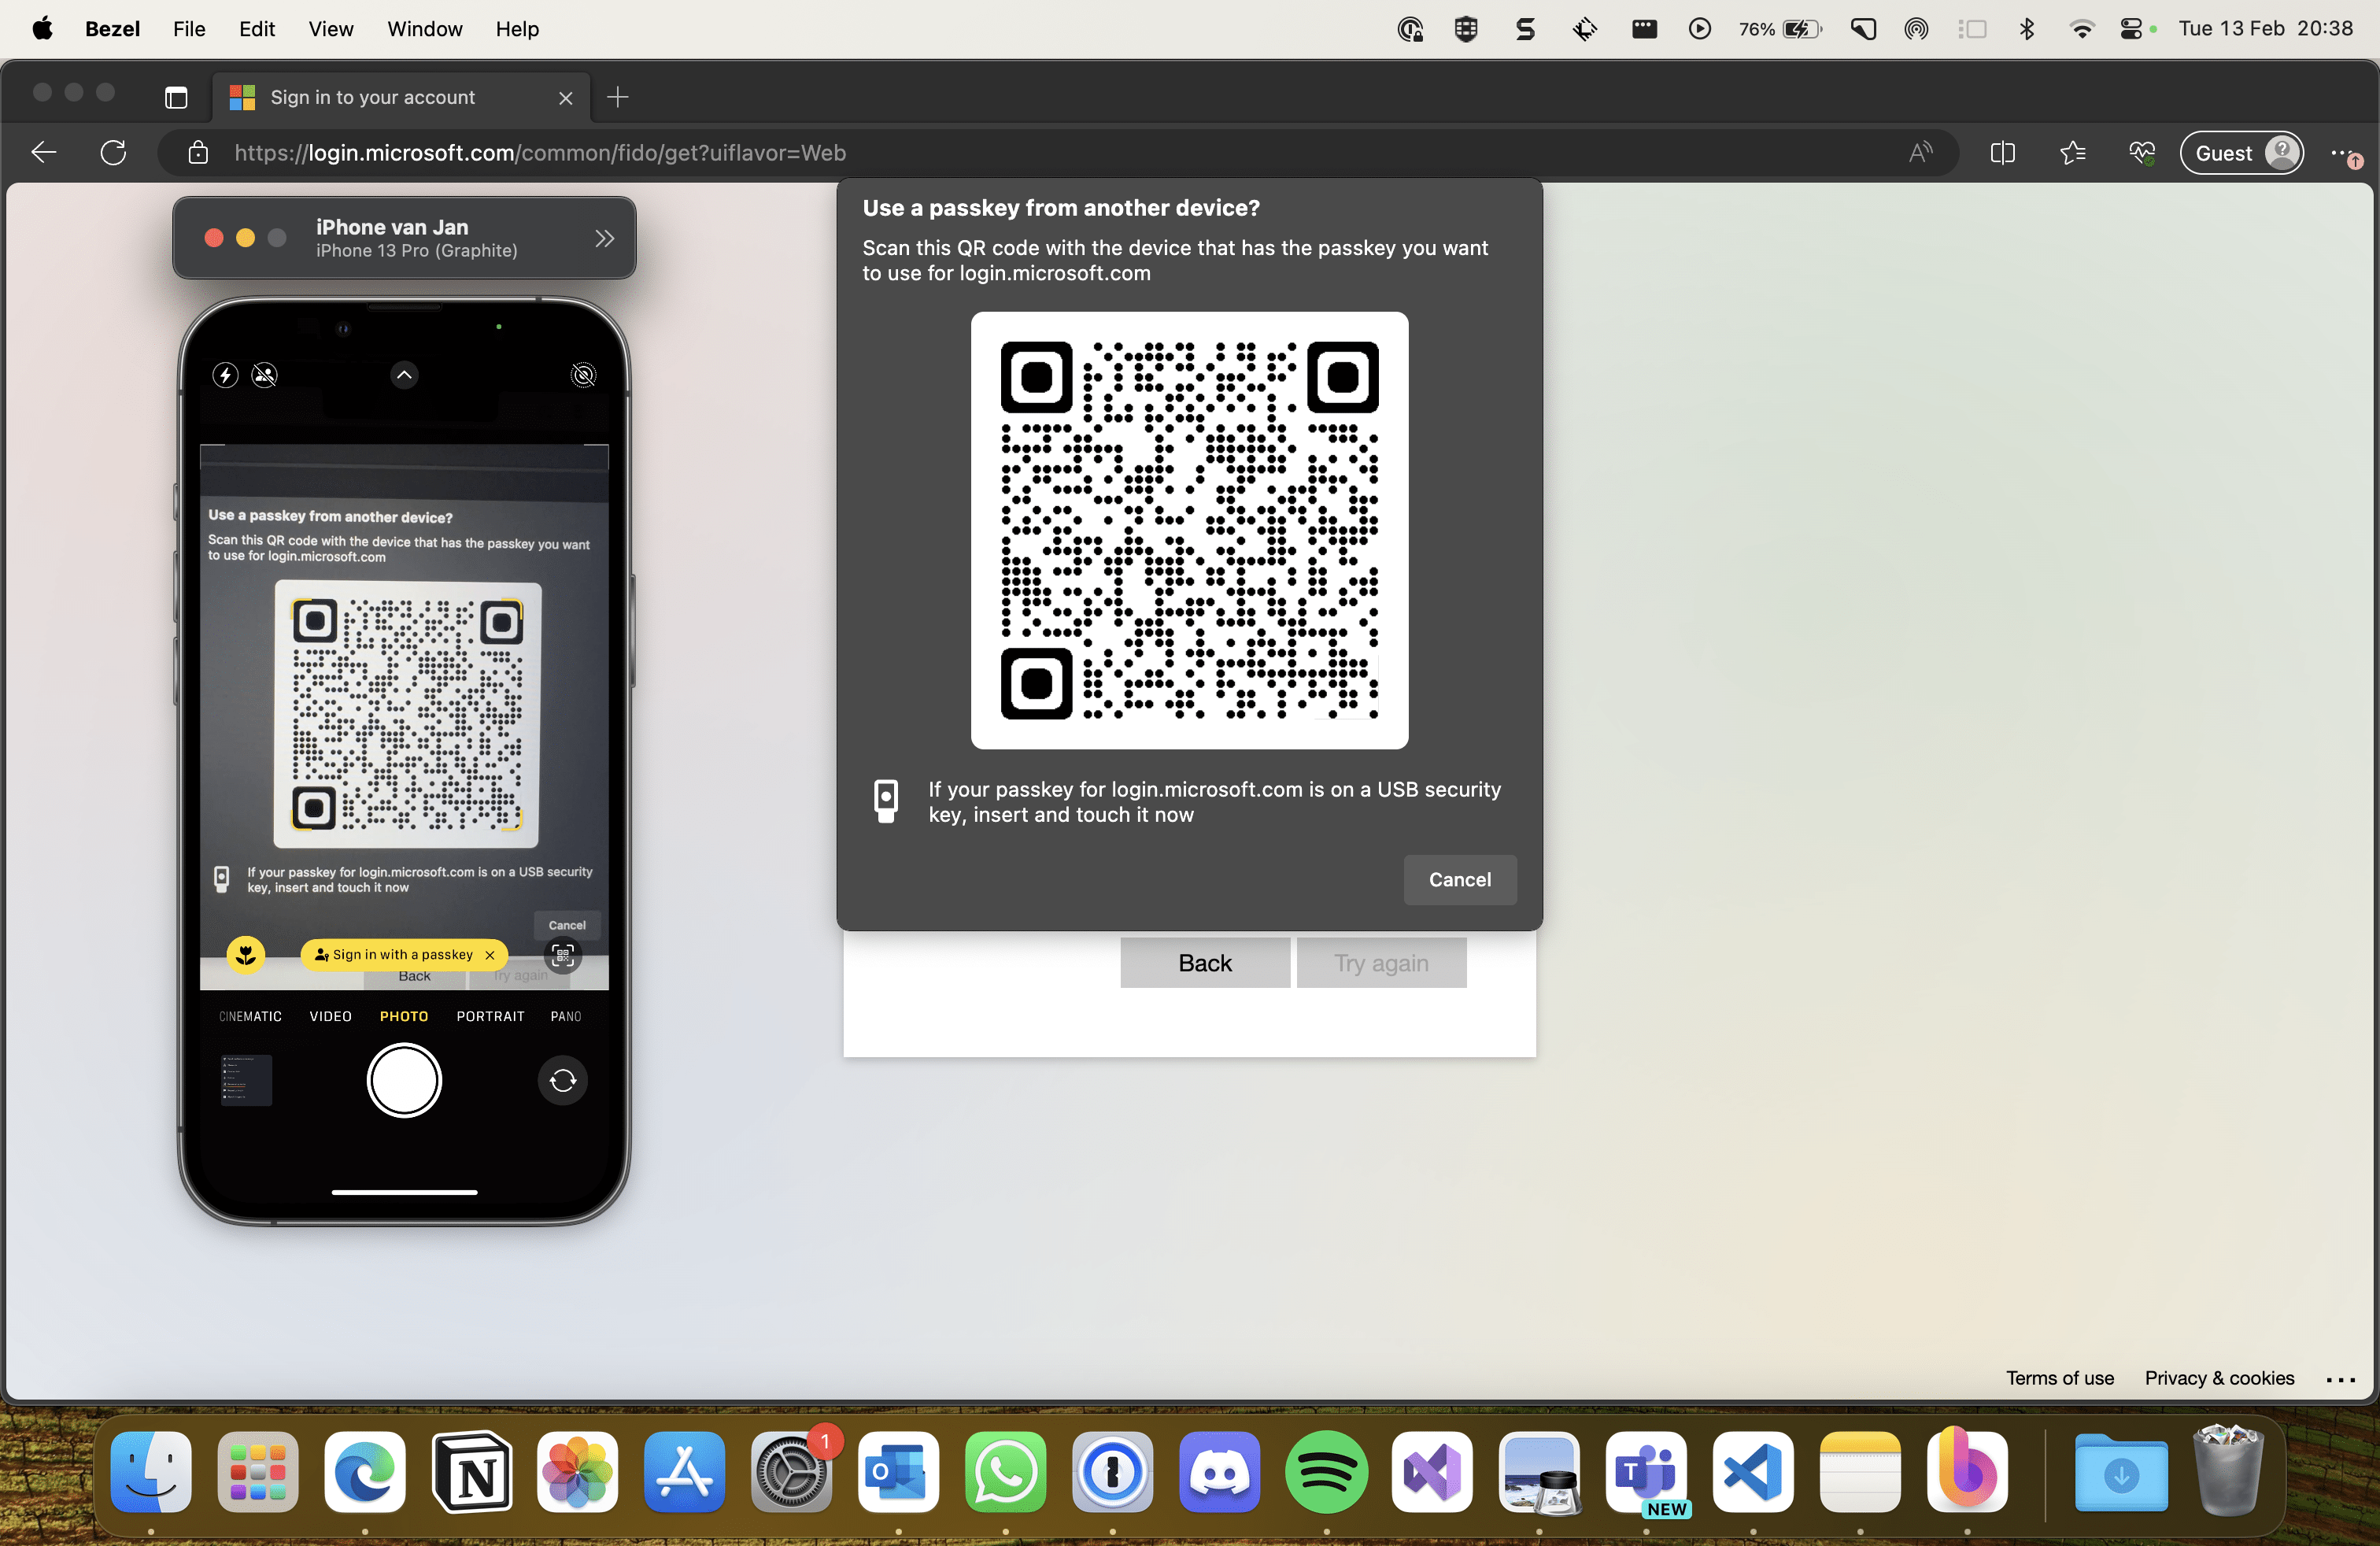
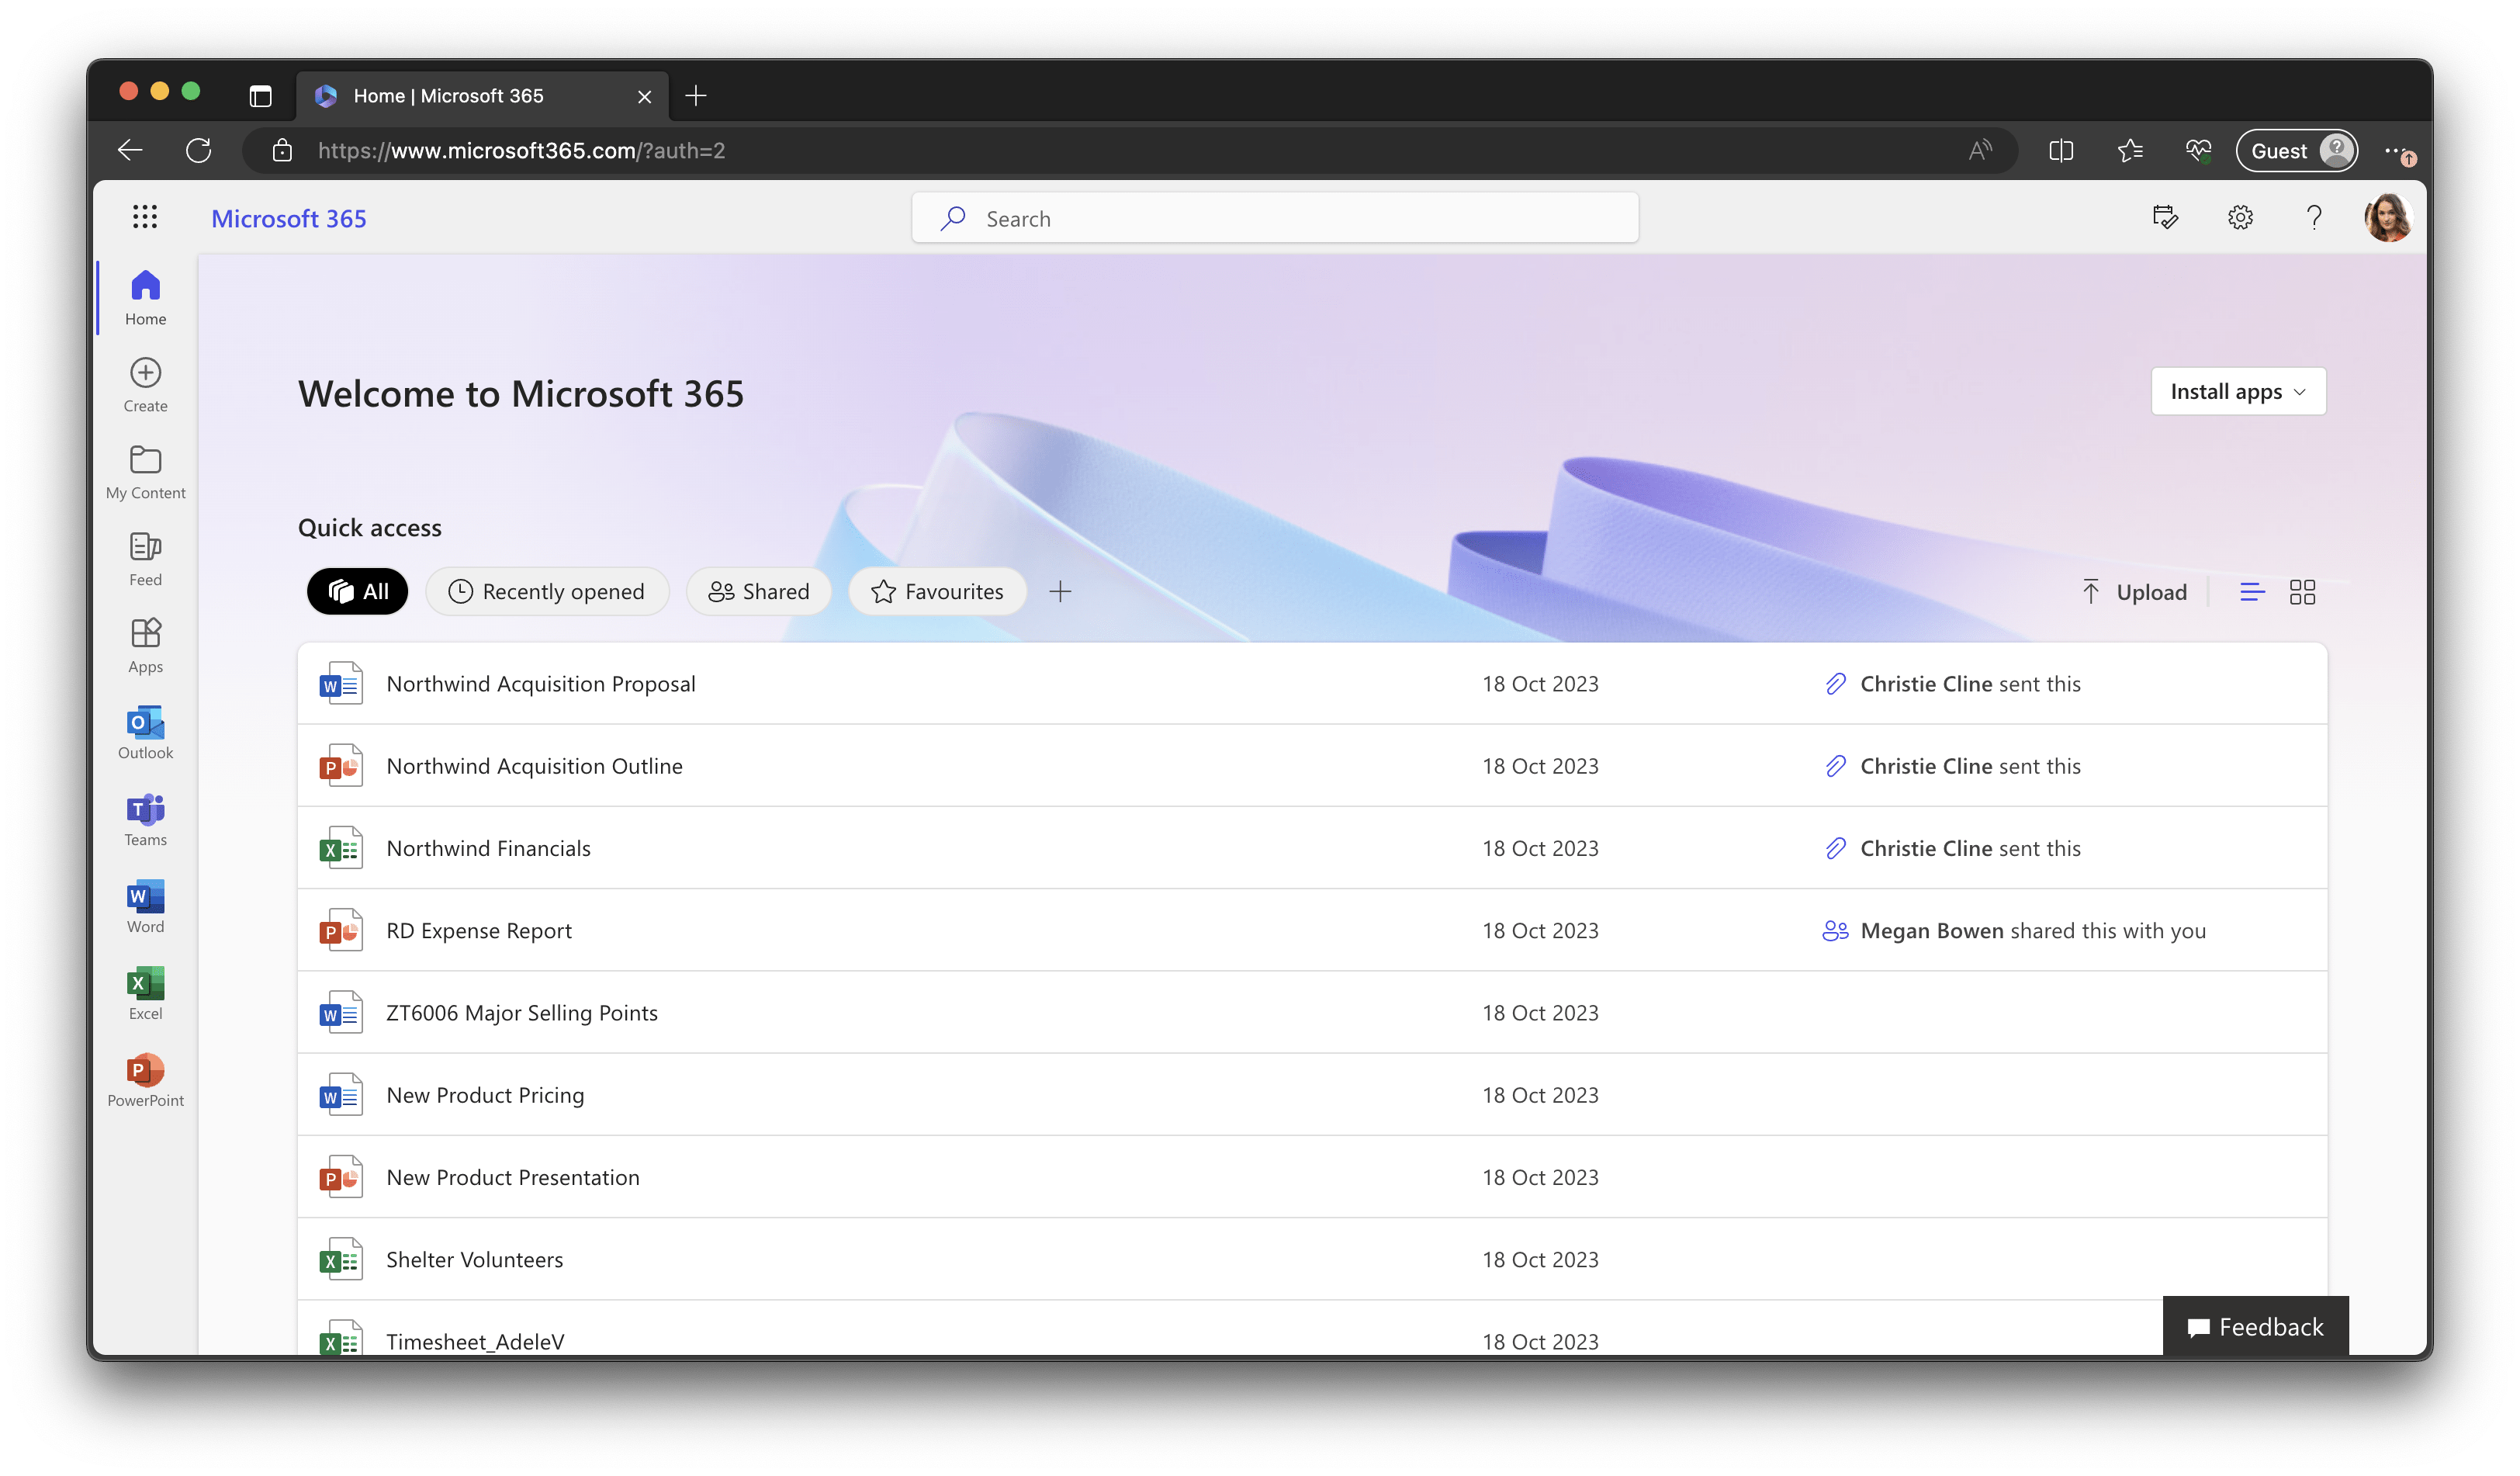
Here’s a quick overview of the experience on MacOS. To be honest, I like this better than Windows. It’s straightforward, and I like the fact they combined the QR code interface to also support physical (USB) passkeys.
Keep track#
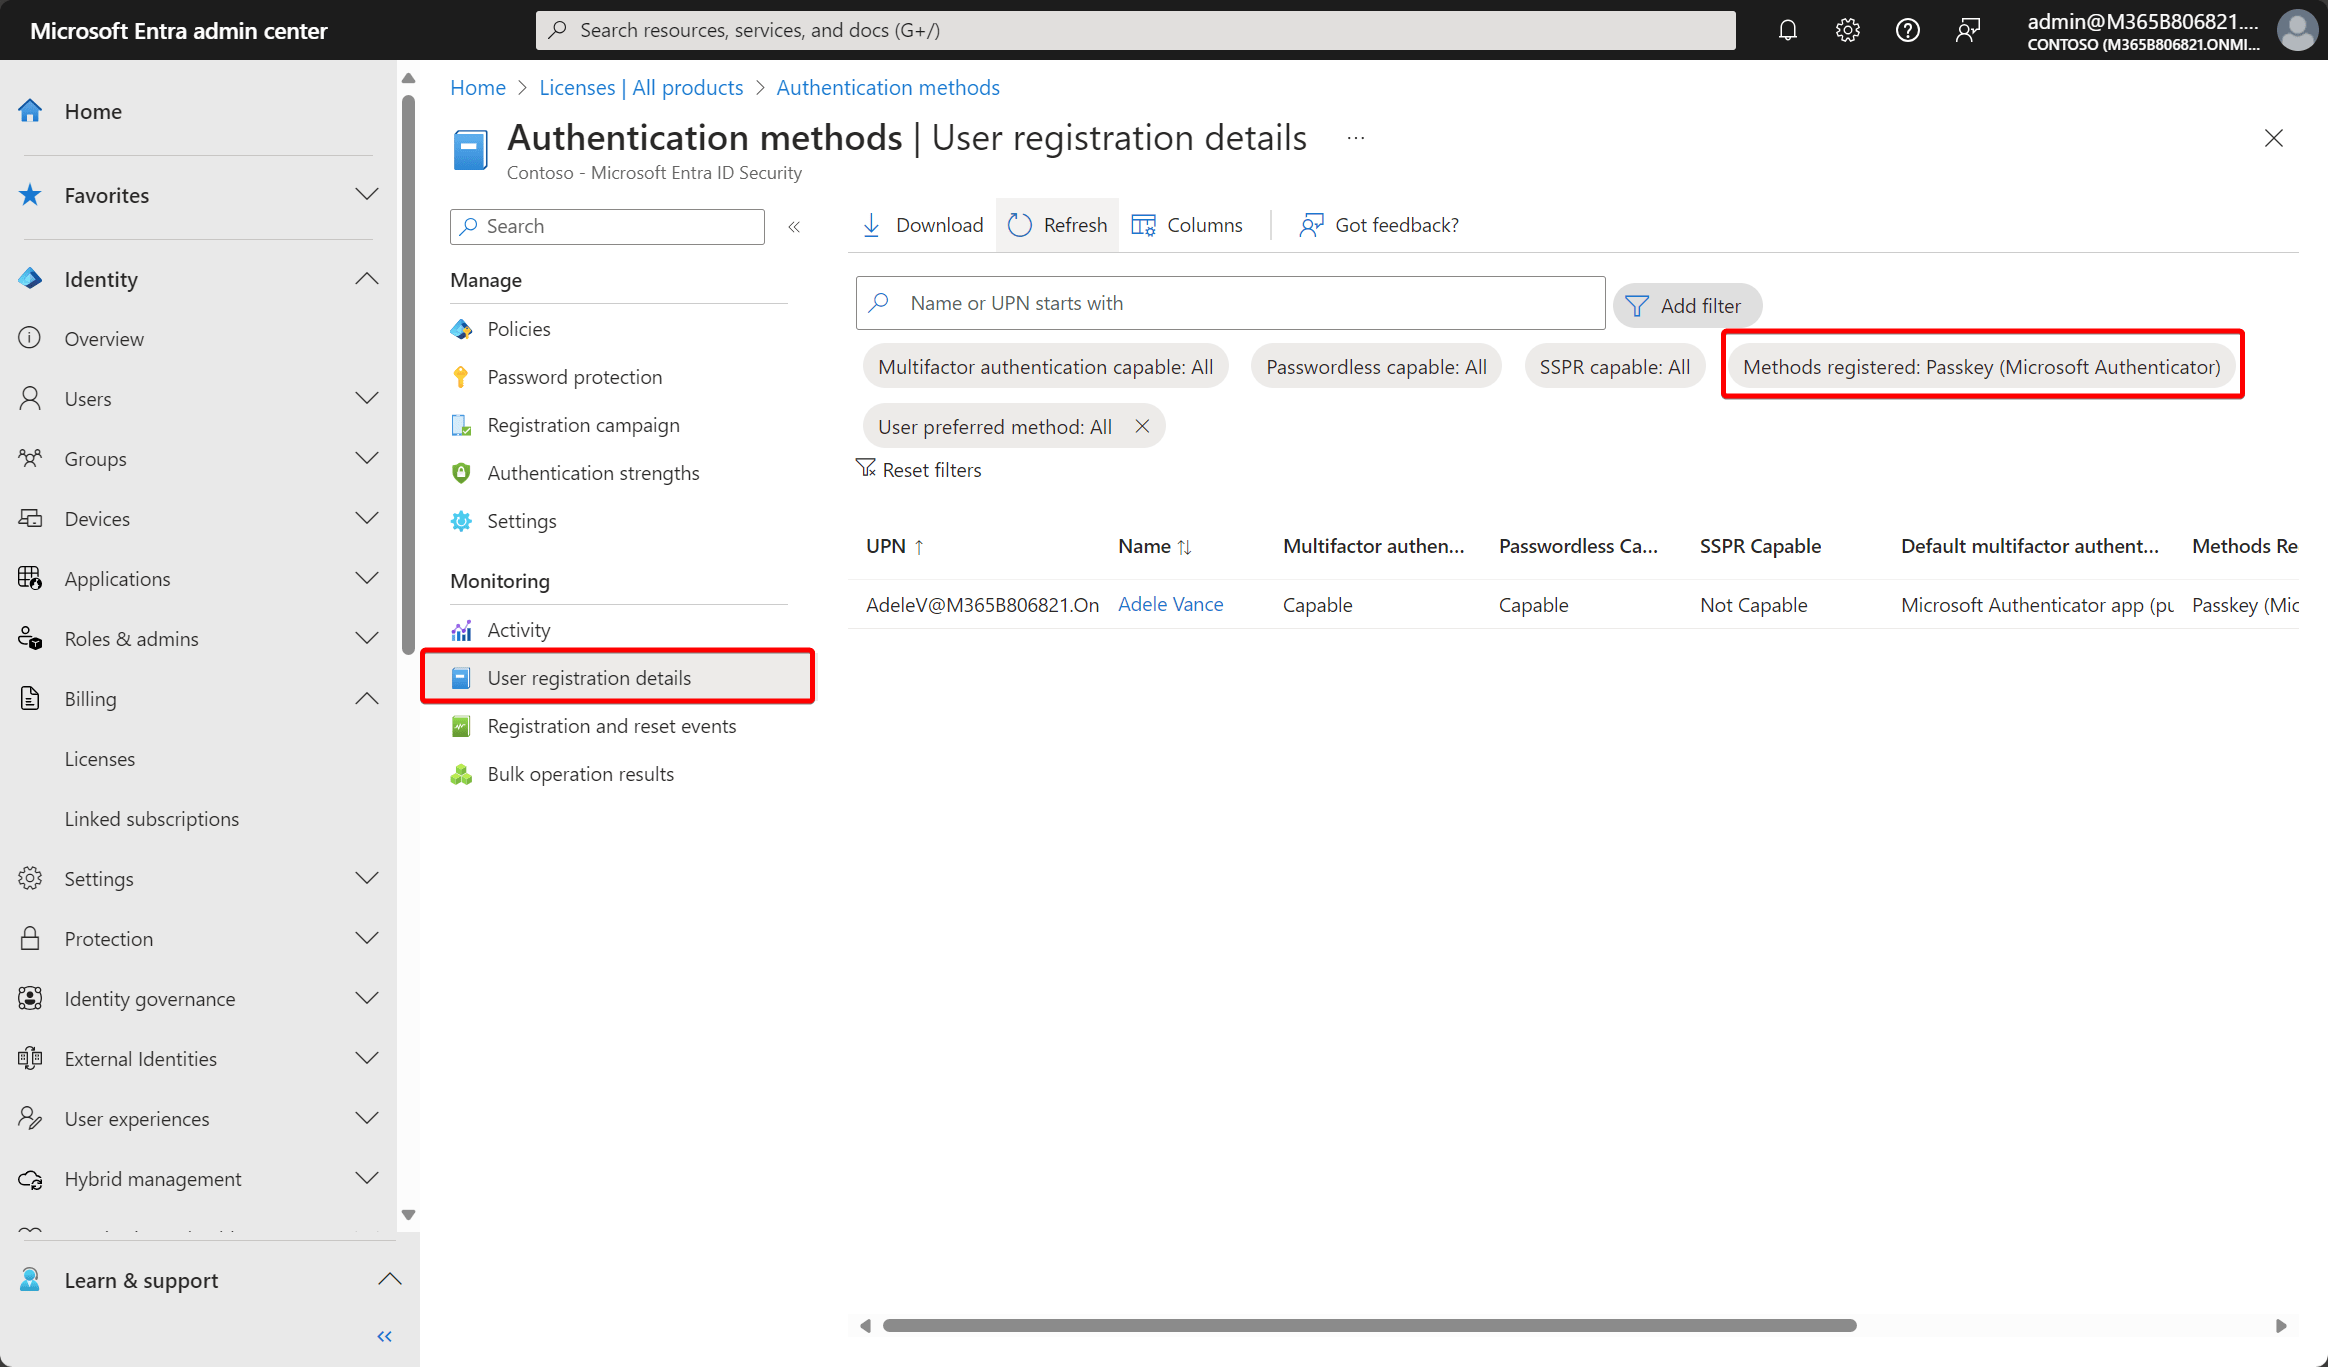
To keep track of the registration of device-bound passkeys, you can check the User registration details report in the Microsoft Entra admin center.
If you are using Log Analytics or Sentinel, use this KQL query (credits to Steven Lim):
AuditLogs
| where ActivityDisplayName == "Add Passkey (device-bound) security key"
| where Result == "success"
| extend AccountUPN = TargetResources[0].userPrincipalName
| extend AAGUID = AdditionalDetails[1].value
| extend WebAuthnInfo = AdditionalDetails[0].value
| project TimeGenerated, AccountUPN, ActivityDisplayName, AAGUID, WebAuthnInfo
Wrap things up#
Overall, I’m really happy that Microsoft now supports passkeys for Microsoft 365 and Entra ID-integrated apps and services, but there is still a long way to go. First of all, there is adoption. We need to educate our users on what passkeys are, why they are more secure than ever, and how to use them over various platforms. Next, vendors need to put in extra effort to optimize the user experience, especially the Windows team themselves. They need to sit down with the identity folks and think about better integration with the operation system and the current passkey features like Windows Hello. For now, it’s just too many clicks and too messy. The experience on macOS is already much cleaner, so perhaps they should visit their friends at Apple sometime.
All jokes aside, phishing resistance is here to stay, and it is now available for everyone! Please share your (constructive) feedback to improve the feature over time. It might take a few months for GA, but until then, make sure to start a pilot on passkeys. You might start with your admins if they still use “legacy” MFA to protect the most desirable accounts in your tenant.
Resources:
How to enable Microsoft Authenticator passkey sign in for Microsoft Entra ID (preview) - Microsoft Entra ID | Microsoft Learn
How to enable Passkeys for the Microsoft Authenticator app (ourcloudnetwork.com)
Passkey Public Preview for Entra ID - Cloudbrothers
Bluetooth Passkeys: Cross-Platform Authentication | Medium
Glossary - Learn About Passkeys and WebAuthn (corbado.com)
Stay safe!\
Comments
Comments load when you scroll here.