Unlocking the Power of employeeHireDate in Entra ID Dynamic Groups
Disclaimer: The main structure of this blog post is created by Claude 3.7 Sonnet. Together with Lokka, I figured out all the supported operators by testing all…
Category
Disclaimer: The main structure of this blog post is created by Claude 3.7 Sonnet. Together with Lokka, I figured out all the supported operators by testing all…
In an earlier post, I showed several ways to (bulk) provision Yubikeys (or keys from other vendors) in Microsoft Entra using the provisioning APIs. In this…
For good reasons, device code flow in Entra ID is getting a lot of attention. Attackers heavily use it to get access to Microsoft 365 accounts and data. Device…
Evilginx is known for capturing user cookies, even if they are secured by MFA methods like SMS, TOTP, push notifications or passwordless phone sign-in. In…
As passkeys get more traction in Microsoft 365, more and more companies are looking to strengthen their identity posture by enrolling passkeys for their…
Microsoft Entra ID Protection and Microsoft Entra Conditional Access work well together. If your organization owns an Entra Premium P2 license, you likely have…
Today's post is about a new feature in Entra ID's Identity Governance: Show suggested access packages in My Access.
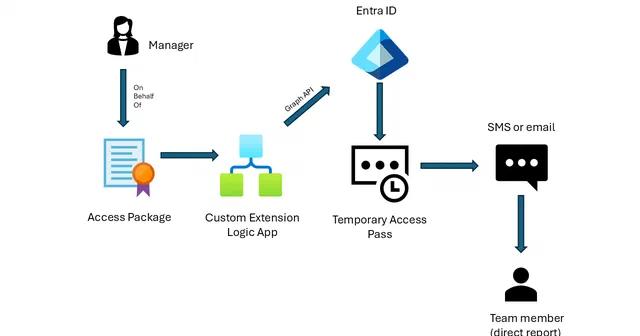
In a previous blog post, I explained a proof of concept in which we use Entra ID Governance Access Packages to request a Temporary Access Pass on behalf of…
While looking at this new feature (Request access packages on-behalf-of other users (Preview) - Microsoft Entra ID Governance | Microsoft Learn), an…
One of the longest-running previews in Entra ID is the support for hardware (OATH) tokens. Hardware tokens can create OTP tokens that can be used to satisfy…
Microsoft recently announced their new FIDO2 provisioning APIs within Microsoft Entra ID. While users can register their FIDO2 keys fairly easily with a…
In case you didn't get the latest memo, Microsoft is tightening the security around the Azure and Microsoft 365 admin portals by enforcing multifactor…